
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

200,000 Comcast login credentials available on the Dark Web

During the weekend, nearly 590,000 Comcast email addresses and passwords were offered for sale on a BlackMarket in the dark web. It is now the turn of Comcast, over the weekend nearly 590,000 Comcast email addresses and passwords were offered for sale on a BlackMarket in the dark web. As proof of the authenticity of the […]

Comcast

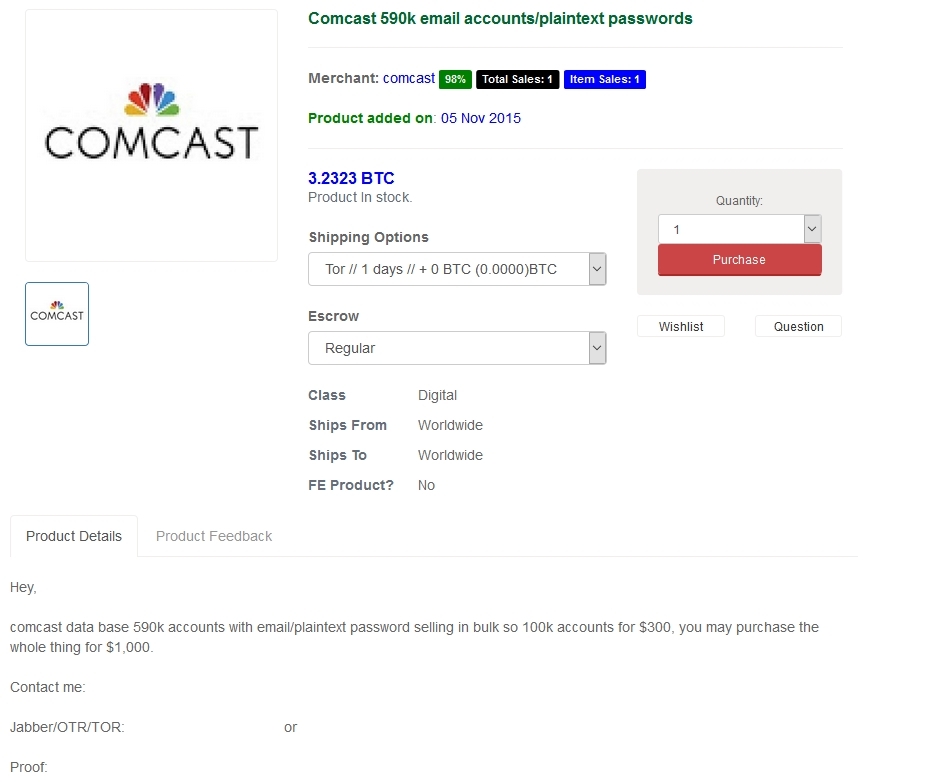
During the weekend, nearly 590,000 Comcast email addresses and passwords were offered for sale on a BlackMarket in the dark web.

It is now the turn of Comcast, over the weekend nearly 590,000 Comcast email addresses and passwords were offered for sale on a BlackMarket in the dark web. As proof of the authenticity of the Comcast data, the seller published a list of 112 accounts requesting 300 USD for 100,000 accounts, the entire list of 590,000 accounts goes for $1,000 USD.

The discovery of the singular sale was made first by an individual owning the Twitter account @flanvel, which promptly contacted Salted Hash to report it the news.

Comcast was in possession of the list and it was checking the leaked data, it seems that of the 590,000 records offered for sale on the black marketplace about 200,000 of them were still active.
comcast darkweb

Although they represent a minor part of the bulk data sold by crooks,  we can not overlook the fact that the credentials offered could be used to take over the Comcast  accounts.

According to the Comcast security team, the systems of the company have not been compromised, every user that will report suspicious activity on his account will be contacted singularly to solve the issue.

It is likely that the data still active and valid comes from a collection of data resulting from other data breaches, they are almost certainly recycled.

Online it is quite easy to find collections of data that come from malware-based attacks, data breaches, and phishing attacks. Unfortunately, users have the bad habit of sharing the same login credentials among different services online, when one of them is compromised attackers can access all the other web services.

In the specific case the list of Comcast login credentials was circulating online since last week, it is likely someone decided to offer it for sale.

Summarizing Comcast wasn’t the victim of a data breach, the company has reset nearly 200,000 passwords after customer list was discovered.

Pierluigi Paganini

(Security Affairs – Comcast, Dark Web)


