
Security Affairs
Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

2017 OWASP Top 10 is out, you can submit your comment until June

The Open Web Application Security Project (OWASP) presented the first release candidate for the 2017 OWASP Top 10, it includes 2 new categories. This week the Open Web Application Security Project (OWASP) presented the first release candidate for the 2017 OWASP Top 10, the principal novelty is the presence of two new vulnerability categories. The […]

2017 OWASP Top 10 is out, you can submit your comment until June

The Open Web Application Security Project (OWASP) presented the first release candidate for the 2017 OWASP Top 10, it includes 2 new categories.

This week the Open Web Application Security Project (OWASP) presented the first release candidate for the 2017 OWASP Top 10, the principal novelty is the presence of two new vulnerability categories.

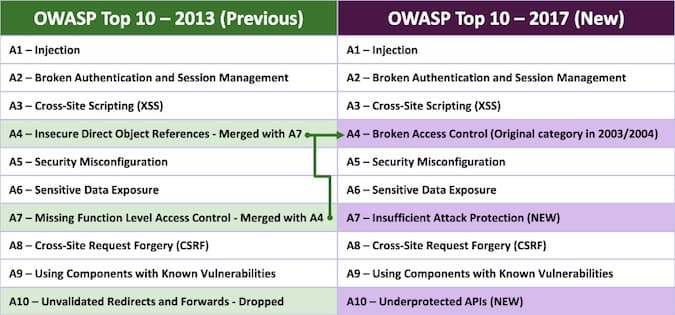
The new categories introduced for OWASP Top 10 – 2017:

  • “insufficient attack detection and prevention”
  • “unprotected APIs.”

The 2017 OWASP Top 10 misses the “unvalidated redirects and forwards,” that was the 10th item on the current list dated back 2013.

The “insufficient attack detection and prevention” results from the merger of the current 4th and 7th items, “Insecure direct object references” and the “Missing Function Level Access Control.”

The categories have been merged into the item “Broken access control” that was dated back in 2004.

2017 OWASP Top 10

Below the description provided by OWASP for the new categories:

“Insufficient attack protection“: “The majority of applications and APIs lack the basic ability to detect, prevent, and respond to both manual and automated attacks. Attack protection goes far beyond basic input validation and involves automatically detecting, logging, responding, and even blocking exploit attempts. Application owners also need to be able to deploy patches quickly to protect against attacks.”

“Unprotected APIs”: “Modern applications often involve rich client applications and APIs, such as JavaScript in the browser and mobile apps, that connect to an API of some kind (SOAP/XML, REST/JSON, RPC, GWT, etc.). These APIs are often unprotected and contain numerous vulnerabilities.”

Security experts, developers, and users can submit comments on the 2017 OWASP Top 10 proposal via email until June 30 to OWASP-TopTen(at)lists.owasp.org, or dave.wichers(at)owasp.org (for private comments).

The final version of the 2017 OWASP Top 10 is expected to be released next summer.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – 2017 OWASP Top 10, Application Security)

[adrotate banner=”13″]


