
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

2017 OWASP Top 10 Final Release is out, what’s new?

The Open Web Application Security Project (OWASP) presented the final release for the 2017 OWASP Top 10. The Open Web Application Security Project (OWASP) published the final version of the 2017 OWASP Top 10. In April, the OWASP announced the first release candidate for the 2017 OWASP Top 10, the main novelty was represented by the presence […]

2017 OWASP Top 10 Final

The Open Web Application Security Project (OWASP) presented the final release for the 2017 OWASP Top 10.

The Open Web Application Security Project (OWASP) published the final version of the 2017 OWASP Top 10. In April, the OWASP announced the first release candidate for the 2017 OWASP Top 10, the main novelty was represented by the presence of the following two new vulnerability categories.

  • “insufficient attack detection and prevention”
  • “unprotected APIs.”

The 2017 OWASP Top 10 is based on data from 23 contributors covering more than 114,000 applications. OWASP published on GitHub the data used for its report.

The categories have been selected based on the risk they pose, but what are the application Security Risks?

“Attackers can potentially use many different paths through your application to do harm to your business or organization. Each of these paths represents a risk that may, or may not, be serious enough to warrant attention.” states the OWASP.

“Sometimes these paths are trivial to find and exploit, and sometimes they are extremely difficult. “

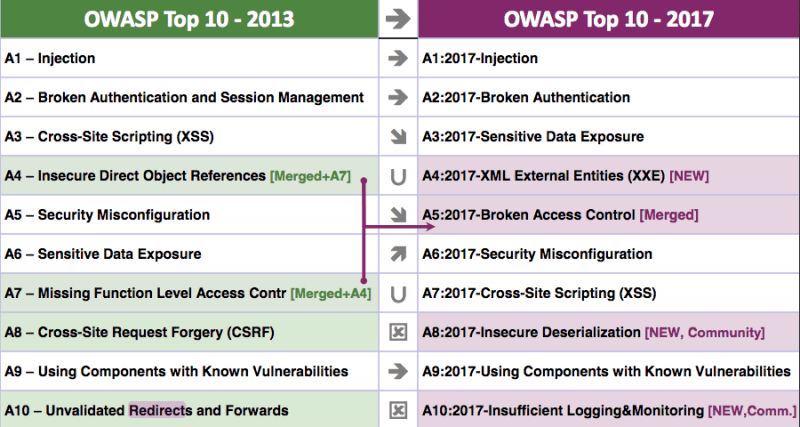
The OWASP Top 10 vulnerabilities are injection, broken authentication, sensitive data exposure, XML external entity (XXE), broken access control, security misconfiguration, cross-site scripting (XSS), insecure deserialization, using components with known vulnerabilities, and insufficient logging and monitoring.

The “insufficient attack detection and prevention” results from the merger of the current 4th and 7th items, “Insecure direct object references” and the “Missing Function Level Access Control.”

The categories have been merged into the item “Broken access control” that was dated back in 2004.
2017 OWASP Top 10 Final

The OWASP left the Cross-Site Scripting (XSS) in a separate category, while it removed the Cross-site request forgery (CSRF) because it is addressed by as modern development frameworks. It was found that the CSRF affected less than 5% of applications, meanwhile Unvalidated redirects and forwards has been found in around 8% of apps and for this reason it was removed too.

News entries are XXE, insecure deserialization, and insufficient logging and monitoring, this latter represents a serious problem for many organizations.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – 2017 OWASP Top 10, Application Security)

[adrotate banner=”5″]

[adrotate banner=”13″]


