
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts discover over 451 clipper malware-laced packages in the PyPI repository

Threat actors published more than 451 unique malware-laced Python packages on the official Python Package Index (PyPI) repository. Phylum researchers spotted more than 451 unique Python packages on the official Python Package Index (PyPI) repository in an attempt to deliver clipper malware on the developer systems. According to the experts, the activity is still ongoing […]

clipper malware

Threat actors published more than 451 unique malware-laced Python packages on the official Python Package Index (PyPI) repository.

Phylum researchers spotted more than 451 unique Python packages on the official Python Package Index (PyPI) repository in an attempt to deliver clipper malware on the developer systems.

According to the experts, the activity is still ongoing and is part of a malicious campaign that they discovered on November 2022.

Threat actors have typosquatted several major packages in PyPI such as:

  • bitcoinlib
  • ccxt
  • cryptocompare
  • cryptofeed
  • freqtrade
  • selenium
  • solana
  • vyper
  • websockets
  • yfinance
  • pandas
  • matplotlib
  • aiohttp
  • beautifulsoup
  • tensorflow
  • selenium
  • scrapy
  • colorama
  • scikit-learn
  • pytorch
  • pygame
  • pyinstaller

The researchers reported that the attackers are trying to register the same code in every possible simple typo of a package name. The process is simple and easy to automate.

Phylum pointed out that the obfuscation technique used in these packages is significantly different from the packages they have spotted in November 2022. 

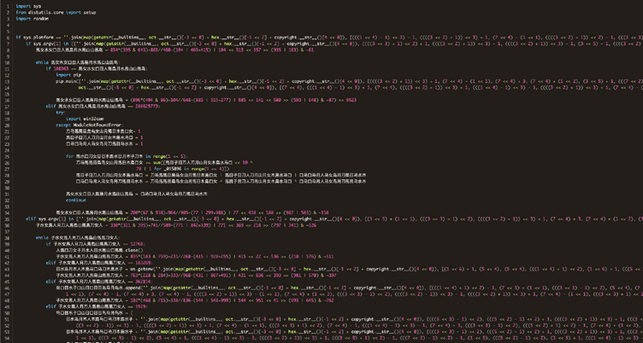
Upon installing a malicious package, a JavaScript file is dropped to the system and executed in the background of any web browsing session allowing to replace a cryptocurrency address with the attacker’s address every time a developer copies it.

“Ultimately, this code is attempting to do exactly what we discovered in November’s blog post and that is quietly replace any crypto wallet address copied to the user’s clipboard with the attacker’s controlled wallet addresses.” reads the analysis published by Phylum. “It does that by creating a browser extension and then writes the following JavaScript to that extension:”

The malware establishes persistence by instructing the developer’s browser(s) to load this extension anytime a browser is opened.

The clipper malware targets popular web browsers, including Google Chrome, Microsoft Edge, Brave, and Opera. The malware modifies browser shortcuts to load the extension by launching the software with “–load-extension” command line.

“This attacker significantly increased their footprint in pypi through automation. Flooding the ecosystem with packages like this will continue.” concludes the report.”The use of Chinese characters, or any other Unicode plane for that matter, is an easy misdirection to detect and to dismiss.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, clipper malware)


