
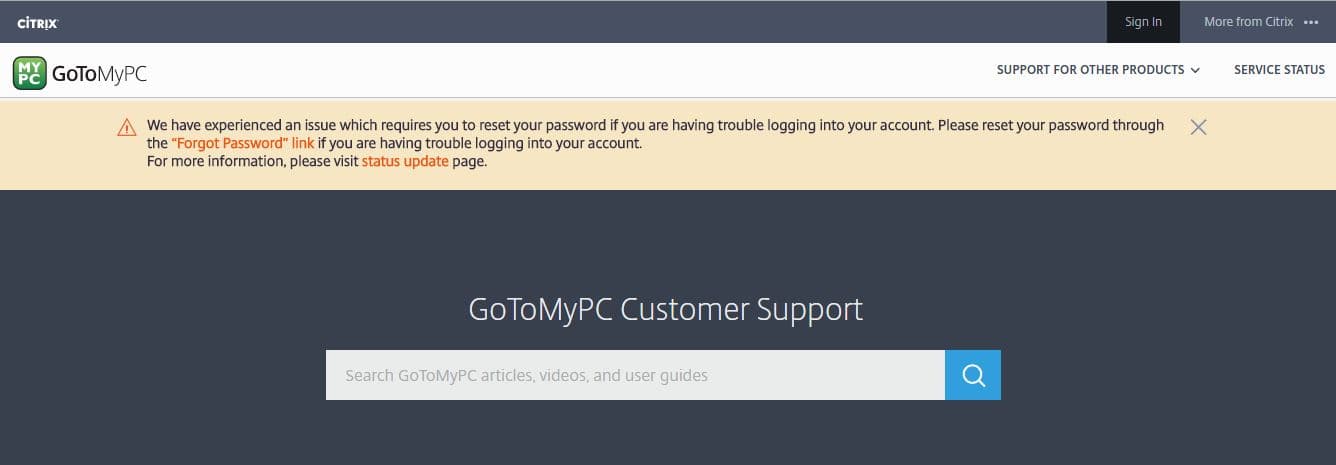
A number of users are experiencing problems during logging into GoToMyPC because Citrix reset account passwords after hackers reportedly attacked it.
It’s official, the GoToMyPC service operated by Citrix is the last victim of the hackers.
GoToMyPC is remote desktop software that allows users to access and control their computers remotely by using a simple web browser.
A number of users are experiencing problems during logging into GoToMyPC because Citrix experts have reset account passwords after unknown hackers reportedly attacked the service.

“Dear Valued Customer,
Unfortunately, the GoToMYPC service has been targeted by a very sophisticated password attack. To protect you, the security team recommended that we reset all customer passwords immediately.” states the security advisory published by GoToMyPC.
“Effective immediately, you will be required to reset your GoToMYPC password before you can login again.
To reset your password please use your regular GoToMYPC login link.
Recommendations for a strong password:
- Don’t use a word from the dictionary
- Select strong passwords that can’t easily be guessed with 8 or more characters
- Make it Complex – Randomly add capital letters, punctuation or symbols
- Substitute numbers for letters that look similar (for example, substitute “0” for “o” or “3” for “E”.”
If you are having issues logging into your account, please visit our service status page for instructions https://t.co/1MBVdkKNFM ^GD
— Citrix GoToMyPC (@GoToMyPC) 18 giugno 2016
The advisory doesn’t include details on the attack, it only describes it a “very sophisticated password attack.”
Now the problem is to understand if hackers breached the GoToMyPC severrs or if the attackers used passwords available online leveraging the bad habit of users in sharing same credentials among various services.
The company is still investigating the case, meantime, let me suggest also to change the password for all those services for which you shared the same credentials.
The incident reminds us the problem recently suffered by TeamViewer, recently many TeamViewer users reported that their systems were accessed by hackers via the popular support tool, but the company denies any incident.
GoToMyPC is suggesting customers to enable two-step verification in order to improve the security of their accounts.
[adrotate banner=”9″]
Security Affairs – (GoToMyPC, Security Breach)


