
Personal information associated with more than a million Aadhaar numbers published on Jharkhand govt website due to a technical problem.
Digital identities of more than a million citizens have been exposed due to a coding error on a website maintained by the Jharkhand Directorate of Social Security.
“We got to know about it this week itself. Our programmers are working on it, and the matter should be addressed very soon,” said MS Bhatia, secretary of the state’s social welfare department.
The Jharkhand Directorate contains personal information of more than 1.6 million pensioners, the technical issue compromised citizen records containing names, addresses, Aadhaar numbers and bank account details of the beneficiaries of Jharkhand’s old age pension scheme.
“Their personal details are now freely available to anyone who logs onto the website, a major privacy breach at a time when the Supreme Court, cyber-security experts and opposition politicians have questioned a government policy to make Aadhaar mandatory to get benefits of a variety of government schemes and services.” reported the Hindustantimes.com.
The glitch exposed transaction-level data on pension paid to the citizens.

The Hindustantimes.com highlighted that the publishing of Aadhaar numbers is in contravention of Section 29 (4) of the Aadhaar Act.
Earlier this year, the Unique Identification Authority of India (UIDAI) blacklisted an Aadhaar service provider for 10 years due to a data leak that exposed the Aadhaar number of MS Dhoni, former captain of the Indian cricket team.
Incidents and abuses involving the Indian biometric ID system are not a rarity.
According to the Congress leader Jairam Ramesh the incident “makes a complete mockery of all that Jaitley and Ravi Shankar Prasad have said in Parliament.”
“Will the CEO of UIDAI take any action against the government of Jharkhand for making this dataset public? And if they don’t, does that mean they condone this act?” said Pranesh Prakash, policy director at the Centre for Internet and Society.
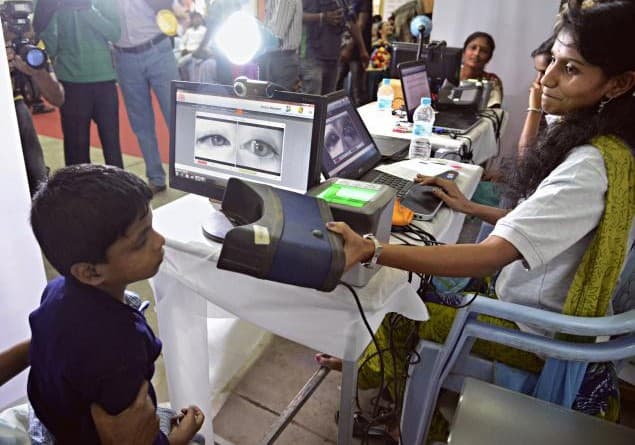
The Aadhaar is the world’s largest biometric ID system, with over 1.123 billion enrolled members as of 28 February 2017, it is mandatory to provide an Aadhaar number when filing income tax returns.
Unfortunately, according to Ramesh, the system caused several problems to people, in some cases citizens had been denied their legally mandated welfare entitlements.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – India, data leak)
[adrotate banner=”5″]
[adrotate banner=”13″]


