Microsoft researchers warn that threat actors are delivering the Godzilla framework using a static ASP.NET machine.
In December 2024, Microsoft Threat Intelligence researchers spotted a threat actor using a public ASP.NET machine key to deploy Godzilla malware, exploiting insecure key usage in code.
Microsoft has since found over 3,000 public keys that could be used to carry out ViewState code injection attacks. Unlike previously known ViewState code injection attacks that used compromised or stolen keys that are often sold on dark web forums, the recent findings show that publicly disclosed keys pose a higher risk because are used in development code.
ViewState allows ASP.NET Web Forms to preserve page and control state between postbacks. ViewState data is stored in a hidden field on the page and is Base64 encoded. The ASP.NET page framework uses machine keys to protect ViewState against tampering and information disclosure.
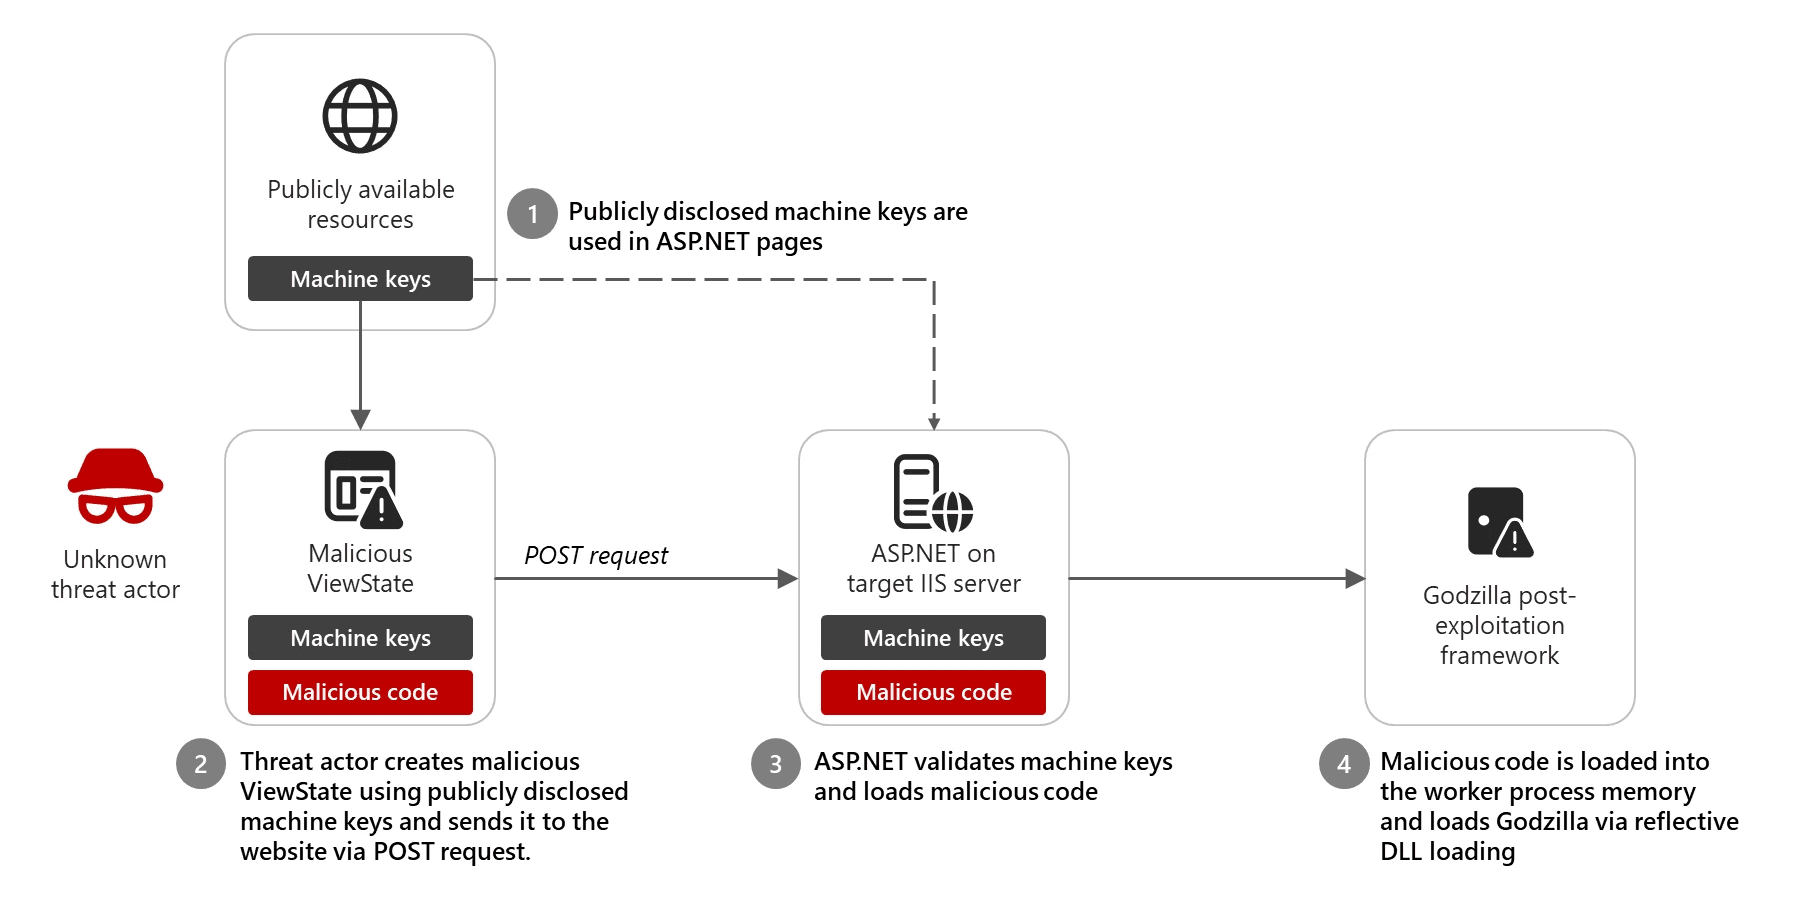
Stolen machine keys allow attackers to craft malicious ViewState data, enabling remote code execution on IIS servers when processed by ASP.NET Runtime.
“If these keys are stolen or made accessible to threat actors, these threat actors can craft a malicious ViewState using the stolen keys and send it to the website via a POST request. When the request is processed by ASP.NET Runtime on the targeted server, the ViewState is decrypted and validated successfully because the right keys are used.” reads the report published by Microsoft. “The malicious code is then loaded into the worker process memory and executed, providing the threat actor remote code execution capabilities on the target IIS web server.”

Microsoft recommends securely generating machine keys, avoiding default or public keys, encrypting secrets, upgrading to ASP.NET 4.8, and hardening servers.
The company provided steps to remove or replace ASP.NET keys and removed key samples from documentation to prevent insecure practices.
“If successful exploitation of publicly disclosed keys has occurred, rotating machine keys will not sufficiently address possible backdoors or persistence methods established by a threat actor or other post-exploitation activity, and additional investigation may be warranted.” concludes the report. “In particular, web-facing servers should be fully investigated and strongly considered for re-formatting and re-installation in an offline medium in cases where publicly disclosed keys have been identified, as these servers are most at risk of possible exploitation.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ASP.NET machine)