
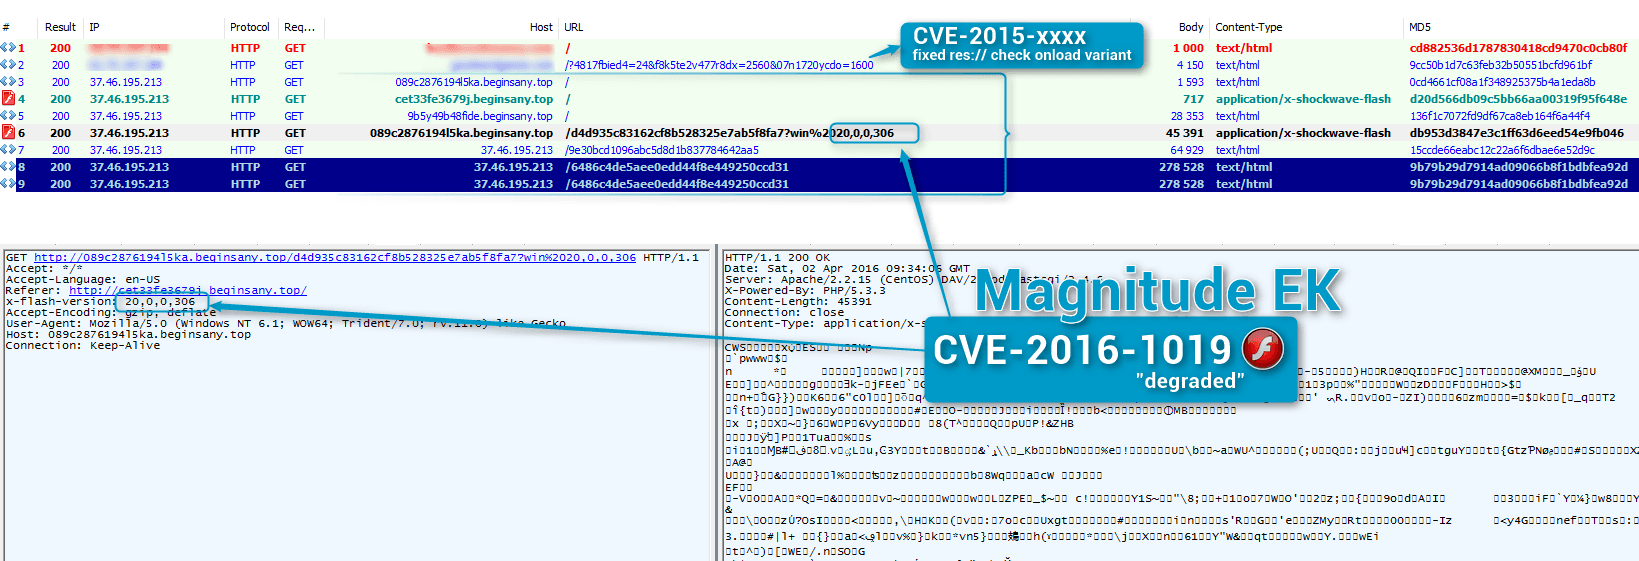
Cyber criminals are exploiting the Flash player zero-day vulnerability (CVE-2016-1019) affecting Flash Player 21.0.0.197 and earlier disclosed by Adobe.
Cyber criminals are already exploiting the Flash player zero-day vulnerability (CVE-2016-1019) affecting Flash Player 21.0.0.197 and earlier (CVE-2016-1019) disclosed by Adobe this week.
Researchers at security firm Proofpoint confirmed that cyber gangs are exploiting it to distribute a ransomware dubbed Cerber.
The hackers exploited the Flash Zero-day vulnerability to infect machines running Flash Player 20.0.0.306 and earlier on Windows 10 and earlier.
“A critical vulnerability (CVE-2016-1019) exists in Adobe Flash Player 21.0.0.197 and earlier versions for Windows, Macintosh, Linux, and Chrome OS. Successful exploitation could cause a crash and potentially allow an attacker to take control of the affected system.” reported the advisory published by Adobe a couple of days ago on the Flash Player zero-day vulnerability.
The Flash player zero-day vulnerability is a memory corruption bug that exists in an undocumented ASnative API, it can be exploited by attackers for remote code execution. The popular security expert Kafeine reported the inclusion of the zero-day flaw in the Magnitude exploit kit.
“On April 2, 2016, Proofpoint researchers discovered that the Magnitude exploit kit (EK) [1] was successfully exploiting Adobe Flash version 20.0.0.306. Because the Magnitude EK in question did not direct any exploits to Flash 21.0.0.182, we initially suspected that the exploit was for CVE-2016-1001 as in Angler [2], the combination exploit “CVE-2016-0998/CVE-2016-0984″ [3], or CVE-2016-1010.” reported ProofPoint.

“Despite the fact that this new exploit could potentially work on any version of Adobe Flash, including a fully patched instance of Flash, the threat actors implemented it in a manner that only targeted older versions of Flash. In other words, equipped with a weapon that could pierce even the latest armor, they only used it against old armor, and in doing so exposed to security researchers a previously unreported vulnerability,” states Proofpoint “We refer to this type of faulty implementation as a ‘degraded’ mode, and it is something that we have observed in the past with CVE-2014-8439 and CVE-2015-0310 in Angler.”
Adobe explained that a mitigation was had been in the version 21.0.0.182 released in March, anyway it has solved the issue with the release of Flash Player 21.0.0.213, which also fixes other 23 vulnerabilities.
It is interesting to note that experts at FireEye noted that the zero-day exploit code for the CVE-2016-1019 presents many similarities to exploits leaked as a result of the clamorous Hacking Team hack.
“The exploit’s code layout and some of the functionalities are similar to the leaked HackingTeam exploits, in that it downloads malware from another server and executes it.” states the analysis published by FireEye.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Flash Player zero-day vulnerability, CVE-2016-1019)
[adrotate banner=”5″]
[adrotate banner=”13″]


