
Physical security firm ADT disclosed a data breach, threat actors stole information from 30,000 customers and leaked it.
ADT is a provider of alarm and physical security systems, it employs more than 13,000 professionals in over 150 locations throughout the U.S.. The company, which has over 6 million customers, disclosed a data breach following a cyber attack.
Threat actors had access to certain databases containing ADT customer order information. The company locked out the threat actors and launched an investigation into the incident with the help of a leading third-party cybersecurity experts.
“ADT Inc. (“ADT” or the “Company”) recently experienced a cybersecurity incident during which unauthorized actors illegally accessed certain databases containing ADT customer order information.” reads a FORM 8-K filed with SEC. “After becoming aware of the incident, the Company promptly took steps to shut down the unauthorized access and launched an investigation, partnering with leading third-party cybersecurity industry experts. The attackers nonetheless obtained some limited customer information, including email addresses, phone numbers and postal addresses.”
ADT’s investigation suggests that customers’ home security systems were not compromised. The company has found no evidence that threat actors have stolen financial information like credit card or banking. The company believes that the incident impacted a small percentage of customers and notified them. ADT does not expect the security breach to significantly impact its operations or financial condition. The investigation is still ongoing.
“Based on its investigation to date, the Company has no reason to believe that customers’ home security systems were compromised during this incident. Additionally, the Company has no reason to believe the attackers obtained other personally sensitive information such as credit card data or banking information.” continues the FORM 8-K. “The Company is continuing its investigation into this cybersecurity incident and has notified the customers it believes to have been affected, who comprise a small percentage of the Company’s overall subscriber base.”
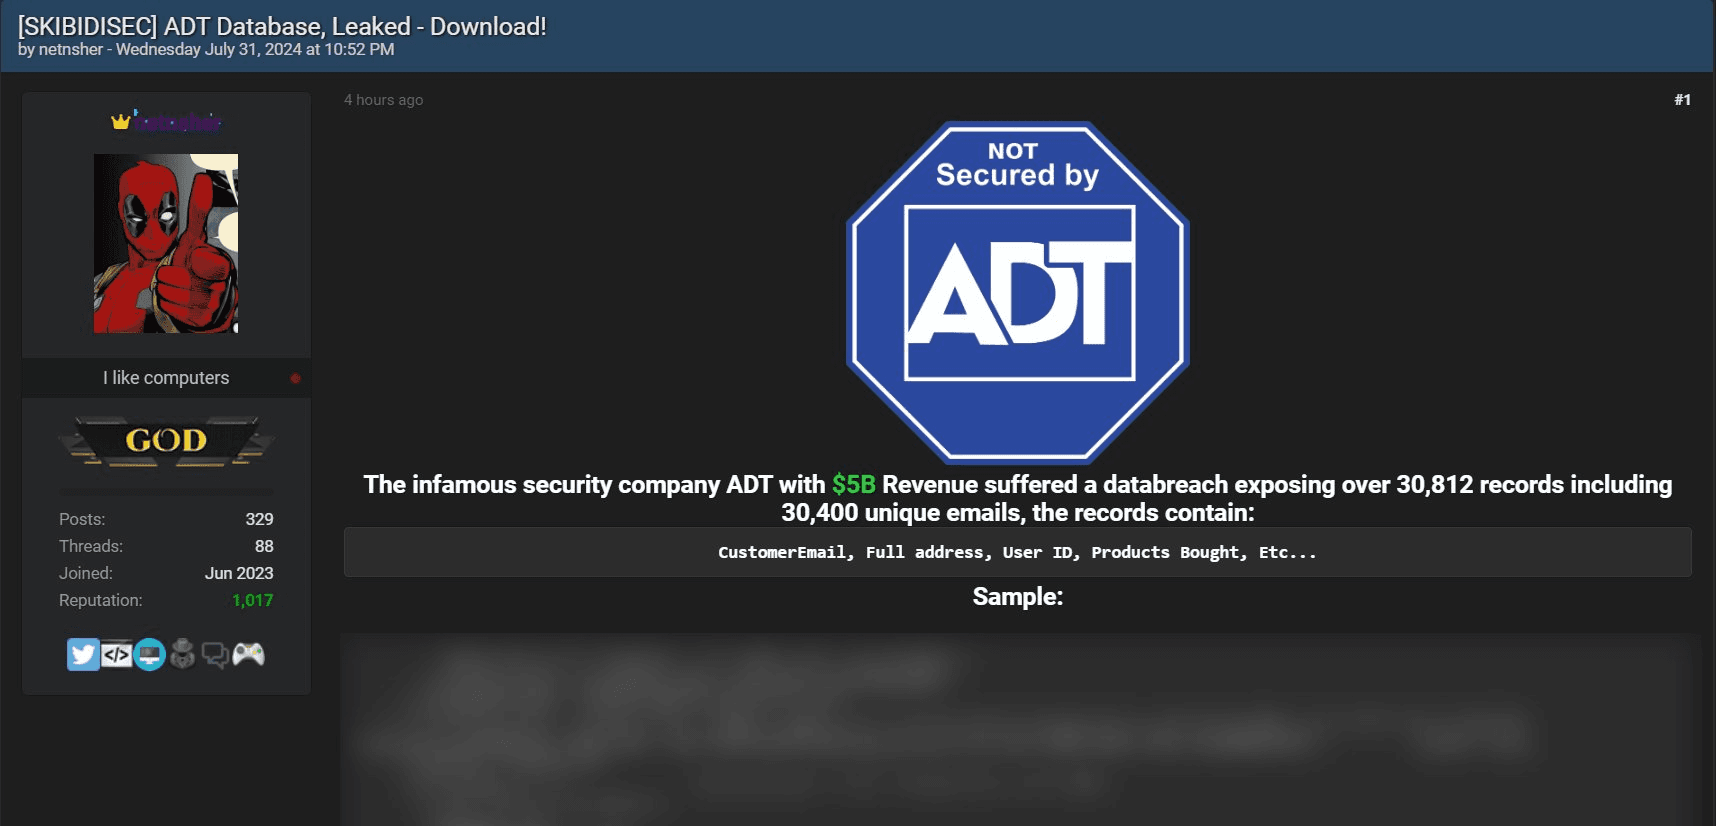
A threat actor that goes online with the moniker “netnsher” claimed the hack of ADT on a popular cybercrime forum.
The threat actor claimed that the data breach had exposed over 30,812 records, including 30,400 emails. The stolen data allegedly includes customer emails, full addresses, user IDs, products bought, and more.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, data breach)


