
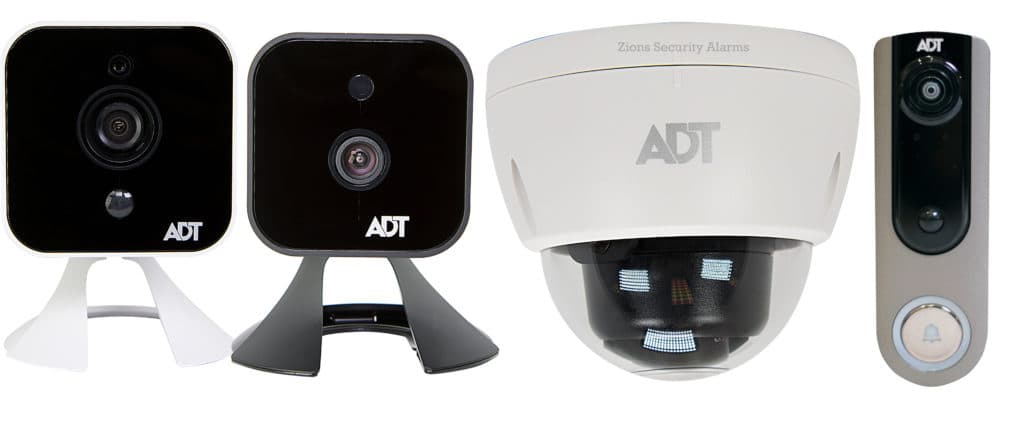
A former ADT employee pleads guilty for accessing the cameras he installed at the home of the company’s customers in the Dallas area.
Telesforo Aviles (35) is a former ADT employee that pleaded for accessing the cameras he installed at the home of the company’s customers.
Every time the man worked at the home of a customer in the Dallas area where an attractive woman was living, he added his personal email address to customers’ “ADT Pulse” accounts, to have real-time access to the video feeds from the cameras.
“This defendant, entrusted with safeguarding customers’ homes, instead intruded on their most intimate moments,” said Acting U.S. Attorney Prerak Shah. “We are glad to hold him accountable for this disgusting betrayal of trust.”

Aviles faces up to five years in federal prison for having illegally accessed roughly 200 accounts more than 9,600 times, in a period of more than four years.
Mr. Aviles admitted having regularly added his own email address to customers’ ADT Pulse accounts to watch women naked and couples engaged in sexual activity for his own sexual gratification, they said.
“The defendant used his position of employment to illegally breach the privacy of numerous people. The FBI works with our law enforcement partners to thoroughly investigate all cyber intrusions and hold criminals accountable for their actions,” said FBI Dallas Special Agent in Charge Matthew J. DeSarno.
ADT discovered Aviles’s activity on April 23 when a customer informed the company of the presence of an unauthorized email on their ADT account.
In April 2020, ADT terminated Aviles and reported him to law enforcement.
“Recently, a customer called to let us know there was an unauthorized email on their ADT account. The security and privacy of our customers is our top priority, and we immediately began an internal investigation.” reads a statement published by the company. “Unfortunately, our investigation revealed that during a service visit, one of our Dallas-area technicians had added his personal email address to this customer’s account to gain unauthorized access, and he had done the same thing during service visits with other customers in the Dallas area.”
The company contacted the impacted customers and apologized to them.
“We apologize to the customers affected by the actions of this former employee and deeply regret this incident,” ADT’s statement said. “The ADT mission is to help protect and connect people with the things they love most. Fully earning this trust back may take time, but nothing is more important to us and to those who have served our customers under the ADT banner for the last 145 years.”
If you want to receive the weekly Security Affairs Newsletter for free subscribe here.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, privacy)
[adrotate banner=”5″]
[adrotate banner=”13″]


