
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Talos Team discovered serious issues in Aerospike Database Server

Security experts from Cisco Talos discovered several flaws in the Aerospike Database Server, a high-performance, and open source NoSQL database. Security experts from Cisco Talos have discovered several vulnerabilities in the Aerospike Database Server, a high-performance, and open source NoSQL database. It is used by several major brands for high-performance applications, including Kayak, AppNexus, Adform, adMarketplace and […]

Talos Team discovered serious issues in Aerospike Database Server

Security experts from Cisco Talos discovered several flaws in the Aerospike Database Server, a high-performance, and open source NoSQL database.

Security experts from Cisco Talos have discovered several vulnerabilities in the Aerospike Database Server, a high-performance, and open source NoSQL database.

It is used by several major brands for high-performance applications, including Kayak, AppNexus, Adform, adMarketplace and BlueKai.

The Cisco Talos team discovered that Aerospace Database Server 3.10.0.3, and likely earlier versions, is affected by three flaws that have been rated as critical and high severity, including remote code execution and information disclosure issues.

Talos has published technical details of the vulnerabilities in the advisories that also include proof-of-concept (PoC) code for them.

“Talos is disclosing multiple vulnerabilities discovered in the Aerospike Database Server. These vulnerabilities range from memory disclosure to potential remote code execution. This software is used by various companies that require a high performance NoSQL database. Aerospike fixed these issues in  version 3.11.” reads the advisory published by the Talos Team.

TALOS-2016-0264 (CVE-2016-9050) – Aerospike Database Server Client Message Memory Disclosure Vulnerability
TALOS-2016-0266 (CVE-2016-9052) – Aerospike Database Server Index Name Code Execution Vulnerability
TALOS-2016-0268 (CVE-2016-9054) – Aerospike Database Server Set Name Code Execution Vulnerability.
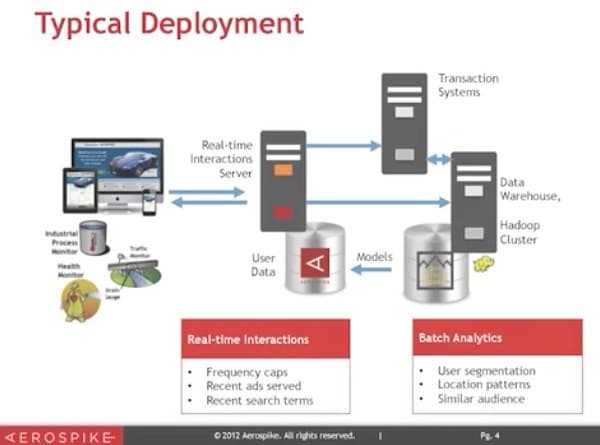
Aerospike Database Server

The first security vulnerability, tracked as CVE-2016-9050, is an out-of-bounds read issue that affects the client message-parsing functionality. An attacker can exploit it by sending a specially crafted packet to the listening port which can result in memory disclosure or a denial-of-service (DoS) condition.

A second vulnerability, tracked as CVE-2016-9052, is an arbitrary code execution that affects a different function, namely “as_sindex__simatch_by_iname.”

The third one tracked as CVE-2016-9054, is a stack-based buffer overflow that resides in the querying functionality, specifically the “as_sindex__simatch_list_set_binid” function. It is quite simple to exploit, an attacker has to connect to the listening port to remotely execute arbitrary code via a specially crafted packet that triggers the vulnerability.

The flaws were reported to the Aerospike development team on December 23 and they addresses them on January 5 in version 3.11.0.

Talos has published advisories containing technical details and proof-of-concept (PoC) code for each of the vulnerabilities.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Aerospike Database Server, hacking)


