
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Dark Web – Agora users targeted by a hacking campaign

Users of the popular Agora Dark Market have been targeted by unknown crooks who sent them malicious java script exploit that tries to steal their Bitcoin. Users of the popular Agora Marketplace have been targeted by unknown crooks who sent them malicious messages trough their PM system. The messages contain a malicious java script exploit that […]

Dark Web – Agora users targeted by a hacking campaign

Users of the popular Agora Dark Market have been targeted by unknown crooks who sent them malicious java script exploit that tries to steal their Bitcoin.

Users of the popular Agora Marketplace have been targeted by unknown crooks who sent them malicious messages trough their PM system. The messages contain a malicious java script exploit that was designed to drain the Bitcoins from the victim’s wallet.

“Immediately after I clicked to open the page, tons of Agora tabs opened up saying “Unable to withdraw amount: 1.0000000”, “Unable to withdraw amount: 2.0000000″, etc. and there were like at least 20 pages with different amounts. 2.0, 0.5, etc. Luckily I had only like $20 in my account.” reported one of the victims in a discussion started on Reddit.

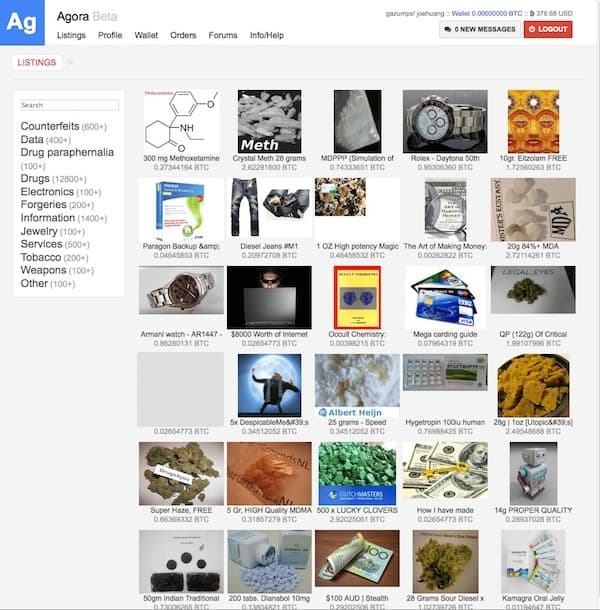
The following image was reported by the popular deepdotweb.com:

Agora marketplace

When Agora users click the link in the message, the malicious JS code tries to exploit a CSRF vulnerability in the Dark Market to steal users fund from Agora’s wallet as well as changing the users PGP key and reset his PIN code.

As reported by DeepDotWeb, the exploit could be successfully exploited if the following conditions are respected:

The user has to have an active session open with Agora

The user must have JS enabled

See an unknown link and be dumb enough to click on it

The complete code of the malicious exploit is available on Pastebin.

In order for the exploit to work:

  • The user has to have an active session open with Agora
  • [The user ] Must have JS enabled
  • Victims click on the malicious link

Agora users are advised, don’t click on any link in a message, the suggestion is particulrly important for Agora vendors.

Pierluigi Paganini

(Security Affairs –  Agora Dark market, cybercrime)


