
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Data from Airlink International UAE leaked on multiple dark web forums

Cybersecurity researchers from Cyble have spotted a threat actor sharing leaked data of Airlink International UAE for free on two different platforms. Cybersecurity researchers from Cyble have found a threat actor sharing leaked data of Airlink International UAE for free on two platforms on the dark web. The availability of the data on the dark web could pose organizations to serious risk, threat […]

Airlink International UAE

Cybersecurity researchers from Cyble have spotted a threat actor sharing leaked data of Airlink International UAE for free on two different platforms.

Cybersecurity researchers from Cyble have found a threat actor sharing leaked data of Airlink International UAE for free on two platforms on the dark web.

The availability of the data on the dark web could pose organizations to serious risk, threat actors could use this data to carry out multiple malicious attacks.

Cyble discovered the data leak as part of its daily monitoring.

Airlink International U.A.E. is a leading company for any travel and logistics requirements. It has more than than 200 employees with around $250 million in revenue.

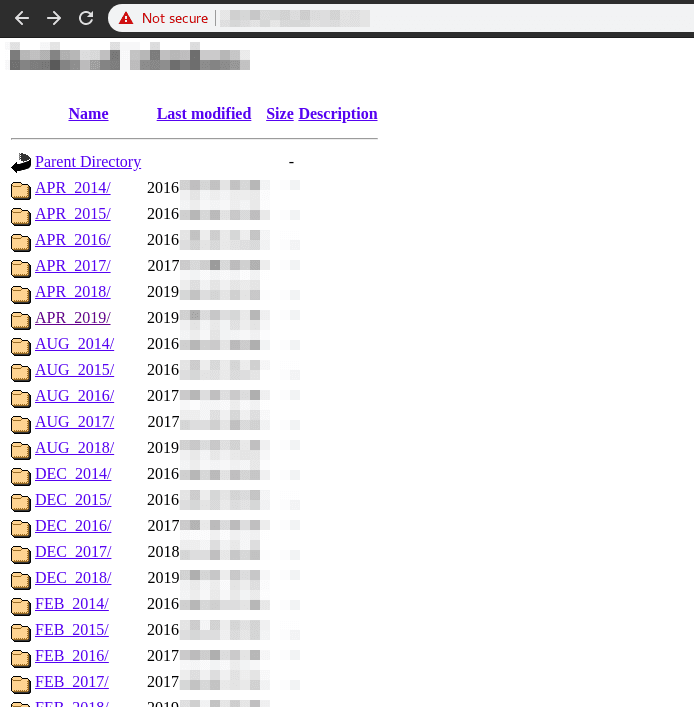
The data leak is the result of a misconfigured server containing 60 directories with approximately 5,000 files each.

The data leak was first reported on May 30, 2020, the data have been posted online by the collective KelvinSecTeam.

“The files present accommodation reservations, airline tickets and other logistics services that the company provides on a global scale. In a quick inspection by sampling, it was possible to observe customers of different nationalities and services provided in Africa, Asia and Europe.” reported the media.

According to Cyble, now, another threat actor is spreading the same data on multiple dark web forums in an attempt to gain fame.

Leaked data includes 14 folders and 53,555 files divided into the following categories:

  • Passport scans
  • Flight bookings
  • Hotel bookings
  • Email communications between Airlink International Group employees and customers
  • Insurance policy for international travel

Cyble provides recommends the following recommendation to the organizations:

  • Configure server to prevent unauthorized access, directory listing
  • Review old backup and unreferenced files for sensitive information
  • Test file permissions
  • Enumeration of infrastructure and application administrator interfaces
  • Consider running scans and doing audits periodically to help detect future misconfigurations or missing patches
[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Airlink International UAE)

[adrotate banner=”5″]

[adrotate banner=”13″]


