
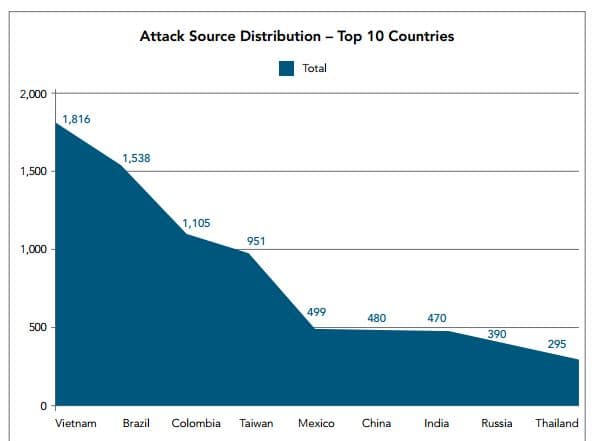
According to the US-based Akamai Technologies Distributed Denial Of Service (DDoS) attacks have a great level of sophistication today.
The Morris Worm of 1989 caused massive damage and losses with its unintentionally caused Denial Of Service (DoS) attacks. Fast forward to today, attacks have sharpened teeth targeting almost every IT service, from telco to gaming firms.
Distributed Denial Of Service attacks have a great level of sophistication today.
Consider for example the recent DDoS attack reported by the US-based Akamai Technologies against an European organization, a media that organization experienced a 363-GBps assault.
“On June 20, Akamai Technologies mitigated one the largest confirmed Distributed Denialof-Service (DDoS) attacks of the year on our routed network. The attack targeted a European media organization and was comprised of six attack vectors: syn, udp fragment, push, tcp, dns, and udp DDoS floods. It peaked at 363 Gigabits per second (Gbps) and 57 Million packets per second (Mpps).” Reads the Akamai Threat Advisory. “The attack analysis identified a dns reflection technique that abused a dnssec-configured domain. This attack technique generates an amplified response size due to the requirements of the Domain Name System Security Extension (dnssec).”
Everyone is so worried about Ransomware, Pokemon GO [which also faced Distributed Denial Of Service attacks recently] and Melania Trump’s copied speech. But we forgot that like many unwanted past memories , DDoS’ evolving nature will never make it a thing of the past but it shows a trend to a complex structure of massive future attacks.
Let’s break Distributed Denial Of Service attacks by its basic categories. HTTP flood,UDP flood,SYN flood,Ping Of Death (POD) , Slowloris,NTP Amplification , Zero Day DDoS attacks and the list goes on. The new kid on the block the DNS reflection, that adds to the huge torrent of data bombardment and is coming into use quite a bit.

The availability of a massive botnet in underground markets which maybe have large number of highjacked home routers . This lets malicious actors have DDoS service on lease to launch attacks.
“During the past few quarters, Akamai has observed and mitigated a large number of dns reflection and amplification DDoS attacks that abuse dnssec-configured domains. As with other dns reflection attacks, malicious actors continue to use open dns resolvers for their own purposes, effectively using these resolvers as a shared botnet. The attack techniques and duration of the attack point to the likelihood of booter services available for lease in the DDoS-for-hire underground marketplace.” Continues the advisory.
“From a technical perspective, the discovery and subsequent increasing employment of new attack vectors or botnets always represent significant, albeit grim milestones,” Akamai concluded.
DDoS campaigns are gaining a huge sophistication to them. I remember huge DDoS attacks being launched where refrigerators where involved. But with the coming of Smart Grid could the complexity , massiveness and surging nature of such attacks become a morphed threat that only a few could handle ? Today only businesses and organisational datacentres are targets of such attacks . Tomorrow could such attacks could have a dire affect on us also, I mean some Pokemon GO maniac surely was angry that he couldn’t do a gym battle during the recent DDoS attack.
About the Author: Joshua Bahirvani
 Cyber Security Enthusiast and believer of Privacy in this Digital Age.
LinkedIn : https://in.linkedin.com/in/jbahirvani15
Peerlyst: https://www.peerlyst.com/users/joshua-bahirvani
Twitter : @B15joshua
Medium : @jbahirvani15


