
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

ALPHV/BlackCat and Clop gangs claim to have hacked cosmetics giant Estée Lauder

The American cosmetics giant company Estée Lauder was hacked by two distinct ransomware groups, the ALPHV/BlackCat and Clop gangs. Yesterday the cybersecurity expert @sonoclaudio first alerted me about a strange circumstance, two ransomware actors, ALPHV/BlackCat and Clop, claim to have hacked the cosmetics giant company Estée Lauder and added the company to their Tor leak […]

Estée Lauder

The American cosmetics giant company Estée Lauder was hacked by two distinct ransomware groups, the ALPHV/BlackCat and Clop gangs.

Yesterday the cybersecurity expert @sonoclaudio first alerted me about a strange circumstance, two ransomware actors, ALPHV/BlackCat and Clop, claim to have hacked the cosmetics giant company Estée Lauder and added the company to their Tor leak sites.

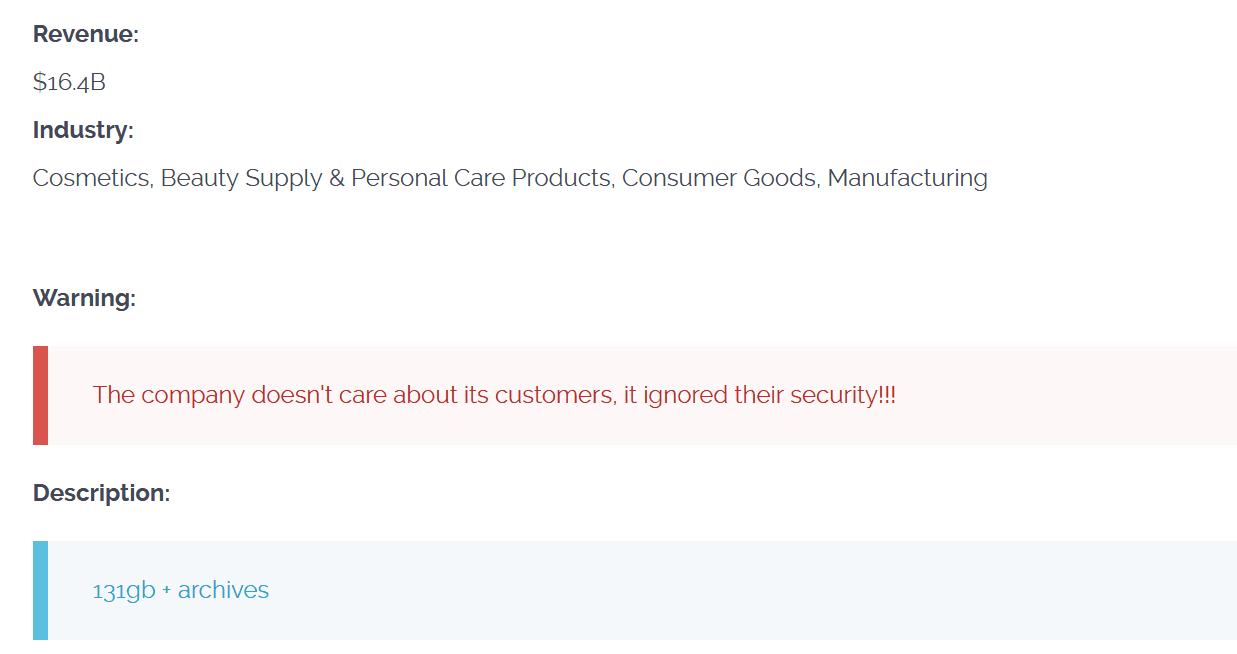
The two attacks appear to be distinct, the Clop group claims to have stolen 131GB of data from the company. Clop gang also published the following statement on its leak site:

“The company doesn’t care about its customers, it ignored their security!!”

The BlackCat group also highlighted the poor security of Estée Lauder and said that they have still access to the victim’s network.

The Estée Lauder Companies yesterday disclosed one of the attacks in Security Exchange Commission (SEC) filing. The company admitted that crooks had access to its infrastructure and exfitrated some data.

Estée Lauder declared that it has quickly responded to the incident and took down some systems to prevent the threat from spreading within its network. The company is still investigation with the help of law enforcement to determine the extent of the security incident.

“The Estée Lauder Companies Inc. (NYSE: EL) has identified a cybersecurity incident, which involves an unauthorized third party that has gained access to some of the Company’s systems.  After becoming aware of the incident, the Company proactively took down some of its systems and promptly began an investigation with the assistance of leading third-party cybersecurity experts.  The Company is also coordinating with law enforcement.  Based on the current status of the investigation, the Company believes the unauthorized party obtained some data from its systems, and the Company is working to understand the nature and scope of that data.” reads the FORM 8-K report filed by the company.

Estée Lauder announced that it is implementing measures to secure its business operations and prevent similar incidents in the future. The incident admitted that the security breach has caused, and is expected to continue to cause, disruption to parts of the company’s business operations.

Even if the company did not share details about the attack, it is likely that the Clop ransomware group has breached its network by exploiting the MoVEit Transfer zero-day vulnerability

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


