
Researchers disclosed two new attack techniques that allow modifying visible content on certified PDF documents without invalidating the digital signature.
Researchers from Ruhr-University Bochum have disclosed two new attack techniques, dubbed Evil Annotation and Sneaky Signature attacks, on certified PDF documents that could potentially allow attackers to modify visible content without invalidating their digital signature. The attacks are documented in CVE-2020-35931, CVE-2021-28545, and CVE-2021-28546.
The experts presented the results of the study at the 42nd IEEE Symposium on Security and Privacy (IEEE S&P 2021).
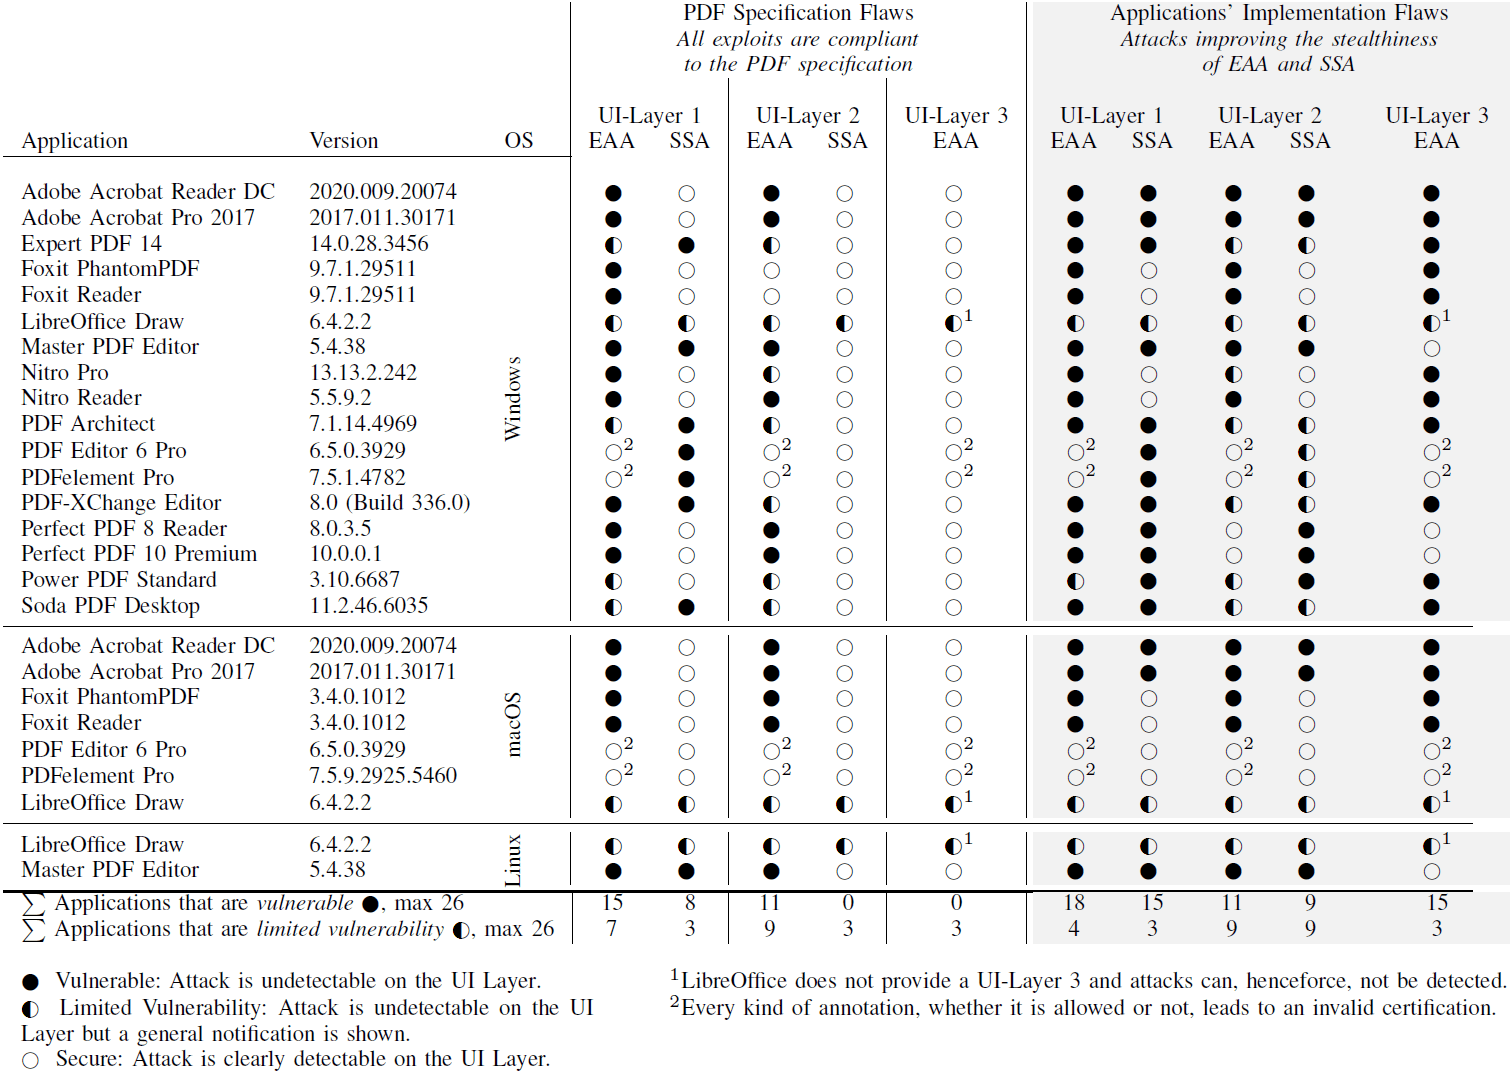
The attacks leverage the flexibility of PDF certification that allows signing or adding annotations to certified documents under different permission levels. The experts demonstrated that the EAA technique could be effective against 15 of 26 viewer applications while the SSA could work against 8 viewers.
“The attack idea exploits the flexibility of PDF certification, which allows signing or adding annotations to certified documents under different permission levels. Our practical evaluation shows that an attacker could change the visible content in 15 of 26 viewer applications by using EAA and in 8 applications using SSA by using PDF specification compliant exploits.” reads the post published by the researchers.
The experts explained that the certification of signed content also allows users with specific permissions set by the certifier to apply certain modifications to the PDF document. This means that the user could write text to specific form fields, provide annotations, or add its own signature if permitted by the certifier.
The idea behind Evil Annotation Attack (EAA) is to modify a certified document by inserting annotations that include malicious code.
“The idea of the Evil Annotation Attack (EAA) is to show arbitrary content in a certified document by abusing annotations for this purpose. Since P3 certified document allow to add annotations, EAA breaks the integrity of the certification.” continues the post.
The idea behind the Sneaky Signature Attack (SSA) is to manipulate the appearance of arbitrary content within the PDF by adding overlaying signature elements to a PDF document that is certified at level P2, which means that it allows to fill forms.

The experts demonstrated that attackers can modify the content of the document to display an International Bank Account Number (IBAN) that is associated with a bank account under their control and trick the victims to transfer the funds to this recipient.
“By inserting a signature field, the signer can define the exact position of the field, and additionally its appearance and content. This flexibility is necessary since each new signature could contain the signer’s information. The information can be a graphic, a text, or a combination of both. Nevertheless, the attacker can misuse the flexibility to stealthy manipulate the document and insert new content.” continues the post. “he attacker modifies a certified document by including a signature field with the malicious content at a position of attacker’s choice. The attacker then needs to sign the document, but he does not need to possess a trusted key. A self-signed certificate for SSA is sufficient. The only restriction is that the attacker needs to sign the document to insert the malicious signature field.”
The experts evaluated 26 PDF applications on each of the three UI-Layers against EAA and SSA attacks, below the results.

Adobe has addressed the CVE-2020-24432 vulnerability in November as part of its Patch Tuesday.
In February 2019, the experts from Ruhr-University Bochum found several flaws in popular PDF viewers and online validation services that allow to deceive the digital signature validation process.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, PDF)
[adrotate banner=”5″]
[adrotate banner=”13″]


