
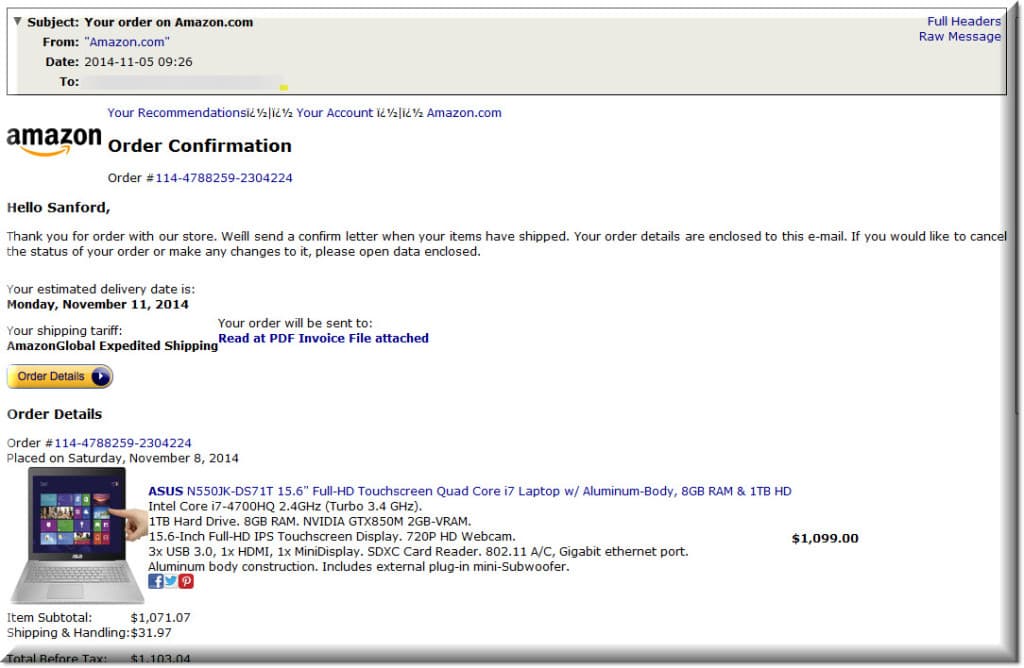
Security experts at AppRiver firm uncovered Malicious Amazon phishing emails that aim to infect Holiday Shoppers in the U.S. and U.K.
Researchers at AppRiver firm reported that cyber criminals are targeting holiday shoppers at Amazon UK with large a scale phishing campaign, which is spreading malicious emails.
The emails sent by crooks include malicious Microsoft Word documents in the attachment, their content as usual tries to trick the recipient in to open it. In the specific case the attackers try to convince the victims by purporting to contain information about the shipment of an order and adding in the subject line the number for the alleged shipment.

Experts at AppRiver detected the malicious campaign at the end of October and since then, they company has quarantined more than 600,000 phishing emails.
“These messages began hitting our filters on 10/31/14 and have been coming in consistently ever since. Thus far we have quarantined just over 600,000 of these messages. Each message contains a Word document (MD5: a75e196e6c0cabc145f4cdc3177e66ec) that contains a malicious macro. In most instances users should at a slightly lower risk with this infection vector, since macros are not enabled by default in more recent versions of Word.”
The attack scheme leverage on malicious emails including a Word document embedded with a macro that installs a Trojan dropper on the victim’s computer.
The malware also implements keylogging capabilities to harvest login credentials for online banking, web-based email services and social media profiles.
Experts consider low-risk the use of Office macros as malware vector, since macros are not enabled by default in recent versions of Office Application, including Microsoft Word.
Anyway if the user turns on support for macros, the commands can be executed compromising the recipient of the malicious email.
Security experts also revealed that also users of Amazon US are under attack, AppRiver quarantined nearly 160,000 malicious emails. The malicious campaign that is targeting Amazon US users uses a different method of infection and also the subject line of the messages is different.
“Instead of a malicious attachment, these messages utilize links to compromised wordpress sites. Clicking these links will launch the download of a .scr file named: invoice1104.pdf[dot]scr,” says AppRiver in the blog post; “
The shopping season is notoriously the period of the year when the cyber criminal activity is more intense, it is necessary to spread awareness of the principal cyber threats and providing the information on best practice to avoid problems.
Security Affairs – (Amazon phishing campaigns, cybercrime)


