
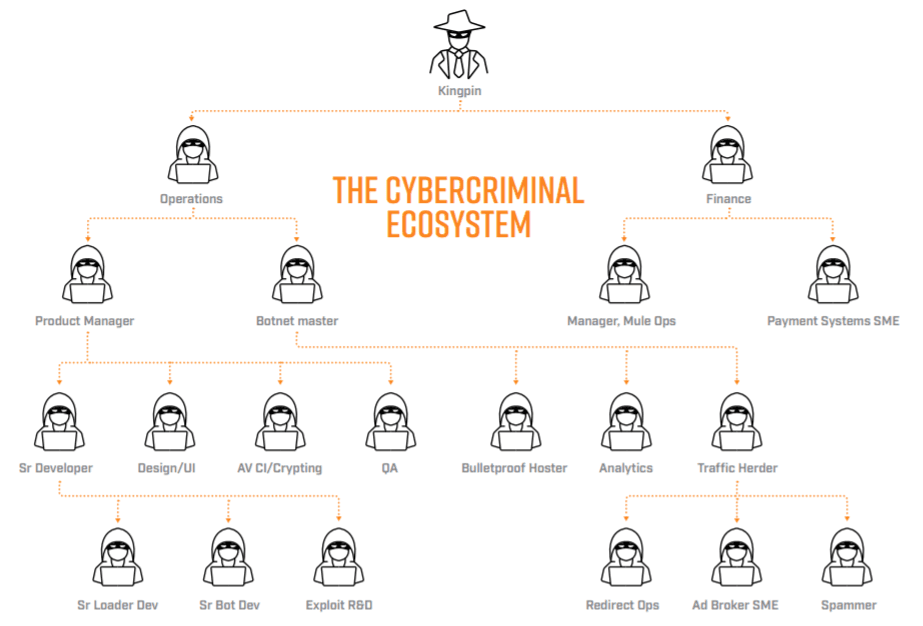
Security firm Flashpoint published an interesting paper titled, ‘Cybercrime Economy: An Analysis of Cybercriminal Communication Strategies‘ about cybercriminal communications of threat actors.
A recent research by the threat intelligence firm Flashpoint has uncovered how malicious threat actors communicate to share information between them.
The research has found out that there is a growing economy in the cybercriminals communications, more than just information sharing it has formed an ecosystem in which the failures, successes, planning and procedures to beat the organization’s countermeasures are shared as well as the planning of attacks.
The research points out that Cybercriminal Communications use a variety of software alongside with the access to communities in the deep and dark web. This is done in order to carry out cross domain organization for commit crimes like phishing, credit card fraud, spam, and every sort of attack that pass through the corporations’ filters and defenses.

The reason for the use of this software to communicate is too difficult law enforcement agencies from tracking the activities in the community’s forums as well as to give privacy to the user since most of these programs have cryptographic functions or protocols operating in its core. The software also allows a user to enter random, aleatory or even fraudulent information about the user which difficulty, even more, the process of detection.
On the other hand, one other reason for doing so is the payment required to maintain a forum, which in many cases can represent a difficult for cybercriminals. The use of communications programs is free of charge and anyone can download them.
The study was carried out by monitoring underground communities where the users often invited other members to discuss the planning outside the underground forum. It was analyzed 80 instant messengers applications and protocols, of which at least five were more used.
Privacy is implemented in these applications, like PGP an algorithm of encryption. The secure communication of user’s difficulty authorities to gain access to the content shared between the users. Without knowing the encryption key that has generated the codification for the session.
The most used programs by cybercriminals are ICQ, Skype, Jaber, Quiet Internet Pager, Pretty Good Privacy, Pidgin, PSI and AOL Instant Messenger (AIM).
The report shows that the use of Cybercriminal Communications is different among communities of different languages, below are reported “Language Group Specific Findings” for Russians we have the following situation:
1. Jabber (28.3%) 2. Skype (24.26) 3. ICQ (18.74%) 4. Telegram (16.39%) 5. WhatsApp (3.93%) 6. PGP (3.79%) 7. Viber (3.01%) 8. Signal (1.58%)
while for the Chinese we have the following distribution in 2016: 1. QQ (63.33%) 2. WeChat (35.58%) 3. Skype (0.44%) 4. WhatsApp (0.22%) 5. Jabber (0.31%) 6. PGP (0.13%) 7. ICQ (0.1%) 8. AOL Instant Messenger (0.08%)
“Cybercriminals can choose from a wide variety of platforms to conduct their peer-to-peer (P2P) communications.” states the report. “This choice is typically influenced by a combination of factors, which can include:
- Ease of use
- Country and/or Language
- Security and/or anonymity concerns
Sources:
http://www.securityweek.com/many-cybercriminals-prefer-skype-communications-study
http://www.ibtimes.co.uk/skype-whatsapp-how-cybercriminals-share-hacking-tips-tricks-online-1617822
http://www.infoworld.com/article/3190563/encryption/cybercriminals-prefer-to-chat-over-skype.html
https://www.flashpoint-intel.com/blog/cybercrime/cybercriminal-communication-strategies/
About the author Luis Nakamoto
Luis Nakamoto is a Computer Science student of Cryptology and an enthusiastic of information security having participated in groups like Comissão Especial de Direito Digital e-Compliance (OAB/SP) and CCBS (Consciência Cibernética Brasil) as a researcher in new technologies related to ethical hacking, forensics, and reverse engineering. Also, a prolific and compulsive writer participating as a Redactor to Portal Tic from Sebrae Nacional.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Skype, Cybercriminal Communications)
[adrotate banner=”5″]
[adrotate banner=”13″]


