
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Android droppers evolved into versatile tools to spread malware

Android droppers now spread banking trojans, SMS stealers, and spyware, disguised as government or banking apps in India and Asia. ThreatFabric researchers warn of a shift in Android malware: dropper apps now deliver not just banking trojans, but also SMS stealers and spyware, mainly in Asia. Google’s Pilot Program enhances Play Protect by scanning Android […]

Android droppers

Android droppers now spread banking trojans, SMS stealers, and spyware, disguised as government or banking apps in India and Asia.

ThreatFabric researchers warn of a shift in Android malware: dropper apps now deliver not just banking trojans, but also SMS stealers and spyware, mainly in Asia.

Google’s Pilot Program enhances Play Protect by scanning Android apps before installation in high-risk regions like India and Brazil, blocking apps with risky permissions or suspicious APIs. Modern droppers exploit this system by appearing harmless at install, then fetching the real payload after user interaction, bypassing initial security checks. This allows even simpler malware to evade detection, showing a timing gap in the Pilot Program that threat actors actively exploit.

“actors want to future-proof their operations. By encapsulating even basic payloads inside a dropper, they gain a protective shell that can evade today’s checks while staying flexible enough to swap payloads and pivot campaigns tomorrow.” reads the report published by ThreatFabric.

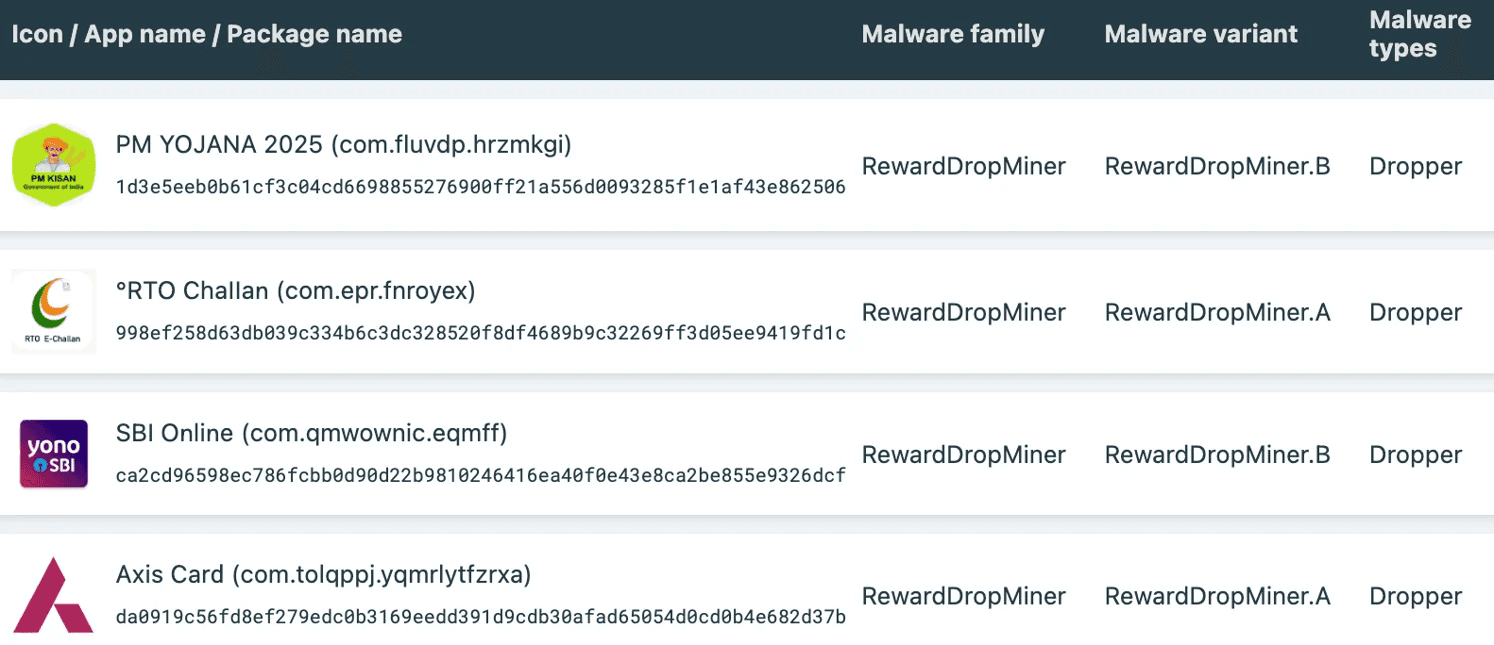
The experts discovered a dropped, called RewardDropMiner, which is a staged dropper that evades Play Protect and the Pilot Program, delivering spyware or payloads and previously running a hidden Monero miner, now removed in recent variants to reduce detection.

Android droppers

Droppers like SecuriDropper, Zombinder, BrokewellDropper, HiddenCatDropper, and TiramisuDropper evade Play Protect and Pilot Program by delaying permissions or hiding payloads, ensuring malware reaches victims despite Android defenses.

Droppers have evolved into versatile tools, quickly adapted by cybercriminals to bypass defenses like the Pilot Program, delivering both major and minor malicious apps.

“The takeaway is simple: Play Protect and the Pilot Program work, but only as part of a constantly evolving defence strategy. Detection needs to adapt as quickly as the threats themselves.” concludes the report. “In this cat-and-mouse game, droppers aren’t slowing down as they’re just getting smarter.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Android droppers)


