
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Over 3,000 Android Malware spotted using unsupported/unknown compression methods to avoid detection

Threat actors are using Android Package (APK) files with unsupported compression methods to prevent malware analysis. On June 28th, researchers from Zimperium zLab researchers observed that Joe Sandbox announced the availability of an Android APK that could not be analyzed from most of the anti-decompilation tools. The APT could be installed on Android devices running […]

Android APK

Threat actors are using Android Package (APK) files with unsupported compression methods to prevent malware analysis.

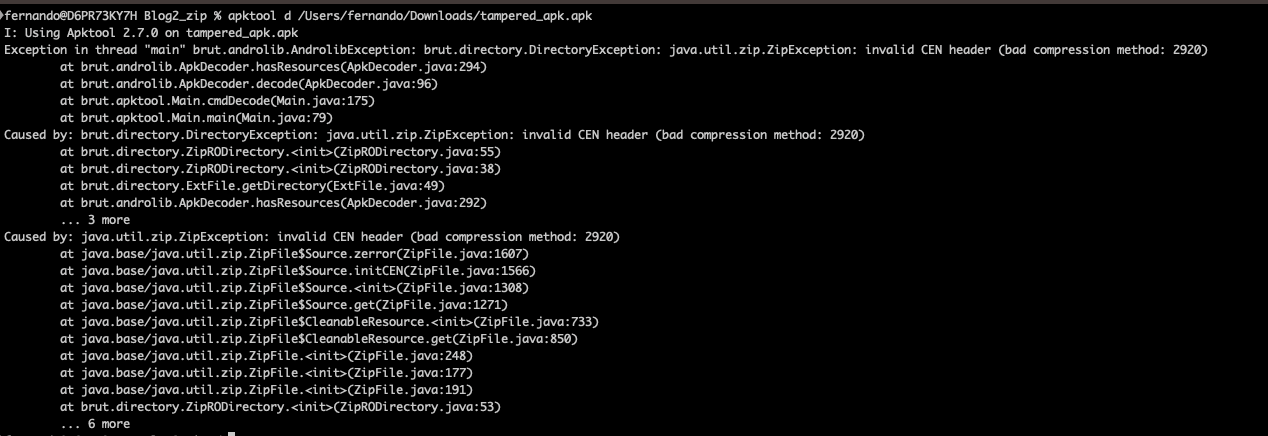
On June 28th, researchers from Zimperium zLab researchers observed that Joe Sandbox announced the availability of an Android APK that could not be analyzed from most of the anti-decompilation tools.

The APT could be installed on Android devices running versions above Android 9 Pie (API 28).

The technique is not new, in 2014 researchers demostrated how the compression algorithm (method) used in an APK could be tampered to remove automatic script analysis and hinder static analysis. 

“However, Android’s APK, which uses the ZIP format, supports only two compression methods. One is without any compression, i.e. the STORED method (0x0000), and the other is the DEFLATE (0x0008) compression algorithm.” reads the report published by Zimperium.”Depending on the Android version, the default behavior for unknown or unsupported methods differs:

  • In Android 4.3 and below, Java ZIP-handling code checks against the method being DEFLATE, and assumes that the STORED method has been used if it does not match.
  • In versions greater than Android 4.3, Android ZIP-handling assumes the compression method to be DEFLATE if the method specified does not match with STORED.

In Android versions below 9, applications using unsupported/unknown compression methods are not installable, but they work properly on versions above it.”

Zimperium experts found 3,300 artifacts using these compression algorithms, they run a retrohunt on public application repositories.

Most of these samples found by the researchers are corrupted beyond the point that the OS is able to load them, however 71 malicious samples can be properly loaded by the Android OS.

The experts have found no evidence that the apps were available on the Google Play Store a circumstance that suggests they were distributed through third-party stores or attackers used social engineering to trick the victims into installing them.

The researchers also identified additional corruptions to the APK files to avoid analysis tools, such as using filenames with more than 256 bytes, malformed AndroidManifest.xml file, and Malformed String Pool.

The report also includes Indicators of Compromise (IoCs).

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, malware)


