
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Applebee restaurants suffered payment card breach

RMH Franchise Holdings revealed on Friday afternoon that PoS systems at the Applebee ’s restaurants were infected with a PoS malware. Another week another data breach, RMH Franchise Holdings revealed last week that PoS systems at the Applebee’s restaurants were infected with malware. The PoS malware was used to collect names, payment card numbers, expiration dates, and […]

Applebee restaurants suffered payment card breach

RMH Franchise Holdings revealed on Friday afternoon that PoS systems at the Applebee ’s restaurants were infected with a PoS malware.

Another week another data breach, RMH Franchise Holdings revealed last week that PoS systems at the Applebee’s restaurants were infected with malware.

The PoS malware was used to collect names, payment card numbers, expiration dates, and card verification codes.

On Friday afternoon, RMH Franchise Holdings published a link to the data breach notice on its website.

“RMH Franchise Holdings (“RMH”) recently learned about a data incident affecting certain payment cards used at RMH-owned Applebee’s restaurants that we operate as a franchisee.” states the notice of the data breach.

“We are providing this notice to our guests as a precaution to inform them of the incident and to call their attention to some steps they can take to help protect themselves. RMH operates its point-of-sale systems isolated from the broader Applebee’s network, and this notice applies only to RMH-owned Applebee’s restaurants.”

The security breach was discovered on February 13, the RMH promptly started an investigation with the help of and law enforcement.

The infection lasted between December 6, 2017, and January 2, 2018, is some cases the malware was present on the PoS systems of restaurants since November 23 or December 5, 2017.

Almost any restaurant operated by RMH was impacted, the incident affects more than 160 restaurants in Alabama, Arizona, Florida, Illinois, Indiana, Kansas, Kentucky, Missouri, Mississippi, Nebraska, Ohio, Pennsylvania, Texas, and Wyoming.

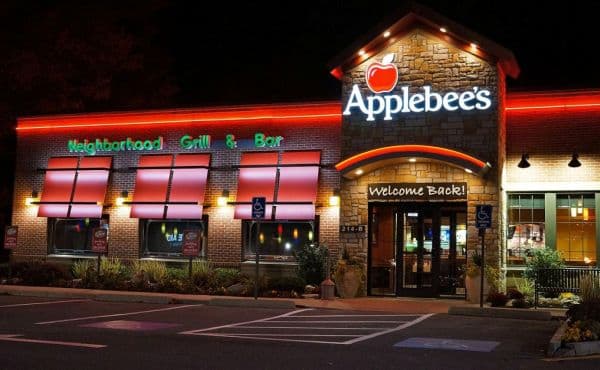
Applebees restaurants

The security breach does not affect online payments systems, clients using self-pay tabletop devices were not affected too.

RMH clarified that its payment systems are not affected by the incident because they are isolated from the payment network used Applebee.

“After discovering the incident on February 13, 2018, RMH promptly took steps to ensure that it had been contained. In addition to engaging third-party cyber security experts to assist with our investigation, RMH also notified law enforcement about the incident and will continue to cooperate in their investigation.”RMH added.

“Moving forward, RMH is continuing to closely monitor its systems and review its security measures to help prevent something like this from happening again.”

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Applebees restaurants, Payment card breach)

[adrotate banner=”5″]

[adrotate banner=”13″]


