
Nearly 37 million users of Ashley Madison have been impacted, the popular investigator Brian Krebs has collected clues on the alleged culprit.
The popular investigator Brian Krebs sustains to know the culprit of the Ashley Madison hack, which publicly leaked 37 million accounts belonging to the users of the adultery website.
Brian Krebs disclosed the Twitter account, Deuszu, used by an individual close to the responsible for the Ashley Madison data breach.
Avid Life Media, the company that owns the Ashley Madison is offering a $500,000 reward for information that could allow law enforcement to identify and arrest the hackers behind the recent data breach it suffered.
Krebs downloaded all the tweets sent in five years from Deuszu (Thadeus Zu):
These are the clues analyzed by Krebs in his analysis:
- Krebs was the first to know the data breach, a member of the Impact Team reported the hack to Krebs and confidentially gave him a link to a copy of the dump of the databases, at same time Deuszu tweeted the very same link. Who passed the same URL to Deuszu?
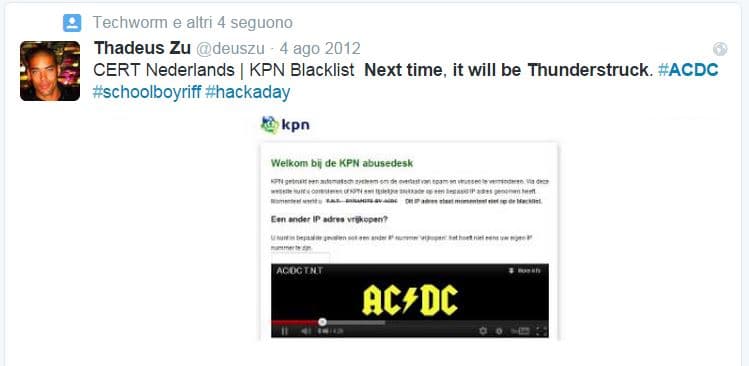
- Ashley Madison workers first discovered the hack on July 12 when they logged into their computers and received a message from the hackers. Evans only added that the message was accompanied by the AC/DC’s song “Thunderstruck.” By analyzing the Deuszu’s tweets, it appears the he is a fan of the popular rock band, going as far as telling one organization he or she hacked in 2012: “Next time, it will be Thunderstruck. #ACDC”

- Deuszu had Thunderstruck playing in a browser tab (see the picture) when he or she posted on Twitter a screenshot configuring “replication servers” to “get the show started. This tweet was sent 2 hours before Impact Team first contacted Krebs.

“The day before, he’d compromised the Web site for the Australian Parliament, taunting lawmakers there with the tweet: “Parliament of Australia bit.ly/NPQdsP Oi! Oi! Oi!….T.N.T. Dynamite! Listen to ACDC here.” he tweeted.
- A day before media agencies published the news that the Impact Team had dumped the full databases on file-sharing networks, Deuszu tweeted a copy of the team’s “time’s up” statement that announced the leak.
Krebs seems to have no doubts, Deuszu is directly involved in the Ashley Madison, even if it is an investigator who is following the case he certainly knows the identity of the culprit.
“[Deuszu] — whoever and wherever he is in real life — may not have been directly involved in the Ashley Madison hack; he claims in several tweets that he was not part of the hack, but then in countless tweets he uses the royal ‘We’ when discussing the actions and motivations of the Impact Team,” wrote Krebs.
“It is possible that Zu is instead a white hat security researcher or confidential informant who has infiltrated the Impact Team and is merely riding on their coattails or acting as their mouthpiece. But one thing is clear: If Zu wasn’t involved in the hack, he almost certainly knows who was.”
(Security Affairs – Ashley Madison, Data Breach)


