
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Cyber Crime

Top website Askmen hacked and used to serve a banking trojan

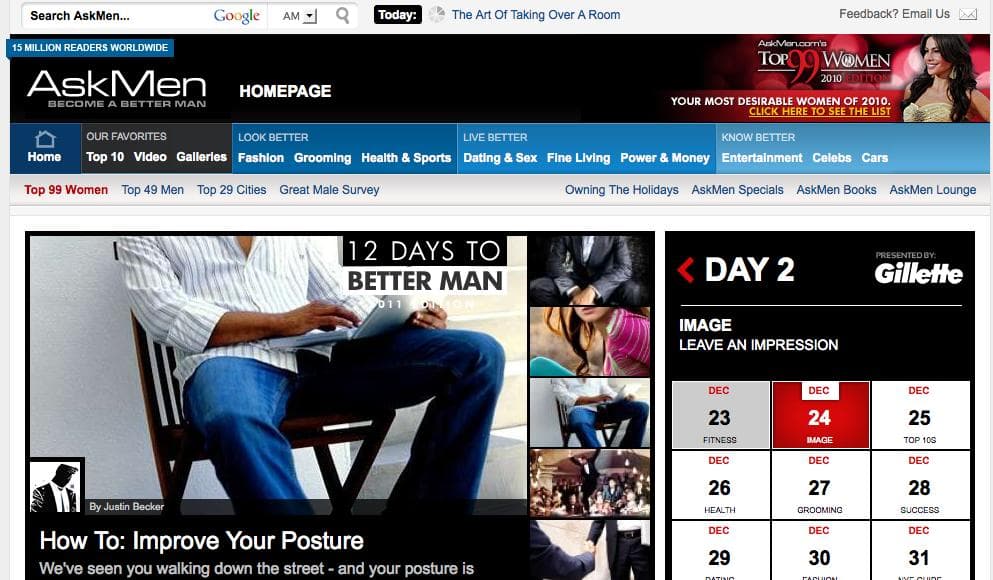
Askmen.com, one of the most popular websites on the Internet (Top 1000 Alexa), is compromised to sever the banking trojan Caphaw. Security experts at Websense have discovered that cyber criminals have compromised the popular website AskMen.com and they used it to serve malware. The attackers deployed several exploits to compromise the visitors, and if successful, the victim […]

Top website Askmen hacked and used to serve a banking trojan

Askmen.com, one of the most popular websites on the Internet (Top 1000 Alexa), is compromised to sever the banking trojan Caphaw.

Security experts at Websense have discovered that cyber criminals have compromised the popular website AskMen.com and they used it to serve malware.

The attackers deployed several exploits to compromise the visitors, and if successful, the victim is infected with the Caphaw Trojan. Caphaw is banking trojan used to steal banking credentials from victims, it also allows the attackers to drop additional malicious payload on the victim’s system.

The malicious code installed on AskMen.com will attempt to exploit Java (most likely CVE-2013-2465) and Adobe Reader, experts believe that hackers used the Nuclear exploit kit for the attack.

“The exploit page displays similar obfuscation techniques, which are often used in the Nuclear Pack exploit kit. In addition, the above mentioned Java exploit is most often used by Nuclear Pack. These facts strongly indicate that the attacker is using either the Nuclear Pack exploit kit or a variant of it.” reported experts at Websense in a blog post.

In February YouTube users were targeted by a classic drive-by download attack by exploiting client Java software vulnerabilities and also serving Caphaw Banking Trojan.

Websense discovered the compromise early last week and has informed the portal administrators, but they haven’t recognized the discovery of the experts for this reason it is suggested to avoid visiting the website until the security issue isn’t resolved.

“The injected code has been found in multiple locations within the main website as well as in localized versions of it,” “When a user browses to the main website, the injected code loads automatically and silently redirects the user to a website serving the actual exploit code. The injected code is obfuscated and can be found at the bottom of legitimate JavaScript pages on AskMen’s website.” added Websense.

AskMen.com is a popular portal dedicated to men and ranked by Alexa within the top 1000 websites. The AskMencom portal is visited on monthly base by nearly 11.6 million users for this reason it represents a privileged target for attackers.

askmen rank

It is crucial that administrators will fix soon the security issue due to the high number of visitors that each day visits the website, in a few days tens thousands or hundreds thousands of people could be infected if their systems are not properly patched.

The lesson learnt is that no one is secure!

Pierluigi Paganini

(Security Affairs –  Askmen.com, malware)


