
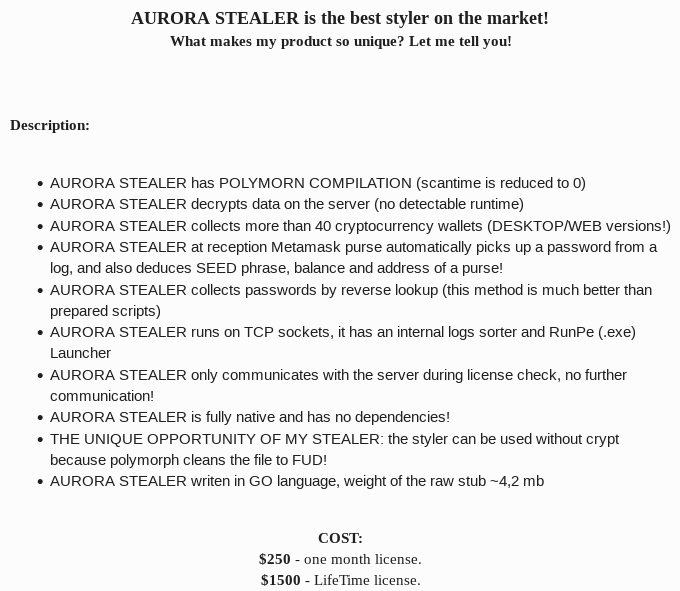
Researchers warn of threat actors employing a new Go-based malware dubbed Aurora Stealer in attacks in the wild.
Aurora Stealer is an info-stealing malware that was first advertised on Russian-speaking underground forums in April 2022. Aurora was offered as Malware-as-a-Service (MaaS) by a threat actor known as Cheshire. It is a multi-purpose botnet with data stealing and remote access capabilities.

Researchers at SEKOIA identified 7 traffers teams on Dark Web forums that announced the availability of the Aurora Stealer in their arsenal, a circumstance that confirms the increased popularity of the malware among threat actors.
| Traffers Team | Malware arsenal | Launch date | Last observed activity |
| RavenLogs | Aurora, Redline | 17/10/2022 | 14/11/2022 |
| BrazzersLogs | Aurora, Raccoon | 14/11/2022 | 14/11/2022 |
| DevilsTraff | Aurora, Raccoon | 30/10/2022 | 14/11/2022 |
| YungRussia | Aurora | 16/10/2022 | 31/10/2022 |
| Gfbg6 | Aurora | 14/09/2022 | 24/10/2022 |
| SAKURA | Aurora | 10/08/2022 | 04/11/2022 |
| HellRide | Aurora | 09/07/2022 | 15/07/2022 |
In October and November 2022, the researchers analyzed several hundreds of collected samples and identified dozens of active C2 servers. The experts also observed multiple infection chains leading to the deployment of Aurora stealer. The attackers used methods to deliver the malware, including phishing websites masquerading as legitimate ones, YouTube videos and fake “free software catalogue” websites.
“These infection chains leveraged phishing pages impersonating download pages of legitimate software, including cryptocurrency wallets or remote access tools, and the 911 method making use of YouTube videos and SEO-poised fake cracked software download websites.” reads the analysis by the experts.
The malware was also able to target 40 cryptocurrency wallets and applications like Telegram.
Threat actors behind this malware also advertised its loader capabilities, the malicious code in fact is able to deploy a next-stage payload using a PowerShell command.
“Aurora is another infostealer targeting data from browsers, cryptocurrency wallets, local systems, and acting as a loader. Sold at a high price on market places, collected data is of particular interest to cybercriminals, allowing them to carry out follow-up lucrative campaigns, including Big Game Hunting operations.” concludes the report. “As multiple threat actors, including traffers teams, added the malware to their arsenal, Aurora Stealer is becoming a prominent threat.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Aurora Stealer)
[adrotate banner=”5″]
[adrotate banner=”13″]


