
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

MageCart attack hit Australia bushfire Donors

A new MageCart attack made the headlines, crooks installed a software skimmer on a website that collects donations for the victims of the Australia bushfires. Experts from Malwarebytes have discovered a new Magecart attack that compromised a website collecting donations for the victims of the Australia bushfires. Crooks planted a malicious script on the website […]

australia bushfire donations

A new MageCart attack made the headlines, crooks installed a software skimmer on a website that collects donations for the victims of the Australia bushfires.

Experts from Malwarebytes have discovered a new Magecart attack that compromised a website collecting donations for the victims of the Australia bushfires.

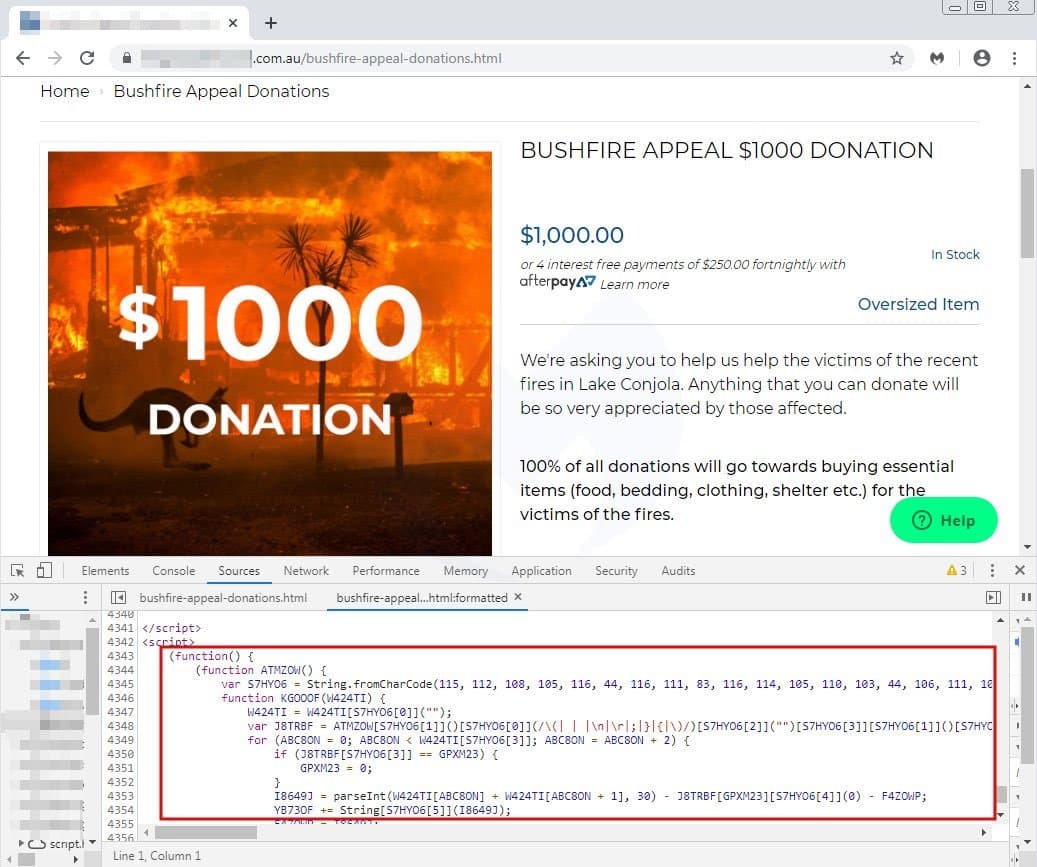
Crooks planted a malicious script on the website that was designed to steal the payment information of the donors and send them to a domain under the control of the attackers.

The software skimmer named ATMZOW was planted in the checkout page and is executed when visitors of the site adds an item to their cart.

australia bushfire donations
Source Bleeping Computer

Stolen credit card data are sent to the vamberlo[.]com domain.

“Malwarebytes’ Jérôme Segura has told BleepingComputer that once they became aware of the compromised site they were able to get the vamberlo[.]com shut down.” states the post published by Bleeping Computer.

The malicious domain used by the attackers was shut down, this means that the software skimmer is not able to send the stolen credit card data to the attackers, but we cannot exclude that attackers could use a different domain. The only way to secure the website is to remove the software skimmer, but the malicious code has yet to be removed.

Malwarebytes attempted to contact the owner of the website without success.

Unfortunately, many other e-commerce sites were compromised with the ATMZOW skimmer. Querying the PublicWWW online service for the malicious skimmer we can find it on tens of websites.

Recently other MageCart attacks were reported by security experts, last week experts reported that the Magecart group has compromised the website of the photography and imaging retailer Focus Camera.

Two distinct MageCart groups have compromised multiple European websites for the Perricone MD anti-aging skin-care brand with the intent of stealing customer payment card info.

A few days ago I reported the news of two Magecart groups that planted software skimmers on Perricone MD websites in Italy, Germany, and the U.K..

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – MageCart attack, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


