
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hackers broke into Australia’s Parliament Computer Network

Australia’s parliament confirmed that is investigating a suspicious security incident that affected its computer network. Australia announced an ongoing investigation on unspecified ‘security incident’ in the federal parliament’s computer network. “Following a security incident on the parliamentary computing network, a number of measures have been implemented to protect the network and its users,” parliamentary authorities […]

conti ransomware

Australia’s parliament confirmed that is investigating a suspicious security incident that affected its computer network.

Australia announced an ongoing investigation on unspecified ‘security incident’ in the federal parliament’s computer network.

“Following a security incident on the parliamentary computing network, a number of measures have been implemented to protect the network and its users,” parliamentary authorities said in a statement.

At the time of writing, authorities did not provide technical details on the security breach, officials said there was no initial evidence that data had been compromised by threat actors.

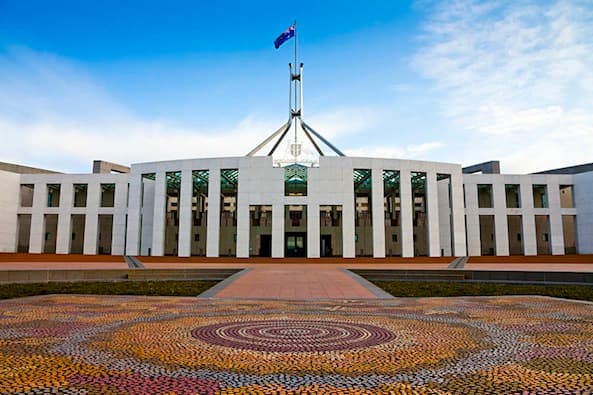
australian parliament house

Representatives from Australia’s Parliament did not release any statement on the attribution of the attack, but clearly, such kind of operations are usually associated with activities of nation-state actors.

“We have no evidence that this is an attempt to influence the outcome of parliamentary processes or to disrupt or influence electoral or political processes,” a statement said.

“Our immediate focus has been on securing the network and protecting data and users.”

In response to the incident, the IT staff reset passwords for all parliamentary

The Australian Signals Directorate (ASD) is also investigating the incident, according to the Australian broadcaster ABC intelligence agencies suspect the involvement of state-sponsored hackers.

“ASD and its Australian Cyber Security Centre will continue to work with (Parliament) to understand the full extent of this network compromise,” and ASD spokesperson told AFP.

“Meanwhile, the necessary steps are being taken to mitigate the compromise and prevent any harm.”

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Australia’s Parliament)

[adrotate banner=”5″] [adrotate banner=”13″]


