
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emsisoft released a new free decryption tool for the Avest ransomware

Emsisoft security firm has released a new free decryption tool for the Avest ransomware, a few days after the release of WannaCryFake decryptor. Emsisoft security firm has released a new free decryption tool for the Avest ransomware, a few days ago the researchers also released a free decryptor for the WannaCryFake ransomware. The Avest ransomware […]

Avest ransomware

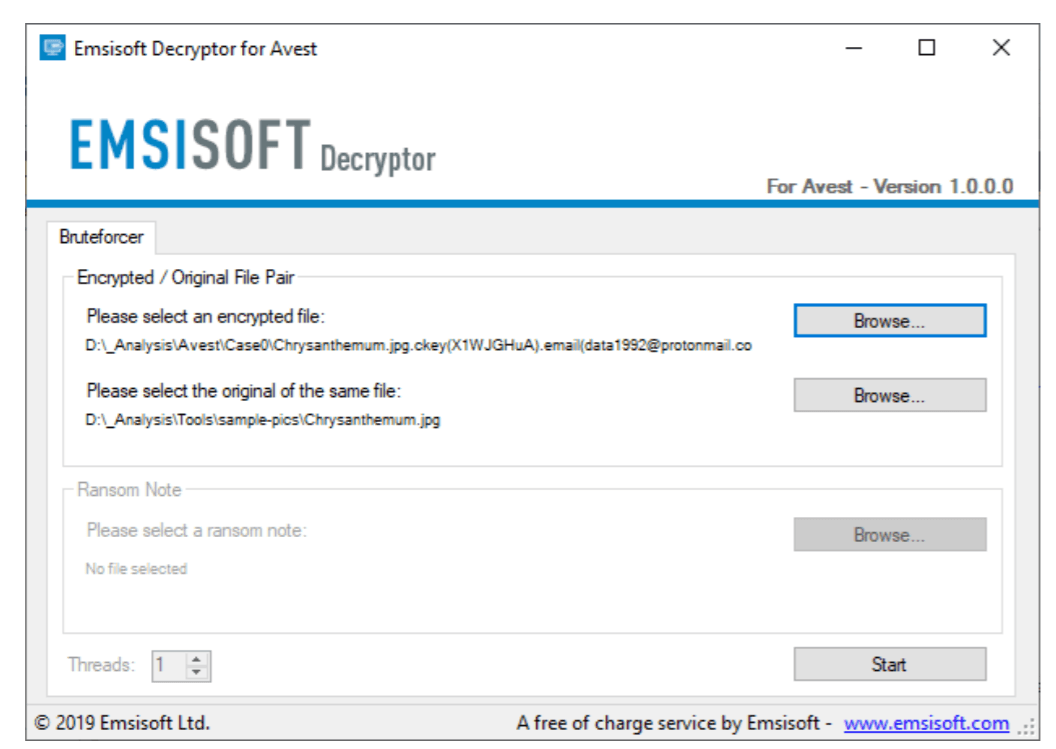
Emsisoft security firm has released a new free decryption tool for the Avest ransomware, a few days after the release of WannaCryFake decryptor.

Emsisoft security firm has released a new free decryption tool for the Avest ransomware, a few days ago the researchers also released a free decryptor for the WannaCryFake ransomware.

The Avest ransomware encrypts victim’s files and appends the extension “.ckey().email().pack14” to the filename.

Below the text of the ransom note “!!!Readme!!!Help!!!.txt” that the ransomware drops on the infected systems:

"Problems with your data? Contact us: data1992@protonmail[.]com key: <victim specific>”

The decryption tool could be used by the victims only after they have successfully removed the malware from their system to avoid that the Avest ransomware will repeatedly lock the machine or will encrypt files.

“The decryptor requires access to a file pair consisting of one encrypted file and the original, unencrypted version of the encrypted file to reconstruct the encryption keys needed to decrypt the rest of your data.” reads the user guide published by Emsisoft. “Please do not change the file names of the original and encrypted files, as the decryptor may perform file name comparisons to determine the correct file extension used for encrypted files on your system.”

Victims of the Avest ransomware can download the decryptor tool here:

https://www.emsisoft.com/ransomware-decryption-tools/avest

In August, security researchers at Emsisoft released a decryptor tool that allows the victims of the JSWorm 4.0 ransomware to decrypt their files for free. In May Emsisoft experts released a free Decrypter tool for the JSWorm 2.0 variant.

In July the company released other free decryptors for the LooCipher ransomware, the ZeroFucks ransomware, and the Ims00rry ransomware.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Avest ransomware, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


