
Security researchers from the Cisco Talos team uncovered a spear-phishing campaign targeting the aviation industry for two years avoiding detection.
Security researchers from Cisco Talos uncovered a spear-phishing campaign targeting, dubbed Operation Layover, that targeted the aviation industry for two years without being detected.
The experts believe that the threat actor behind this campaign is based out of Nigeria with a high degree of confidence and isn’t technically sophisticated. The group is suspected to have been running successful malware campaigns for more than five years. The attackers have used off-the-shelf malware since the beginning of their operations and have never developed their own malware.
Talos researchers believe that the group was able to remain under the radar using crypters that it bought on cybercrime forums.
The investigation into the activity of the group started after a tweet from Microsoft describing a series of attacks that employed the AsyncRAT.
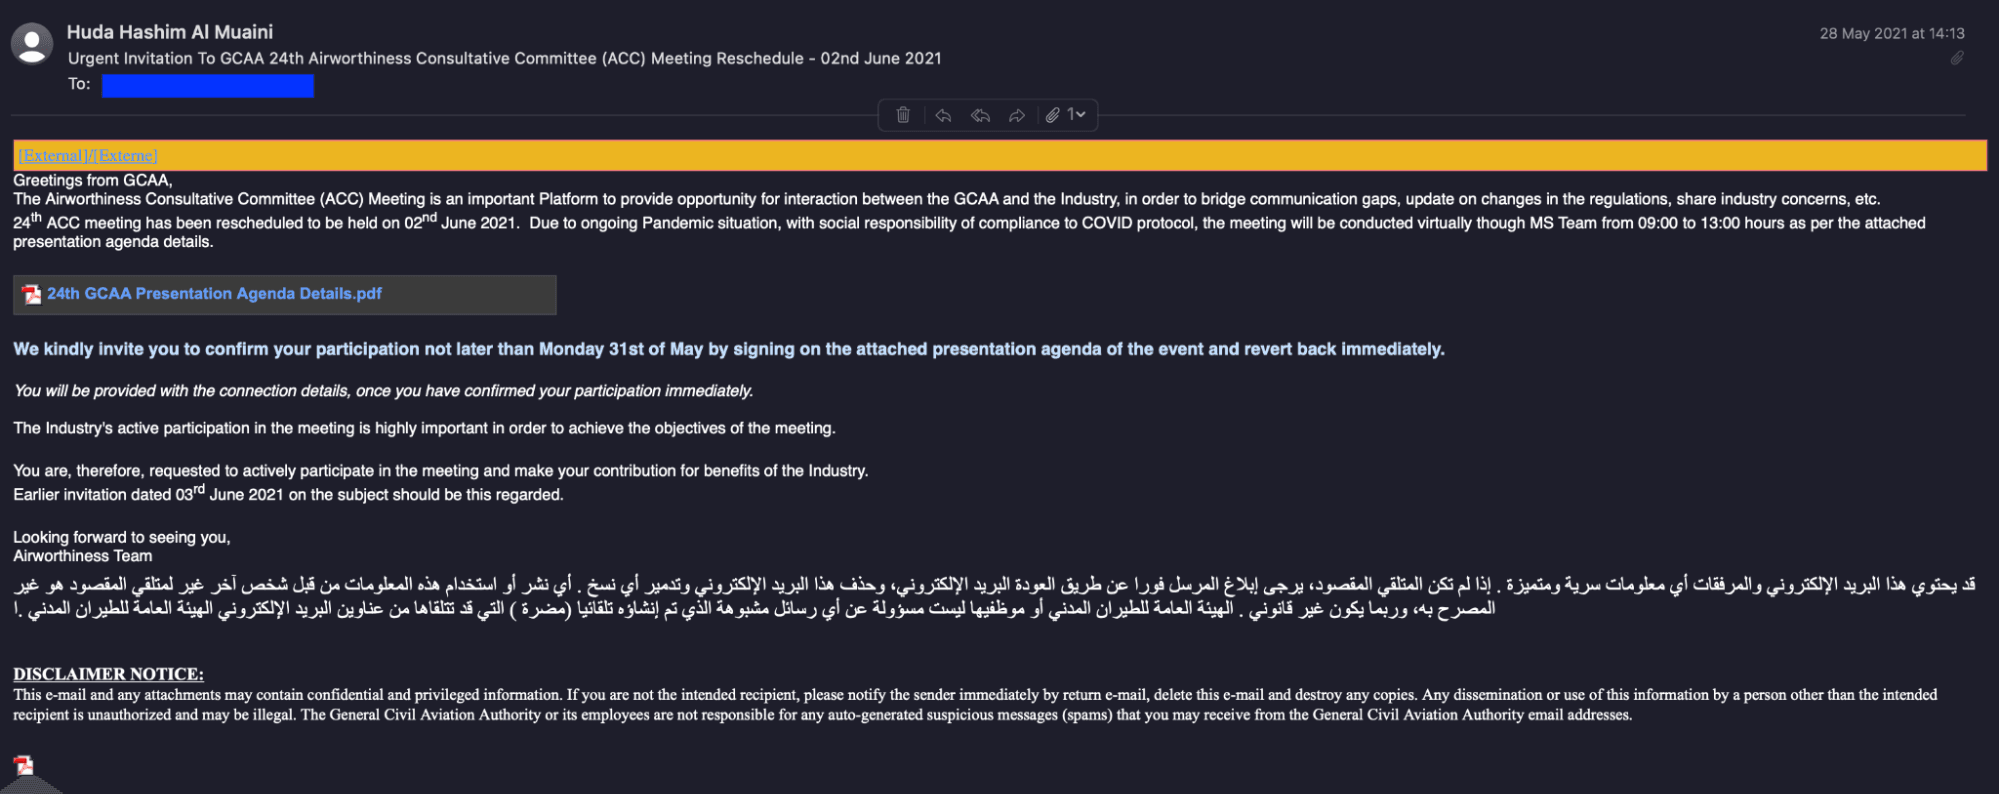
The spear-phishing messages use bait documents specifically crafted to target the aviation or cargo industry that purport to be PDF files but link to a VBScript file hosted on Google Drive, which ultimately leads to the delivery of remote access trojans (RATs) like AsyncRAT and njRAT.
“The actor behind these campaigns has been operating malware for more than five years and specifically targeting the aviation industry for at least two years. For this campaign, the actor used emails similar to the one below as the initial attack vector.” reads the analysis published by Cisco Talos. “These emails would appear to contain an attached PDF file that was a link to a .vbs file hosted on Google Drive.” Our research shows that this actor has been targeting the aviation industry since at least 2018, with files mentioning both “Trip Itinerary Details” and “Bombardier” at the time using the URL akconsult[.]linkpc[.]net.”

Evidence collected by the experts suggests that the threat actor has been active at least since 2013.
Further analysis of the operations associated with this threat actor revealed the use of different domains and RATs into their campaigns, including Cybergate RAT, AsyncRAT, and a batch file used to download and execute other malware.
“Many actors can have limited technical knowledge but still be able to operate RATs or information-stealers, posing a significant risk to large corporations given the right conditions. In this case, we have shown that what seemed like a simple campaign is, in fact, a continuous operation that has been active for three years, targeting an entire industry with off-the-shelf malware disguised with different crypters.” concludes the experts. These kinds of small operations tend to fly under the radar and even after exposure the actors behind them wont stop their activity. They abandon the C2 hostnames — which in this case are free DNS-based and they may change the crypter and initial vector, but they won’t stop their activity. The black market for web cookies, tokens and valid credentials is way too valuable when compared with the economy in their home countries for them to stop.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


