
Security Affairs
Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Avtech camera vulnerability actively exploited in the wild, CISA warns

CISA warned that an Avtech camera vulnerability, which is still unpatched, is being actively exploited in the wild. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) published an advisory to warn of a vulnerability, tracked as CVE-2024-7029 (CVSS base score of 8.8), in Avtech camera that has been exploited in the wild.  An attacker can exploit […]

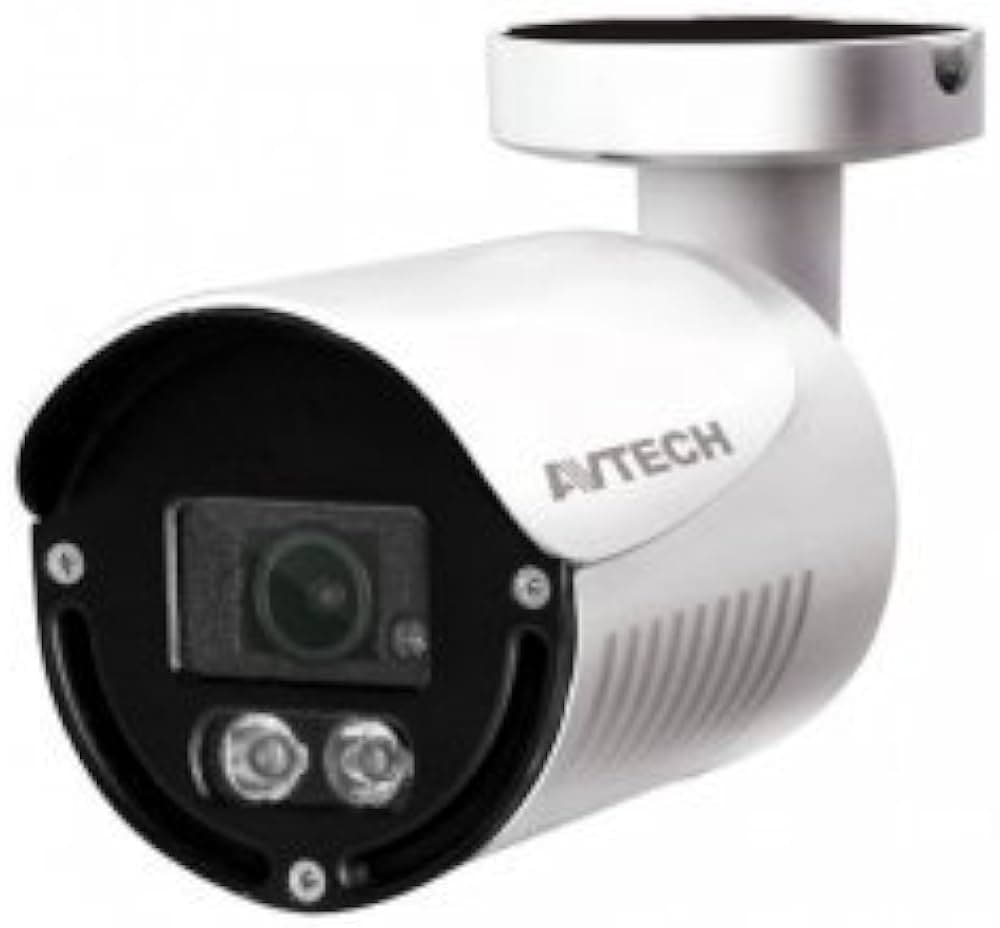
Avtech camera

CISA warned that an Avtech camera vulnerability, which is still unpatched, is being actively exploited in the wild.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) published an advisory to warn of a vulnerability, tracked as CVE-2024-7029 (CVSS base score of 8.8), in Avtech camera that has been exploited in the wild. 

An attacker can exploit this flaw to inject and execute commands as the owner of the running process.

“Successful exploitation of this vulnerability could allow an attacker to inject and execute commands as the owner of the running process.” reads the advisory published by CISA. “Commands can be injected over the network and executed without authentication.”

The vulnerability impacts Avtech AVM1203 IP cameras running firmware versions FullImg-1023-1007-1011-1009 and prior.

The US agency states that it is suspected that prior versions of other IP cameras and NVR (network video recorder) products are also affected.

The cyber security expert Larry Cashdollar of Akamai Technologies reported the vulnerability to CISA.

CISA attempted to report the issue to the vendor that has yet to respond to requests.

The US Agency advises users to reduce the risk of exploitation of the vulnerability CVE-2024-7029 by:

  1. Limiting network exposure of control system devices to prevent internet access.
  2. Placing control system networks and remote devices behind firewalls and isolating them from business networks.
  3. Using secure remote access methods like VPNs, ensuring they are up-to-date and recognizing their limitations.
  4. Conducting thorough impact analysis and risk assessment before implementing defensive measures.

Multiple botnets are known to target Avtech devices, including Mirai, Death botnet, Hide ‘N Seek and HNS.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)


