
A new version of the Azorult info-stealer appeared in the wild, it is able to steal more data, including other types of cryptocurrencies
A new version of the Azorult info-stealer appeared in the wild, it is able to steal more data, including other types of cryptocurrencies, and implements new features.
The latest version of the Azorult was delivered through the RIG exploit kit as well as other sources, previous variants were mainly distributed via weaponized Office documents as attachment of phishing messages.
AZORult is a data stealer that was first spotted in 2016 by Proofpoint that discovered it was it was part of a secondary infection via the Chthonic banking trojan. Later it was involved in many malspam attacks, but only in July 2018, the authors released a substantially updated variant.

In July, the experts discovered a new sophisticated version of the AZORult Spyware that was involved in a large email campaign on July 18.
The malicious code allows crooks to steal credentials, payment card data, browser histories and contents of cryptocurrency wallets.
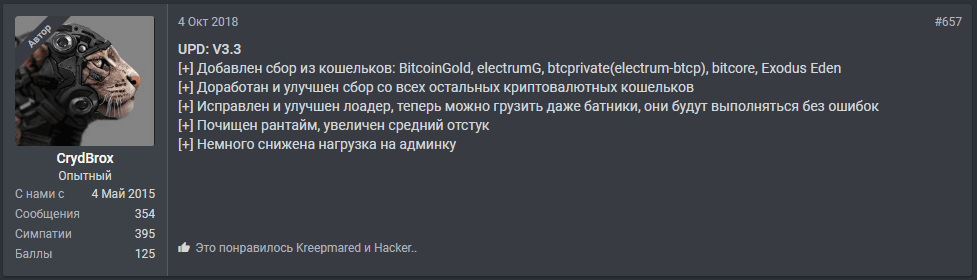
Now experts from Check Point have discovered a new version that is being advertised in an underground forum.

The new version is a substantial update of the previous one, authors implemented new features such as the ability to steal additional forms of cryptocurrency from the victims’ wallets, including BitcoinGold, electrumG, btcprivate (electrum-btcp), bitcore and Exodus Eden.
“During the last week, Check Point Research spotted a new version of Azorult in the wild being delivered through the RIG exploit kit, as well as other sources.” reads the analysis published by the experts.
“There are quite a few changes in this newly witnessed variant, the most prominent ones being a new encryption method of the embedded C&C domain string, a new connection method to the C&C and improvement of the Crypto currency wallets stealer and loader.”
The new variant implements a new encryption method used to protect the hardcoded C&C domain string. along with a new key for connecting to the command and control server.
The new variant was first offered for sale on October 4, a few days the source code for Azorult versions 3.1 and 3.2 were leaked online, earlier this month experts from CheckPoint discovered in the Dark Web an online builder, dubbed Gazorp, that allows crooks to create customized binaries for the Azorult malware.
Experts speculate the author of Azorult has released a new version of the data-stealer in response to the availability of leakage of the source code.
“Moreover, we have witnessed and written about another project related to Azorult, dubbed ‘Gazorp’ – a dark web binary builder that allows anyone to craft the malware’s binaries for free.” continues CheckPoint.
“Having this in minds, it is plausible that the Azorult’s author would like to introduce new features to the malware and make it worthy as a product in the underground market.” continues CheckPoint.
Further technical details, including IoCs are reported in the analysis published by CheckPoint.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Azorult , malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


