
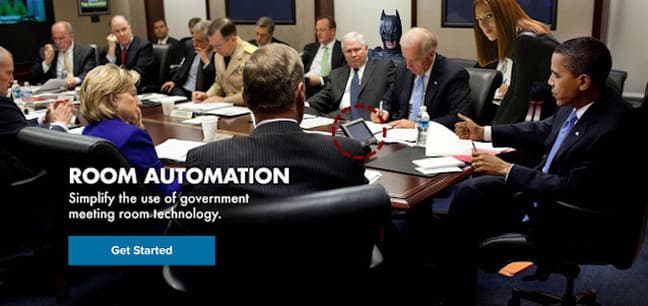
Experts from the security firm SEC Consult discovered a backdoor in the AMX equipment being used by US President Obama and the US Military.
AMX is a company that supplies communications systems and building control equipment to the US military, the White House and many other security organizations in the States. The particularity of these systems is the presence of a surveillance backdoor that could be used to hack or spy on users.
Researchers from the security firm SEC Consult have discovered the backdoor after conducting an analysis of the AMX NX-1200 equipment, it is a programmable network appliance specifically designed to control AV and building technology.
They became suspicious after noticing an unexpected function called “setUpSubtleUserAccount” that could be invoked to sets up a hidden account with abilities that are not available even to an administrator account. This new account implements specific “super powers,” including packet inspection and traffic sniffing, as well as access to the network interface.
The account could be accessed via the device’s built-in web interface or via SSH using a hardcoded password. The researchers discovered that the backdoor is present also in 30 other AMX products.
The discovery is disconcerting, most important US officials, including the US President currently use the AMX equipment for their communications, the same system is also used by a number of firms and organizations for their confidential conference, where discuss sensitive data information about their company.
“Although the backdoor vulnerability is quite a serious matter, we have published an accompanying blog post to this technical advisory which sheds a more funny light on this topic” states the Sec Consult.

Image sources, AMX: http://www.amx.com/government/_WebResources/imgs/slider_Automation_1920x1005.jpg Batman: http://hypesrus.com/files/the-dark-knight-rises-batman-1-4-scale-figure-by-hot-toys-1.jpg Black Widow: http://i2.wp.com/geekdad.com/wp-content/uploads/2014/04/blackwidow2.jpg
The author of the backdoor is clearly a fan of superheroes because the named the account Black Widow, aka Natalia “Natasha” Alianovna Romanova, a character from the Marvel, “one of the world’s greatest spies and master of disguise”, who is played on screen by Scarlett Johansson.

The experts from SEC Consult reported the issue to the AMX company early 2015, seven months later the firm updated the firmware of the AMX equipment but intentionally left the backdoor, just changing the username of the powerful account.
This time, the backdoor author has chosen another popular superhero for his powerful account called 1MB@tMaN (I’m Batman).
“Whatever the reason may be, the vendor decided to hire somebody from the DC universe this time. Na na na na na na na na … you guessed it. BATMAN! But not the usual Batman, the leet-hacker-Batman, who uses numbers and special characters to write his own name:
 |
| IDA excerpt: New backdoor username 1MB@tMaN |
” states the blog post published by the researchers.
AMX has now released a new patch for firmware indicted, the researchers from SEC Consul are already investigating the presence of the backdoor in the new software.
(Security Affairs – AMX equipment, backdoor)


