A critical vulnerability, named ‘BatBadBut’, impacts multiple programming languages, its exploitation can lead to command injection in Windows applications.
The cybersecurity researcher RyotaK (@ryotkak ) discovered a critical vulnerability, dubbed BatBadBut, which impacts multiple programming languages.
When specific conditions are satisfied, an attacker can exploit the flaw to perform command injection on Windows.
“The BatBadBut is a vulnerability that allows an attacker to perform command injection on Windows applications that indirectly depend on the CreateProcess function when the specific conditions are satisfied.” wrote the researcher. “CreateProcess() implicitly spawns cmd.exe when executing batch files (.bat, .cmd, etc.), even if the application didn’t specify them in the command line.“
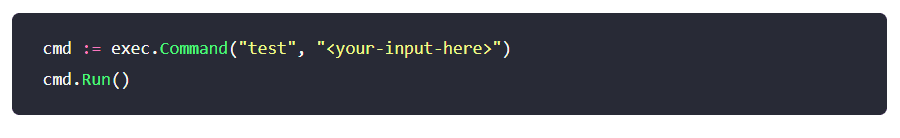
Due to Windows’ default inclusion of .bat and .cmd files in the PATHEXT environment variable, some runtimes inadvertently execute batch files instead of the intended commands. This can lead to arbitrary command executions, even if a snippet like the following one doesn’t explicitly include .bat or .cmd files.

RyotaK explained that OS executes batch files with ‘cmd exe’, which has complicated parsing rules for the command arguments, and programming language runtimes fail to escape the command arguments properly. The majority of programming languages provide their interface to the ‘CreateProcess’ function, however, they fail to escape the command arguments properly passed to the function.
Below is the list of conditions that must be satisfied to exploit BatBadBut:
- The application executes a command on Windows
- The application doesn’t specify the file extension of the command, or the file extension is
.bator.cmd - The command being executed contains user-controlled input as part of the command arguments
- The runtime of the programming language fails to escape the command arguments for
cmd.exeproperly2
The researcher already notified the maintainers of the impacted programming languages, who have taken steps to address the flaw.
The CERT/CC from Carnegie Mellon University published an advisory on this issue. Four different CVE identifiers, respectively CVE-2024-1874, CVE-2024-22423, CVE-2024-24576, and CVE-2024-3566, have been assigned to this issue.
“Various programming languages lack proper validation mechanisms for commands and in some cases also fail to escape arguments correctly when invoking commands within a Microsoft Windows environment.” reads the advisory. “The command injection vulnerability in these programming languages, when running on Windows, allows attackers to execute arbitrary code disguised as arguments to the command. This vulnerability may also affect the application that executes commands without specifying the file extension.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, data breach)