
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Noooo, now Ancient Tortoise BEC scammers are launching Coronavirus-Themed attacks

A cybercrime gang focused on Business Email Compromise (BEC) has started using coronavirus-themed scam emails in its attacks. While the Coronavirus is spreading worldwide cybercriminals and nation-state actors are launching COVID19-themed attacks on a global scale. Most of the attacks aimed at spreading malware to control victims’ computers and stealing sensitive data, but now a […]

coronavirus bec

A cybercrime gang focused on Business Email Compromise (BEC) has started using coronavirus-themed scam emails in its attacks.

While the Coronavirus is spreading worldwide cybercriminals and nation-state actors are launching COVID19-themed attacks on a global scale.

Most of the attacks aimed at spreading malware to control victims’ computers and stealing sensitive data, but now a cybercrime gang, tracked as Ancient Tortoise, is launching BEC attacks taking advantage of the COVID-19 outbreak.

According to a report shared by Agari Cyber Intelligence Division (ACID) researchers with BleepingComputer, crooks are launching Coronavirus-themed BEC attacks.

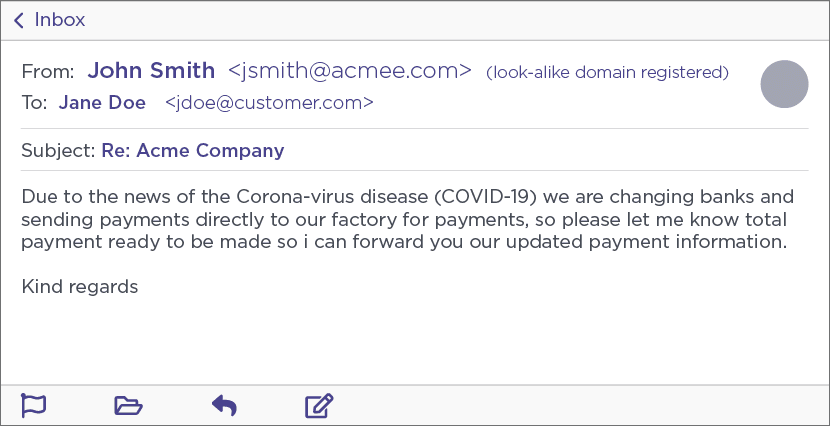
The researchers received a coronavirus-themed scam email that attempted to trick victims into using a different bank account for the payment due to the COVID-19 outbreak.

“Due to the news of the Corona-virus disease (COVID-19) we are changing banks and sending payments directly to our factory for payments, so please let me know total payment ready to be made so i can forward you our updated payment information,” reads the scam email.

The Ancient Tortoise’s BEC message includes details of a Hong Kong mule account and instructs victims to send the money to it.

Researchers noticed that it took about three weeks for the attackers to send the coronavirus-themed scam email after they have initially established a contact with them.

“It took about three weeks for the attackers to send the coronavirus-themed scam email after their initial contact with the researchers, between February 17th when the request for an aging report landed in Agari’s inboxes and March 9th when they launched the final attack on the fake vendor.” reported BleepingComputer.

To defend against BEC attacks, Agari experts recommend vendors and suppliers to implement strong email authentication and anti-phishing email protections.

Any organization that has regularly pay external suppliers is recommended to set up a formal process for handling outgoing payments, especially when some changes are reported in the normal payment procedure (i.e. A change of the bank account).

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, BEC)

[adrotate banner=”5″]

[adrotate banner=”13″]


