
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

SQL Dump from popular Indian BGR tech site leaked online

Hackers share SQL databases from unsecured AWS buckets, including the archive belonging to the BGR tech news site in India. Hackers are sharing SQL databases from unsecured Amazon S3 buckets, one of them belongs to the BGR tech news site in India. BGR, aka Boy Genius Report, is a popular technology-influenced website that covers topics […]

BGR

Hackers share SQL databases from unsecured AWS buckets, including the archive belonging to the BGR tech news site in India.

Hackers are sharing SQL databases from unsecured Amazon S3 buckets, one of them belongs to the BGR tech news site in India.

BGR, aka Boy Genius Report, is a popular technology-influenced website that covers topics ranging from consumer gadgets, to entertainment, gaming, and science. 

The data leak was first reported by experts from the security firm Under the Breach, the full SQL backup contains , emails, hashed passwords, and other information.

The site has about two million monthly users, it has over 210,000 followers on Twitter.

https://twitter.com/underthebreach/status/1232605676746289153

“A “full SQL dump” refers to all the posts on the site along with access credentials for authors and administrators. The potential for cybercriminal activity is obvious in this case.” reads a post on BleepingComputer.

“The researcher says that credentials were stored in hashed form, converted with a function in WordPress. In most cases, hackers pay to have the hashes cracked. On some specialized sites, this service is advertised at a reasonable price.”

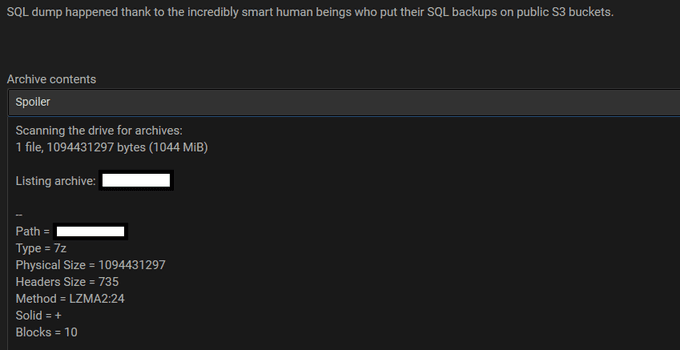
According to the hackers that shared the links to the archive, the overall dump contains at least 36,000 emails and logins for the affected websites (tradinggame.au.com, in, and S3 Production). Experts found 16 SQL dumps contained in a 7 ZIP archive.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, BGR)

[adrotate banner=”5″]

[adrotate banner=”13″]


