
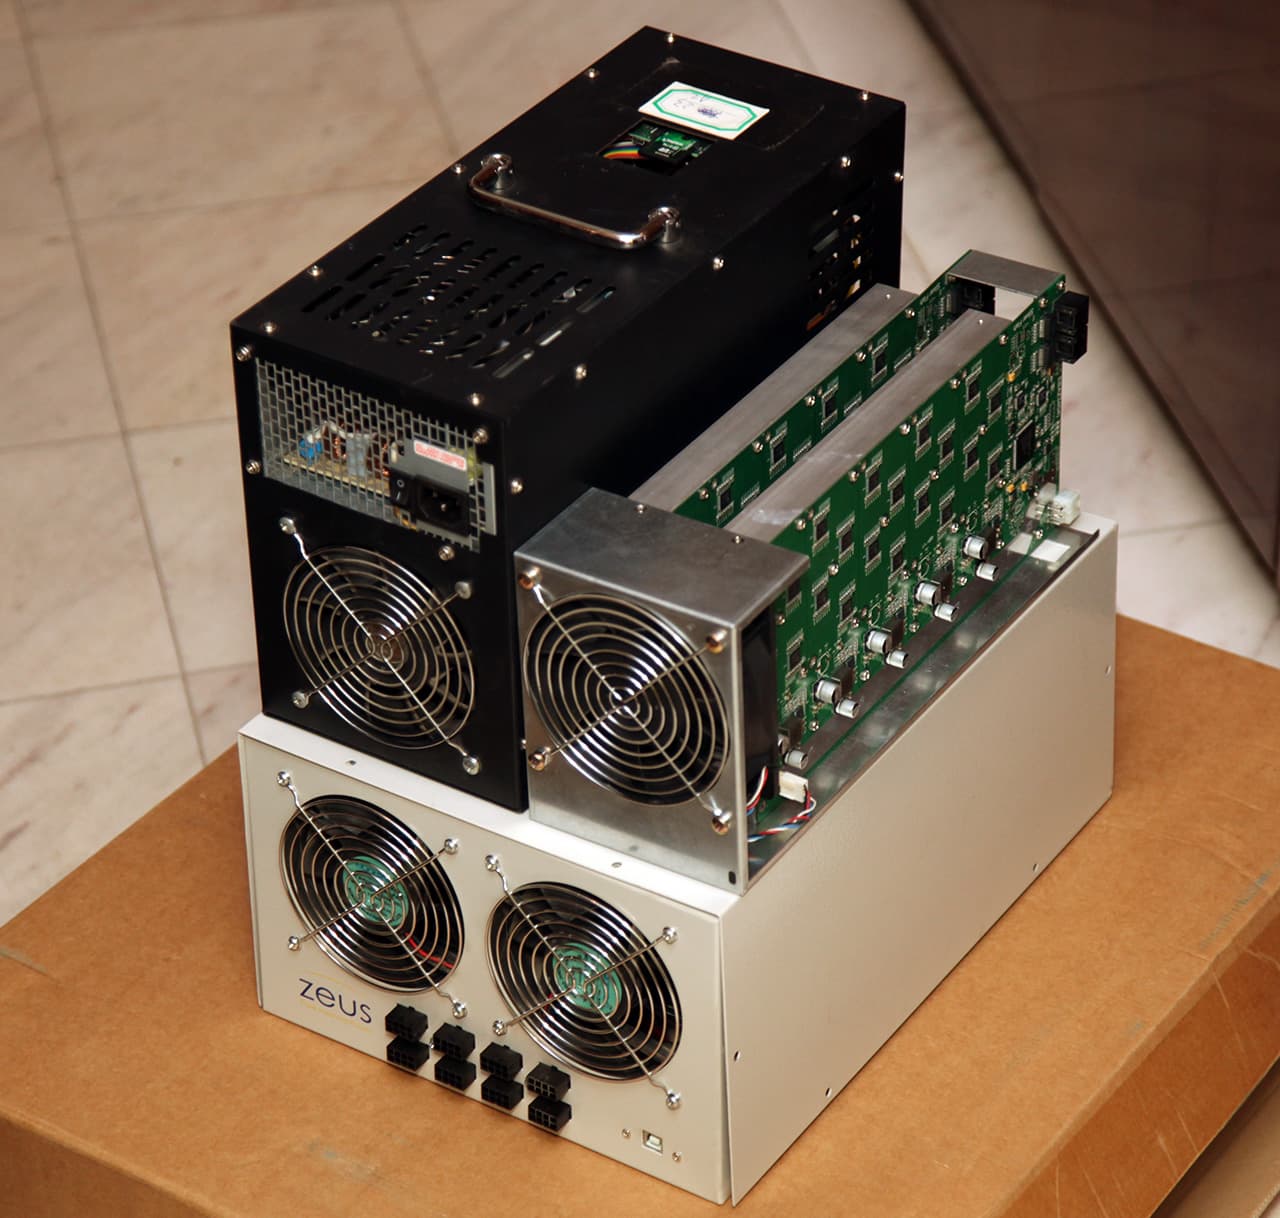
The popular Dutch security researcher Victor Gevers has discovered thousands of Bitcoin miners left exposed on the Internet.
The popular security researcher Victor Gevers, the founder of the GDI Foundation, has discovered 2,893 Bitcoin miners left exposed on the Internet.
I see about 2,893 Chinese Bitcoin "Thunder mining machines" online which are accessible via telnet w/o any password. Is the GFW down? pic.twitter.com/pGuBJnld5i
— Victor Gevers (@0xDUDE) August 28, 2017
The devices expose Telnet port with no password, the expert explained to Bleeping Computer that all miners belong to the same Bitcoin mining pool and likely are operated by the same organization.
Most of the devices are ZeusMiner THUNDER X3 Bitcoin miners.

The analysis of the IP addresses assigned to the Bitcoin Miners led to believe that the devices belong to a Chinese state-sponsored group.
“The owner of these devices is most likely a state sponsored/controlled organization part of the Chinese government, ” Gevers told Bleeping Computer.
Shortly after Gevers announced his discovery the operators behind the Bitcoin miners secured the exposed devices shortly after, the experts highlighted the speed in protecting the Bitcoin miners.
“Most of the miners are now not available anymore via Telnet,” Gevers told Bleeping Computer.
“At the speed they were taken offline, it means there must be serious money involved,” Gevers added. “A few miners is not a big deal, but 2,893 [miners] working in a pool can generate a pretty sum.”
A so huge botnet of miners could generate million dollars per months depending on the specific crypto currency they were mining.
The Twitter user @Quan66726078 speculate the botnet of 2,893 miners discovered by Gevers could generate an income of just over $1 million per day, in case operators use it to mine Litecoin cryptocurrency.
3) Then with power consumption about 1323 watt at price of 0.08 cent per kwH and mining Litecoin with 1 machine generates ~$379.000
— Quan (@Quan66726078) August 29, 2017
“I have proof of other visitors on the boxes where they tried to install a backdoor or malware,” Gevers said.
From XL_MINER_0001 to XL_MINER_2893. And no I am not the only visitor with admin privileges. These miners get visitors daily from everywhere pic.twitter.com/pOt1D4ChgL
— Victor Gevers (@0xDUDE) August 28, 2017
According to a researcher who goes online with the handle Anthrax0, the miners appeared to be participating in a bandwidth sharing scheme run via Chinese service Xunlei.
This is not any crypto currency miner. It's in fact a bandwidth/uploading affiliation program. You get rewarded for using the router as CDN.
— Anthr@X (@anthrax0) August 29, 2017
[adrotate banner=”9″]
(Security Affairs – Bitcoin Miners, Chine)
[adrotate banner=”12″]


