
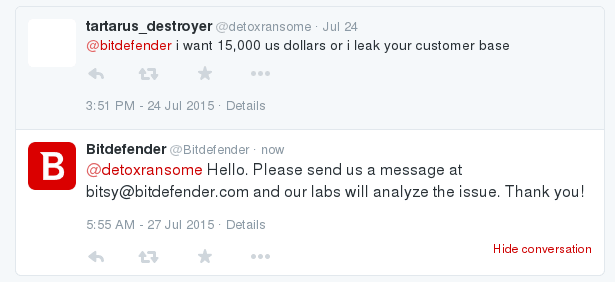
Antivirus firms BitDefender has been hacked and data belonging to its customer have been leaked online. Hackers requested a $15,000 ransomware.
Hackers are raising the bar, one of the most popular Antivirus firms BitDefender has been hacked and data belonging to its customer have been leaked online.
The data breach highlighted serious security issues in the way the company managed customer’s data, the incident for sure will have a serious impact on the reputation of the company.
A hacker, who uses the online pseudonymous DetoxRansome, has violated a server of the BitDefender company that hosted the cloud-based management dashboards for its small and medium-sized business clients. The company is currently working with law enforcement to investigate the issue.
The hackers exposed a list of credentials for more than 250 BitDefender accounts, as reported by the HackerFilm.
“Bitdefender, the critical darling in internet security, appears to have been hacked and is now embroiled in a dangerous extortion plot that’s putting its over 400 million customers at risk.
Friday July 24th 2015: A Hacker going by the handle DetoxRansome (DR) first attempted to blackmail the company via Twitter, writing “I want 15,000 us dollars or I leak your customer base”. This message was then followed by a tweet containing login credentials for two Bit Defender staff members’ accounts and another one belonging to a customer.” reported the HackerFilm.
The hacker has compromised users’ credentials, and the worst news is that the login details were in plain text.

The company has admitted the data breach, it also added that the hackers haven’t penetrated the company network, but they likely exploited a security hole that “potentially enabled exposure of a few user accounts and passwords.”
This means that the incident affected a limited number of users, the attacker exploited a SQL injection vulnerability in order to access users’ data.
Who is behind the attack?
The attack appears to be financially-motivated, the hackers are threatening to release the leaked data publicly unless the ransom of $15,000 is paid by BitDefender.

Of course, Bitdefender refused to pay the ransom and immediately worked to identify and fix the flaw exploited by the hackers.
“The issue was immediately resolved, and additional security measures have been put in place to prevent its reoccurrence,” BitDefender spokesperson said in a statement. “Our investigation revealed no other server or services were impacted.”
DetoxRansome confirmed that he is currently infiltrating networks of Bitdefender customers.
“I’m sniffing one of their major servers stealing logins”
The news could not be confirmed at the time I was writing, Bit Defender is resetting customers’ passwords.
Stay tuned …
[adrotate banner=”9″]
(Security Affairs – Bitdefender, data breach)


