
Experts warn of a new malware campaign using sensitive information stolen from a bank as a lure to spread the remote access trojan BitRAT.
Qualys experts spotted a new malware campaign spreading a remote access trojan called BitRAT using sensitive information stolen from a bank as a lure in phishing messages.
BitRAT is a relatively new threat advertised on underground marketplaces and forums since Feb 2021, it is offered for $20. The RAT supports the following capabilities:
- Data exfiltration
- Execution of payloads with bypasses.
- DDoS
- Keylogging
- Webcam and microphone recording
- Credential theft
- Monero mining
- Running tasks for process, file, software, etc.
While investigating multiple lures for BitRAT, the researchers discovered that a threat actor had hijacked the IT infrastructure of a Columbian cooperative bank and likely gained access to customers’ data.
Then the attackers use lures containing sensitive data from the bank to trick victims into installing the malware.
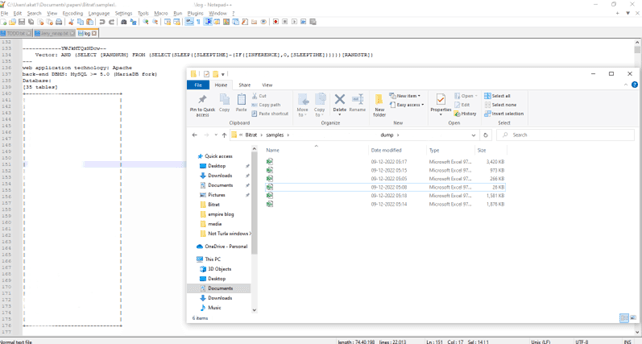
The researchers discovered that the threat actors had access to a database containing 4,18,777 rows of customers’ sensitive data, including Cedula numbers (Columbian national ID), email addresses, phone numbers, customer names, payment records, salary, address etc.
The threat actors exported the data in weaponized Excel maldocs and used them in phishing emails crafted to trick recipients into opening the file.
Upon opening the file and enabling the macro, a second-stage DLL payload is downloaded and executed. The second-stage DLL uses various anti-debugging techniques, it retrieves and executes BitRAT on the compromised host.

“The excel contains a highly obfuscated macro that will drop an inf payload and execute it. The .inf payload is segmented into hundreds of arrays in the macro. The de-obfuscation routine performs arithmetic operations on these arrays to rebuild the payload. The macro then writes the payload to temp and executes it via advpack.dll.” reads the analysis published by the experts. “The .inf file contains a hex encoded second stage dll payload which is decoded via certutil, written to %temp%\ and executed by rundll32. The temp files are then deleted.”
The obfuscated BitRAT loader samples were hosted on a GitHub repository that was created in mid-November 2022.
The BitRAT loader samples are obfuscated via DeepSea. The experts reported that the BitRAT sample is embedded into the loaders and is obfuscated via SmartAssembly. The loader decodes the binary and reflectively loads them.
“Commercial off the shelf. RATs have been evolving their methodology to spread and infect their victims.” concludes the report. “They have also increased the usage of legitimate infrastructures to host their payloads and defenders need to account for it.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, BitRAT)
[adrotate banner=”5″]
[adrotate banner=”13″]


