
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

BlackCat ransomware group claims the hack of Seiko network

The BlackCat/ALPHV ransomware group claims to have hacked the Japanese maker of watches Seiko and added the company to its data leak site. On August 10, 2023, the Japanese maker of watches Seiko disclosed a data breach following a cyber attack. “Seiko Group Corporation (hereinafter referred to as “the Company” or “we”) has confirmed that […]

Seiko blackcat ransomware

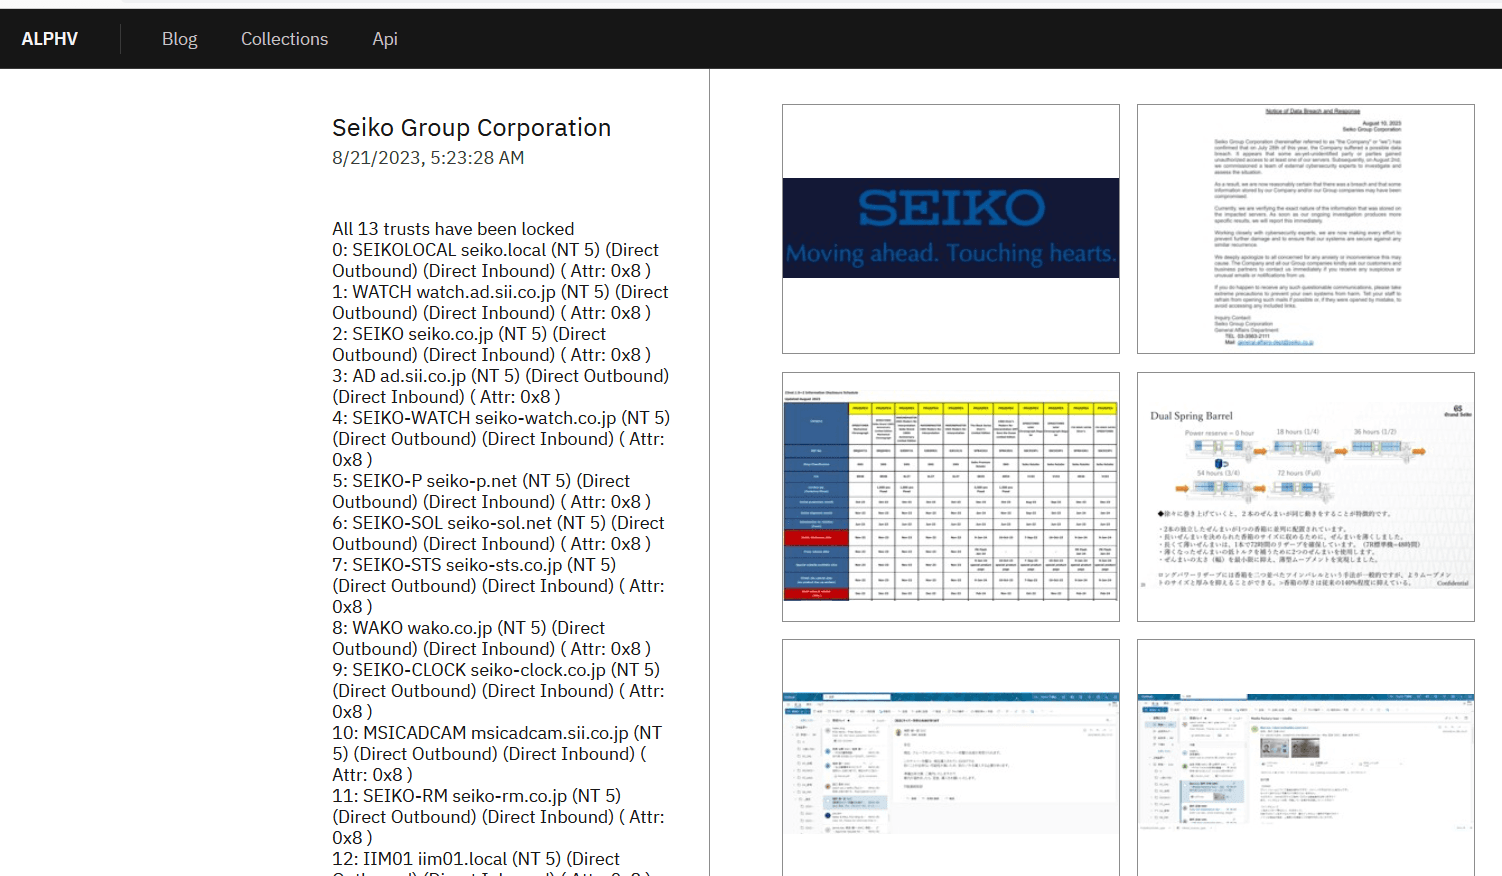
The BlackCat/ALPHV ransomware group claims to have hacked the Japanese maker of watches Seiko and added the company to its data leak site.

On August 10, 2023, the Japanese maker of watches Seiko disclosed a data breach following a cyber attack.

“Seiko Group Corporation (hereinafter referred to as “the Company” or “we”) has confirmed that on July 28th of this year, the Company suffered a possible data breach. It appears that some as-yet-unidentified party or parties gained unauthorized access to at least one of our servers. Subsequently, on August 2nd, we commissioned a team of external cybersecurity experts to investigate and assess the situation.” reads a notice published by the company. “As a result, we are now reasonably certain that there was a breach and that some information stored by our Company and/or our Group companies may have been compromised.”

Threat actors gained access to the network of the company and stole some data from its systems.

Now the BlackCat/ALPHV ransomware gang has added Seiko to the list of victims published on its data leak site.

Seiko blackcat ransomware

The group published samples of some data allegedly exfiltrated from the company network, including passport scans and projects of new watches.

It is still unclear if the hackers have stolen company secrets or intellectual property, such as patented technologies used for its products.

The ransomware group states that the company has low security of its networks and products.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Seiko)


