
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hackers behind the BLACKGEAR espionage campaign now targets Japan

The threat actor behind the Blackgear cyber-espionage campaign that is targeting Japanese entities is the same that hit Taiwan in 2012. According to security experts from Trend Micro, Japanese organizations were targeted in an espionage campaign dubbed Blackgear. Attackers behind the Blackgear appear to be the same that targeted users in Taiwan in 2012, they used […]

Hackers behind the BLACKGEAR espionage campaign now targets Japan

The threat actor behind the Blackgear cyber-espionage campaign that is targeting Japanese entities is the same that hit Taiwan in 2012.

According to security experts from Trend Micro, Japanese organizations were targeted in an espionage campaign dubbed Blackgear.

Attackers behind the Blackgear appear to be the same that targeted users in Taiwan in 2012, they used a well-known strain of malware detected by many security firms as Elirks.

The attack vectors are spear phishing emails or compromised websites used to serve the malware in watering hole attack. The websites used in the watering hole attacks were used to download a malicious code that drops decoy documents and the downloaders used to fetch the backdoors used by the group (i.e. Elirks and Ymalr).

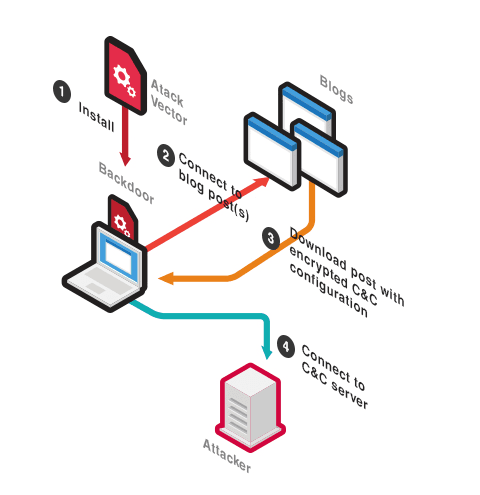
The researchers noticed that the both Elirks and Ymalr used as command and control (C&C) infrastructure blogging services in order to make harder their detection and , allowing the attackers to keep the location of the actual C&C server hidden and easily change the server that is in use.

“BLACKGEAR is an espionage campaign which has targeted users in Taiwan for many years. Multiple papers and talks have been released covering this campaign, which used the ELIRKS backdoor when it was first discovered in 2012. It is known for taking using blogs and microblogging services to hide the location of its actual command-and-control (C&C) servers. This allows an attacker to change the C&C server used quickly by changing the information in these posts.” read the blog post published by TrendMicro.

“Like most campaigns, BLACKGEAR has evolved over time. Our research indicates that it has started targeting Japanese users. “

blackgear

The researchers speculate the BLACKGEAR has evolved over time and threat actors behind the espionage campaign now moved to Japan. The decoy documents used in the attacks are now in Japanese and the blogging services used as part of the C&C infrastructure are based in Japan.

The experts from PaloAlto Network arrived at the same conclusion after they noticed some cyber attacks against organizations in Japan this summer that presented many similarities with attacks against targets in Taiwan.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – BLACKGEAR , Japan)


