
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

BlackMatter ransomware also targets VMware ESXi servers

BlackMatter gang rapidly evolves, the group has developed a Linux version that allows operators to targets VMware’s ESXi VM platform. The BlackMatter ransomware gang has implemented a Linux encryptor to targets VMware ESXi virtual machine platform. This is the last ransomware in order of time that is able to target VM platforms, some of the […]

BlackMatter ransomware Darkside

BlackMatter gang rapidly evolves, the group has developed a Linux version that allows operators to targets VMware’s ESXi VM platform.

The BlackMatter ransomware gang has implemented a Linux encryptor to targets VMware ESXi virtual machine platform. This is the last ransomware in order of time that is able to target VM platforms, some of the other ransomware operations that do the same are REvil, RansomExx/Defray, Mespinoza, HelloKitty, and Babuk.

BlackMatter operators developed the Linux version to expand the list of targets and compromise virtualized environments.

The BlackMatter group launched its operations at at the end of July, the gang claims to be the successor of Darkside and REvil groups. Lile other ransomware operations, BlackMatter also set up its leak sitewhere it will publish data exfiltrated from the victims before encrypting their system.

The birth of the BlackMatter ransomware was first spotted by researchers at Recorded Future who also reported that the gang is setting up a network of affiliates using ads posted on two cybercrime forums, such as Exploit and XSS.

The group is recruiting crooks with access to the networks of large enterprises, which have revenues of $100 million/year or larger, in an attempt to infect them with its ransomware. The group is looking for corporate networks in the US, the UK, Canada, or Australia.

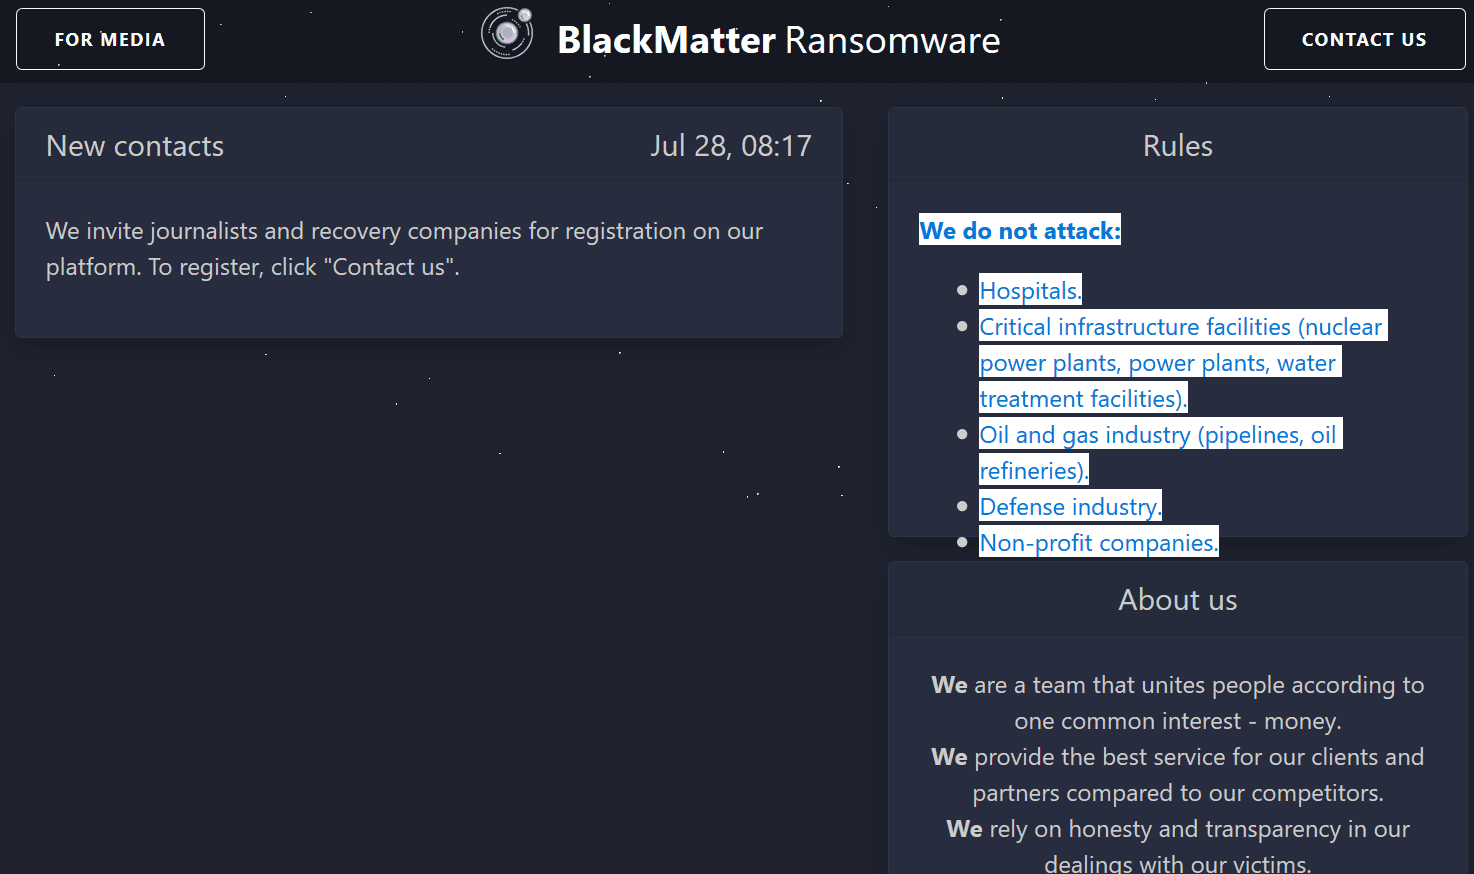
BlackMatter ransomware operators announced that they will not target healthcare organizations, critical infrastructure, organizations in the defense industry, and non-profit companies.

BlackMatter forum-post
BlackMatter forum post – Source THE RECORD

This week, researchers from MalwareHunterTeam first spotted a Linux ELF64 encryptor for the BlackMatter ransomware gang that was designed to target VMware ESXi servers.

Malware researcher Vitali Kremez analyzed the sample and confirmed it was a BlackMatter variant that targets VMware ESXi servers.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, BlackMatter ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


