Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Hacking

Is the Blackphone really so easy to root? Probably no.

A security researcher claimed to have rooted the super secure Smartphone Blackphone in just five minutes. Is it true? What’s happened? Recently we read about the Blackphone, a super secure smartphone designed by SGP Technologies, a joint venture between Silent Circle and Spanish Geekphone, which is able to avoid surveillance of the NSA. The designer of Blackphone […]

Is the Blackphone really so easy to root? Probably no.

A security researcher claimed to have rooted the super secure Smartphone Blackphone in just five minutes. Is it true? What’s happened?

Recently we read about the Blackphone, a super secure smartphone designed by SGP Technologies, a joint venture between Silent Circle and Spanish Geekphone, which is able to avoid surveillance of the NSA. The designer of Blackphone defined it as the “world’s first Smartphone which places privacy and control directly in the hands of its users,”.

Security expert Jon Sawyer (@TeamAndIRC), CTO of Applied Cybersecurity, at the recent DEF CON hacker conference demonstrated that Blackphone is vulnerable, they have rooted the super smartphone in just 5 minutes.  The security researcher took 5 minutes to root the device without unlocking the device’ bootloader.

The principal problem is that the researcher didn’t know to have tested a phone with old firmware and that the designers of Blackphone had already patched one of the vulnerabilities and pushed out the update.


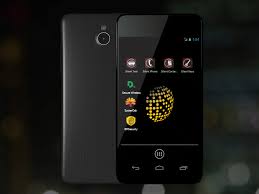
Blackphone 1

Blackphone is based on a customized version of Android dubbed PrivatOS which comes with pre-installed privacy-enabled applications. The Blackphone was criticized by some security experts which consider the mobile phone only a container of privacy tools, that anyway runs on Android OS.

BlackBerry dubbed the devices of its competitor as “Consumer-Grade Privacy That’s Inadequate for Businesses.”

@TeamAndIRC described three ways to hack the Blackphone:

  • USB debugging/dev menu removed, open via targeted intent
  • remote wipe app runs as system, and is debuggable, attach debugger get free system shell
  • system user to root, many available

blackphone hacked 11082014

Later the researcher noticed later that the first of the above hacks was conducted on an unpatched version of Android, meanwhile the second attack required user interaction.

Resuming, one of the flaws has been already patched and the other is only exploitable with direct user consent, for this reason there is no imminent danger to Blackphone users.
Regarding the third issue, Sawyer said that he will privately disclose it to SGP Technologies Team, and he remarked that “it is hard to reach and trigger, requiring priv(ilege) escalation to even attempt, and of little value.”
Anyway a bad actor needs to have physical access to the Blackphone.

Dan Ford, chief security officer at SGP Technologies, explained that the debugging attack is not a vulnerability as the Android Debugging Bridge is a part of Android itself.

“We turned ADB off because it causes a software bug and potentially impacts the user experience, a patch is forthcoming,” “I would like to thank him for not blowing the issue out of proportion and going back to the twittersphere for a little more transparency by explaining that direct user interaction is required and that we had already patched one of the vulnerabilities through the OTA update.” Ford says in a blog post.

It’s my opinion that the perfect software doesn’t exist, bugs are everywhere, let’s think to the recent flaw in Tor and in Tails like distribution, I have appreciated how Blackphone team managed the news and promptly identified and fixed the alleged flaws.

Pierluigi Paganini

(Security Affairs –  Blackphone, hacking)