Security Affairs
The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Iranian developer advertised BlackRouter RaaS

An Iranian developer is promoting on a Telegram hacking channel the BlackRouter ransomware through a Ransomware-as-a-Service model. An Iranian developer is advertising on Telegram a Ransomware-as-a-Service called BlackRouter. The same expert advertises other malware and is believed to the author of another ransomware called Blackheart. promotes other infections such as a RAT. BlackRouter was first […]

blackrouter 2

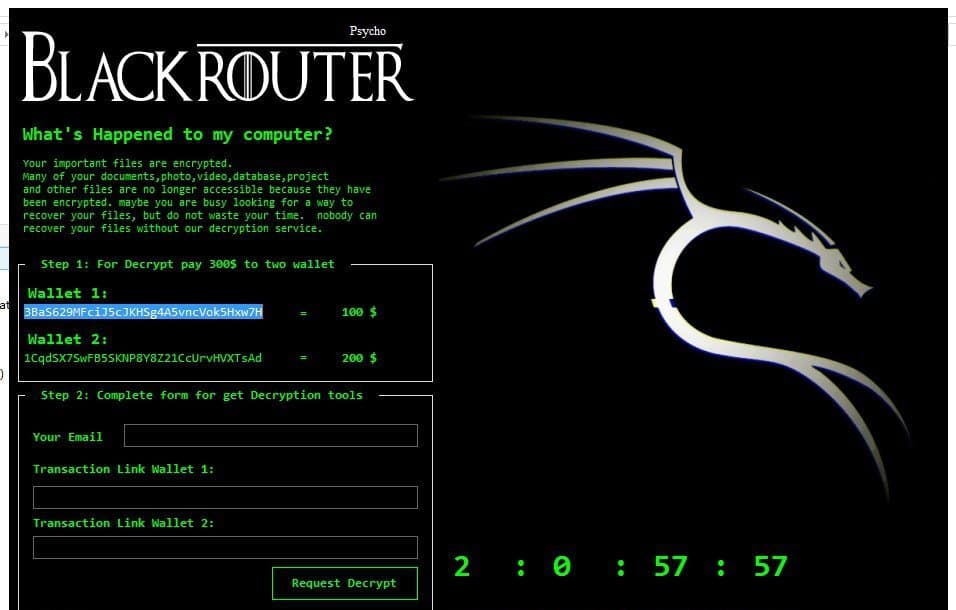
An Iranian developer is promoting on a Telegram hacking channel the BlackRouter ransomware through a Ransomware-as-a-Service model.

An Iranian developer is advertising on Telegram a Ransomware-as-a-Service called BlackRouter. The same expert advertises other malware and is believed to the author of another ransomware called Blackheart.
promotes other infections such as a RAT.

BlackRouter was first observed in May 2018, at the time experts at TrendMicro discovered legitimate application AnyDesk bundled with the Ransomware.

According to Bleeping Computer, security researcher Petrovic discovered a new variant of the BlackRouter Ransomware in January, but the MalwareHunterTeam stated that only differences between this variant and previous ones were an improved GUI and the implementation of a timer.

blackrouter 2

A researcher that goes online with the handle A Shadow told BleepingComputer that the same ransomware was offered as a RaaS platform in a hacking channel on Telegram by an Iranian developer. 

The developer offers to its customers 80% of paid ransom payments, keeping for him the remaining 20%.

BlackRouter

At the time, the BlackRouter was not widespread, Bleeping Computer reports only one submission to ID Ransomware since December 31.

The ransomware was mainly distributed via RDP accesses or through fake cracks and downloads.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – ransomware-as-a-service, malware)

[adrotate banner=”5″] [adrotate banner=”13″]