
A ransomware attack by the BlackSuit group on Young Consulting compromised the personal information of over 950,000 individuals.
Software solutions provider Young Consulting disclosed a data breach impacting 950,000 individuals following a BlackSuit ransomware attack.
On April 13 the company “became aware of technical difficulties” that impacted its infrastructure. Attackers gained access to the company network between April 10, 2024, and April 13, 2024, and stole certain files.
“On April 13, 2024, Young Consulting became aware of technical difficulties in our computer environment. We immediately took certain systems offline to contain the incident and launched an investigation, with the assistance of a cybersecurity forensics firm, to determine the nature and scope of the event.” reads a notice of data breach published by the company. “The investigation determined that an unauthorized actor gained access to Young Consulting’s network between April 10, 2024, and April 13, 2024, and downloaded copies of certain files.”
Compromised data varies by individual and may include a combination of certain individuals’ names, Social Security numbers, date of birth, and insurance policy/claim information.
The company maker did not share details about the attack. According to the data breach notification shared by the company with the Maine Attorney General’s Office, the incident impacted 954,177 people.
The investigation conducted by Young Consulting revealed that information related to certain data owners, including Blue Shield, was accessed by an unauthorized actor during a security breach. The company is still reviewing the impacted files and identifying affected individuals. On June 28, 2024, Young Consulting confirmed the breach to Blue Shield and has started notifying the individuals whose information may have been compromised.
“Blue Shield of California received notification from Young Consulting, Inc., a third-party vendor who provides risk management services, that it experienced a data security event which potentially impacted the health plan members’ information.” reads an incident notice published by Blue Shield.
The software maker offers one year of free credit monitoring services to the impacted individuals.

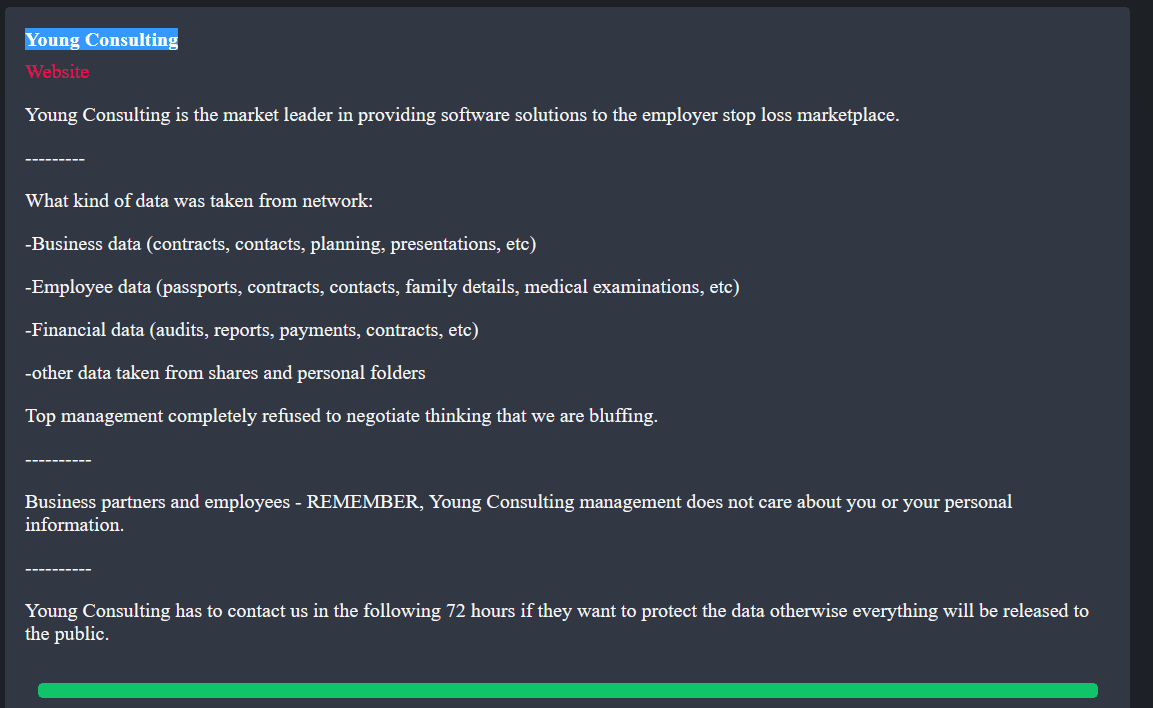
In May, the BlackSuit ransomware group added Young Consulting to the list of victims on its Tor leak site. The ransomware gang claimed the theft of the following information:
- Business data (contracts, contacts, planning, presentations, etc)
- Employee data (passports, contracts, contacts, family details, medical examinations, etc)
- Financial data (audits, reports, payments, contracts, etc)
- other data taken from shares and personal folders
The group added that top management completely refused to negotiate thinking that they were bluffing.
The stolen data are now available for download.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ransomware)


