Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A new Bluetooth overlay skimmer block chip-based transactions

Experts discovered a new Bluetooth overlay skimmer that interferes with the ability of the terminal to read chip-based cards, forcing the use of the stripe. The popular investigator Brian Krebs reported the discovery of a new Bluetooth overlay skimmer that interfered with the terminal’s ability to read chip-based cards, forcing the use of the magnetic […]

Overlay Skimmer

Experts discovered a new Bluetooth overlay skimmer that interferes with the ability of the terminal to read chip-based cards, forcing the use of the stripe.

The popular investigator Brian Krebs reported the discovery of a new Bluetooth overlay skimmer that interfered with the terminal’s ability to read chip-based cards, forcing the use of the magnetic stripe. The device was found in an unnamed retail chain in the United States.

The payment card skimmer included a PIN pad overlay and was able to physically block chip-based transactions.

The PIN pad overlay was designed to capture, store and transmit via Bluetooth payment card data stolen on the stripe along with the PIN provided by the clients on the terminal.

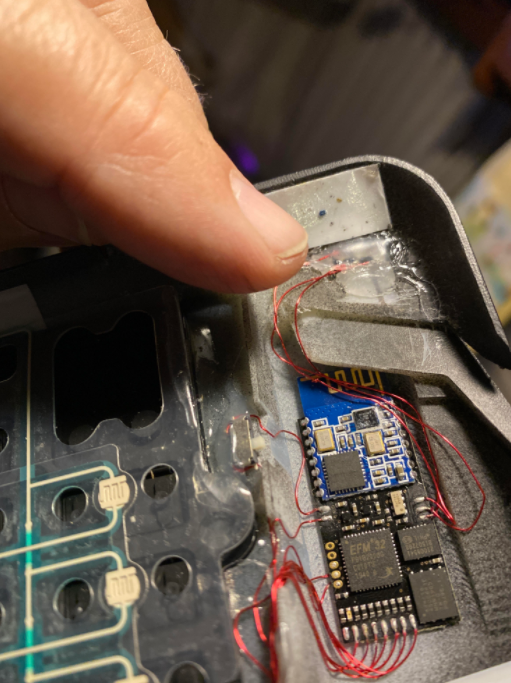
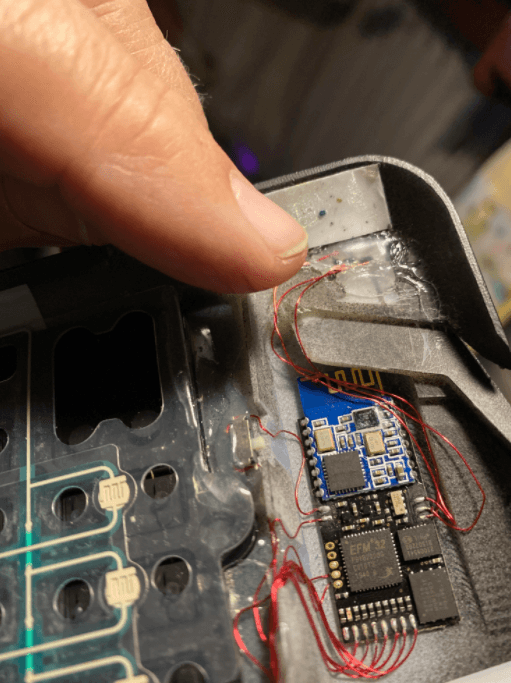
“The hidden magnetic stripe reader is in the bottom left, just below the Bluetooth circuit board. A PIN pad overlay (center) intercepts any PINs entered by customers; the cell phone battery (right) powers all of the components.” wrote Brian Krebs on Krebsonsecurity.com.

Chip-based payment cards are more difficult to clone, for this reason, crooks forced the use of the magnetic stripe present on the card for backward compatibility. The recently discovered overlay skimmer included a physical component that blocks chip-based transactions on the terminal, forcing the customer to swipe the stripe.

Krebs explained that the overlay skimmer was undetected for several weeks.

Krebs pointed out that once obtained the payment card data and the PIN, cybercriminals can clone the card and use them to withdraw money at an ATM.

If you want to receive the weekly Security Affairs Newsletter for free subscribe here.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Skimmer)

[adrotate banner=”5″]

[adrotate banner=”13″]