
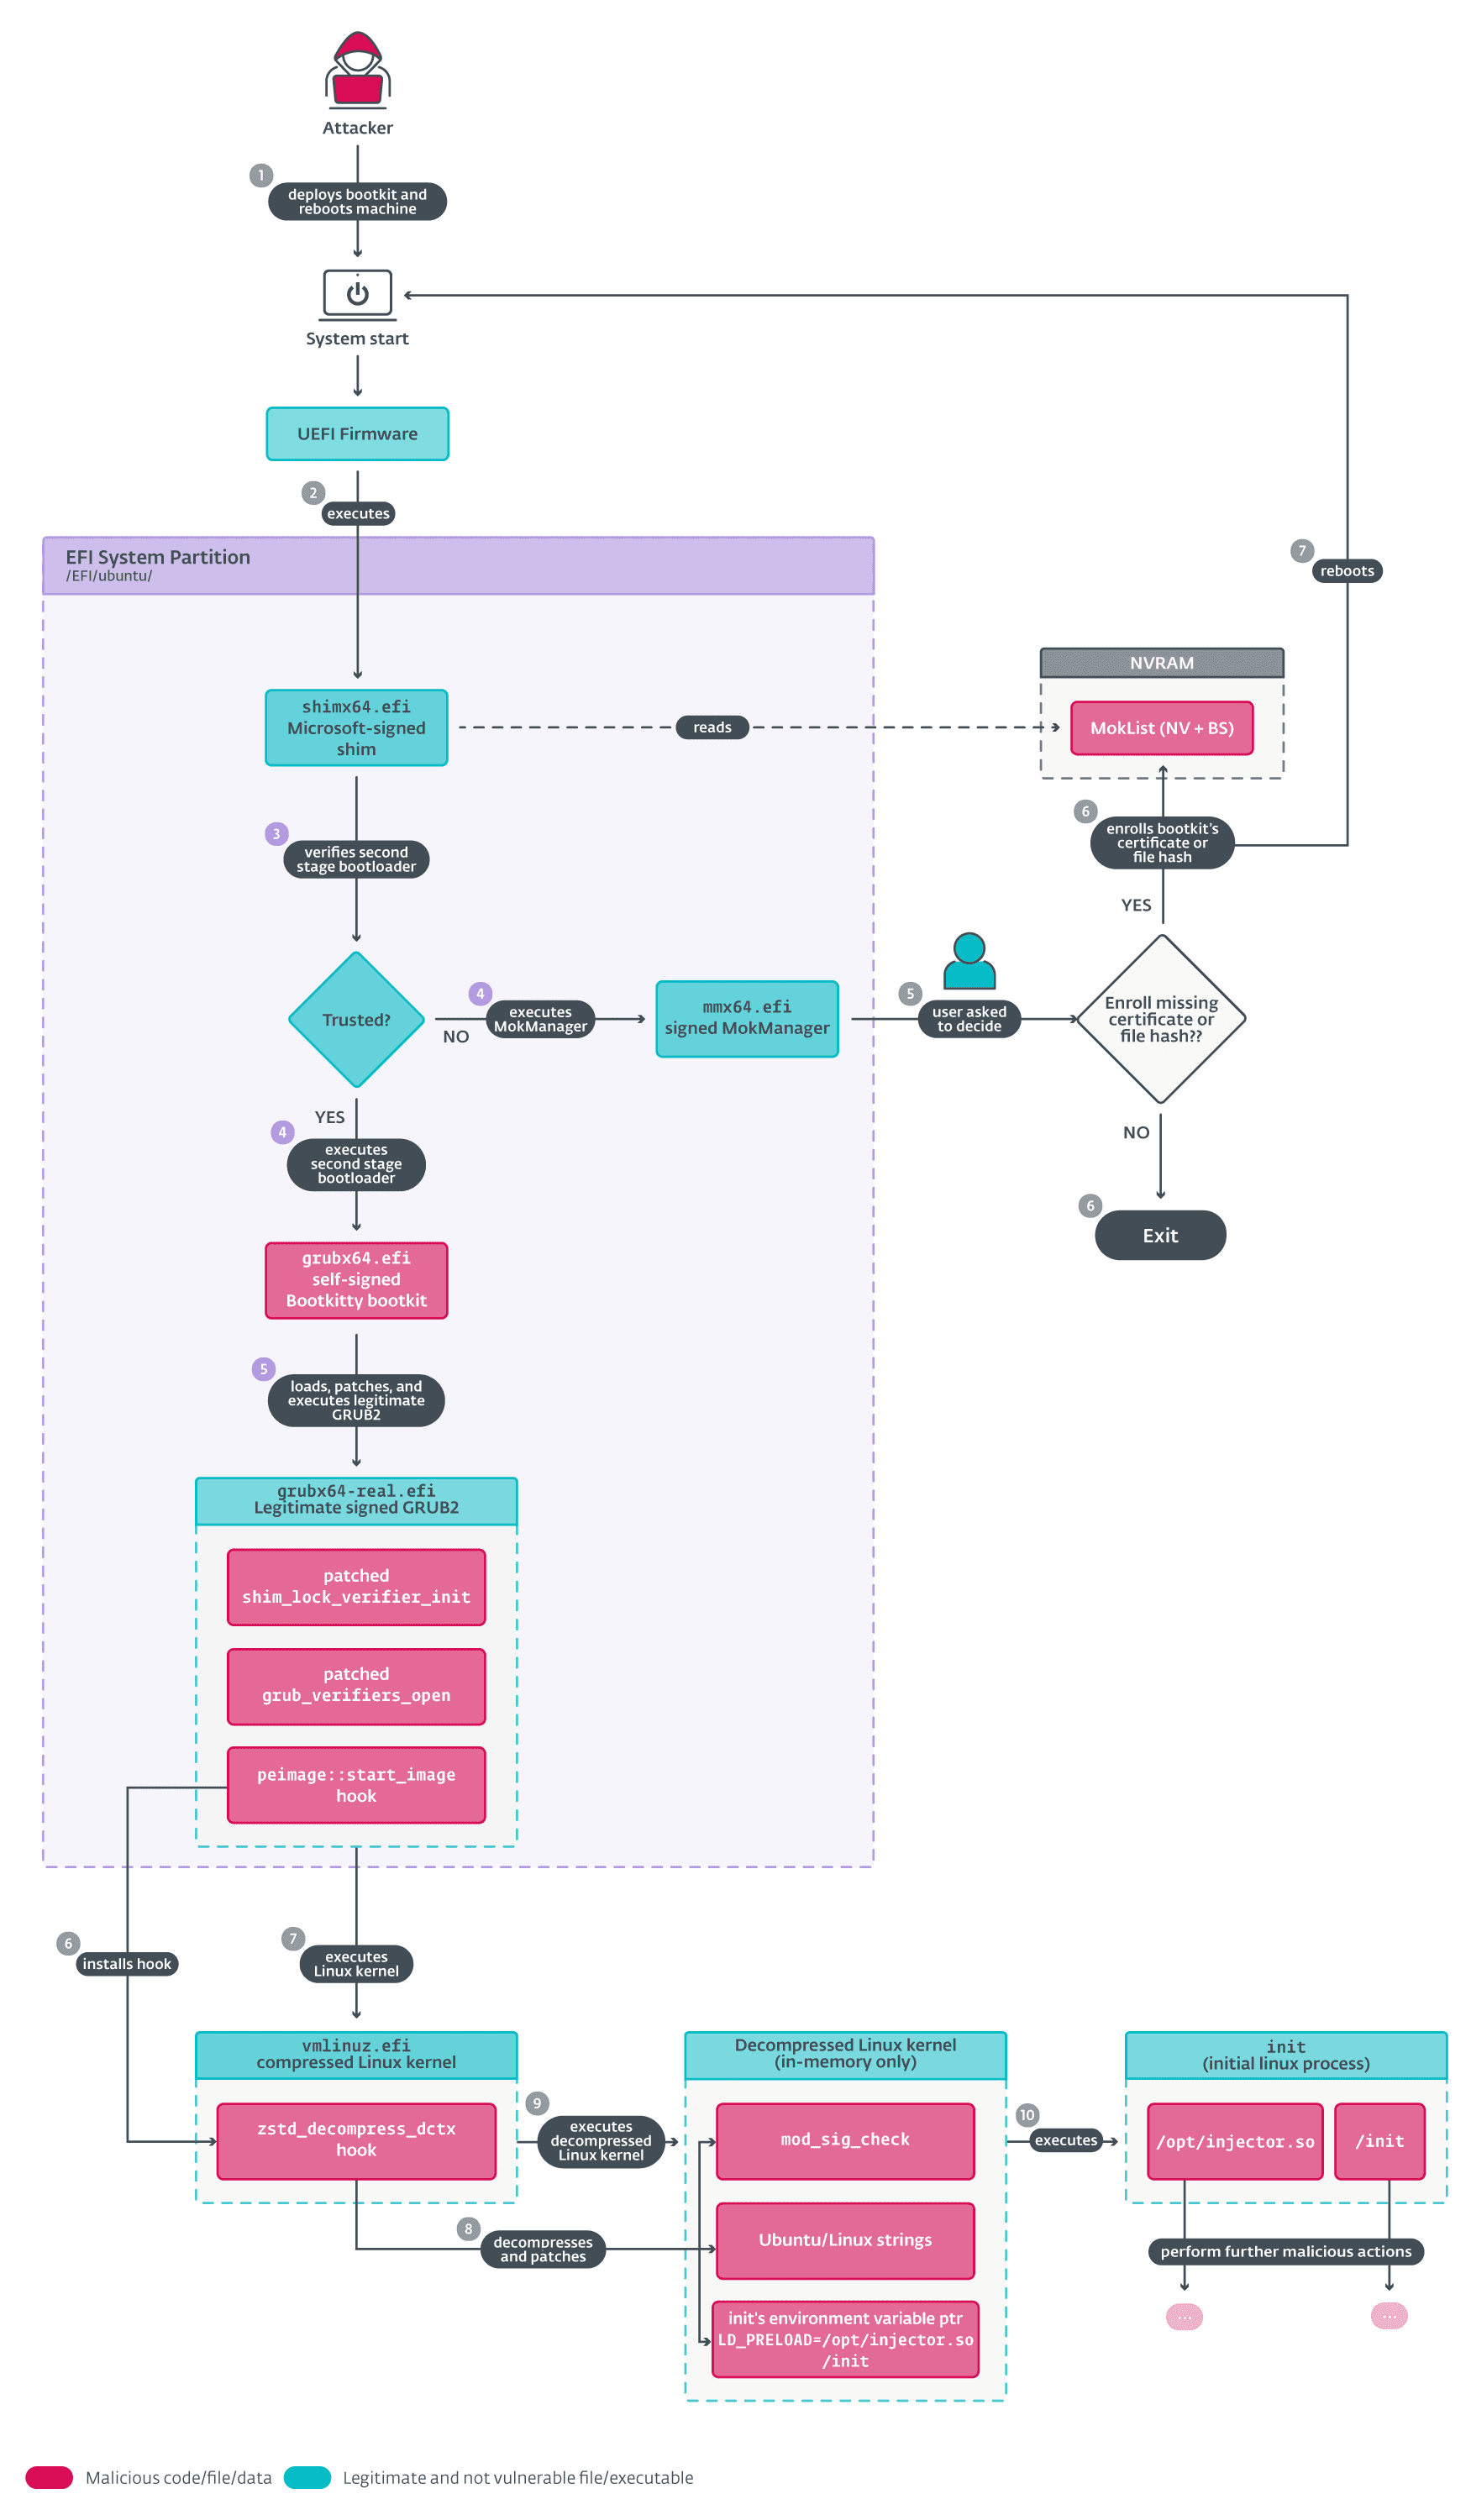
ESET discovered the first Unified Extensible Firmware Interface (UEFI) bootkit specifically designed for Linux systems, named Bootkitty.
Cybersecurity researchers from ESET discovered the first UEFI bootkit designed to target Linux systems, called by its authors Bootkitty.
The bootkit allows attackers to disable the kernel’s signature verification feature and to preload two as yet unknown ELF binaries via the Linux init process.
A previously unknown UEFI application, named bootkit.efi, was uploaded to VirusTotal in November 2024.
“Our initial analysis confirmed it is a UEFI bootkit, named Bootkitty by its creators and surprisingly the first UEFI bootkit targeting Linux, specifically, a few Ubuntu versions.” reads the advisory published by ESET. “Bootkitty is signed by a self-signed certificate, thus is not capable of running on systems with UEFI Secure Boot enabled unless the attackers certificates have been installed.”
The researchers noticed the many artifacts in bootkit.efi, suggesting that the binary is likely a proof of concept that was never used in attacks in the wild.
The authors signed Bootkitty with a self-signed certificate, thus the malware cannot run on systems with UEFI Secure Boot enabled unless the attackers’ certificates have been installed.
Bootkitty bypasses UEFI Secure Boot by patching integrity verification functions in memory, allowing seamless Linux kernel booting.
“Bootkitty is designed to boot the Linux kernel seamlessly, whether UEFI Secure Boot is enabled or not, as it patches, in memory, the necessary functions responsible for integrity verification before GRUB is executed.” continues the report.

Bootkitty supports a limited number of systems due to hardcoded byte patterns for function modification and fixed offsets for patching decompressed Linux kernels.
The bootkit hooks UEFI authentication functions to bypass the Secure Boot mechanism and patches GRUB boot loader functions to evade additional integrity verifications.
Alongside Bootkitty, researchers also discovered an unsigned kernel module, called BCDropper, likely developed by the same author. It features BlackCat references and unused file-hiding functionality, aligning with Bootkitty’s behavior of preloading /opt/injector.so.
“Whether a proof of concept or not, Bootkitty marks an interesting move forward in the UEFI threat landscape, breaking the belief about modern UEFI bootkits being Windows-exclusive threats. Even though the current version from VirusTotal does not, at the moment, represent a real threat to the majority of Linux systems, it emphasizes the necessity of being prepared for potential future threats.” concludes the report.
“To keep your Linux systems safe from such threats, make sure that UEFI Secure Boot is enabled, your system firmware and OS are up-to-date, and so is your UEFI revocations list.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, bootkit)


