
Hackers have stolen over $250,000 in Ethereum from Bored Ape Yacht Club (BAYC), this is the third security breach it suffered this year.
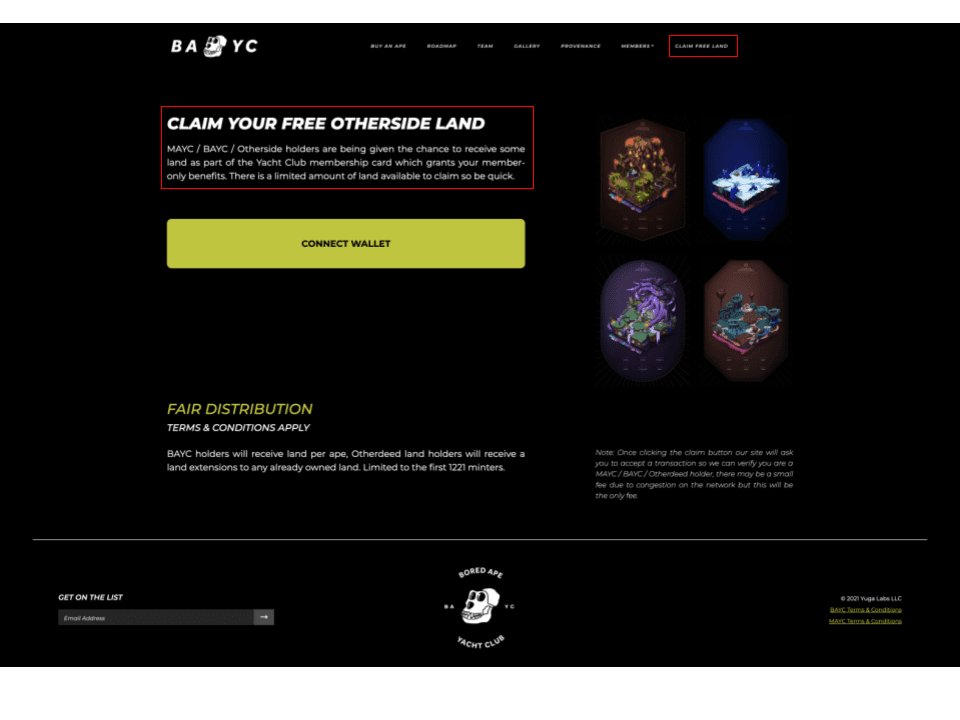
Threat actors compromised Bored Ape Yacht Club (BAYC) for the third time this year, they have stolen and sold NFTs, making away with 142 ETH, equivalent to over $250,000. The hacker conducted a phishing attack, they set up a phishing site that impersonated the official BAYC site claiming that BAYC, MAYC and OthersideMeta holders were able to claim a free NFT for a short period of time.
The website was advertised through the official BAYC Discord for a Yuga Labs community manager that was previously hackerd.
“CertiK analysis reveals that this community manager,
account –@BorisVagner (“BorisVagner | SBS” on Discord)– posted a message to BAYC’s
Discord server with a phishing link that led to the fake site. This then granted the scam the
appearance of authenticity and made it easier to dupe the NFT holders.” reads the analysis published by blockchain cybersecurity firm CertiK.

In the attack, the EOA related to the phishing site was identified as EOA 0x1079061D37f7F3FD3295E4aAd02EcE4a3f20DE2d OpenSea account (Now blocked).
Following the theft of NFTs, the attacker began to sell the collected assets at 08:25:42 AM UTC.
After selling off the stolen NFTs, threat actors moved the funds to the obfuscation platform
Tornado Cash.
This attack marks the third time the BAYC social media servers have been hacked by attackers this year. The first hack of the BAYC discord server took place on April 1st. On April 25th, BAYC was hit the victim of another phishing attack, threat actors compromised its Instagram account and stole 91 NFTs, equivalent to $1,345,472.34
At this time it is unclear how the attackers have hacked the community manager’s account.
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Zyxel)
[adrotate banner=”5″]
[adrotate banner=”13″]


