
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

BRATA, the Android RAT that infected only Brazilian users

Security experts at Kaspersky have spotted a new Android remote access tool (RAT) dubbed BRATA used to spy on Brazilian users. Security experts at Kaspersky have discovered a new Android remote access tool (RAT), tracked as BRATA (the name comes from ‘Brazilian RAT Android’), that was used to spy on Brazilian users. The BRATA RAT […]

brata rat

Security experts at Kaspersky have spotted a new Android remote access tool (RAT) dubbed BRATA used to spy on Brazilian users.

Security experts at Kaspersky have discovered a new Android remote access tool (RAT), tracked as BRATA (the name comes from ‘Brazilian RAT Android’), that was used to spy on Brazilian users. The BRATA RAT was first detected in January while spreading via WhatsApp and SMS messages

““BRATA” is a new Android remote access tool malware family. We used this code name based on its description – “Brazilian RAT Android”. It exclusively targets victims in Brazil: however, theoretically it could also be used to attack any other Android user if the cybercriminals behind it want to.” reads the analysis from Kaspersky. “It has been widespread since January 2019, primarily hosted in the Google Play store, but also found in alternative unofficial Android app stores. For the malware to function correctly, it requires at least Android Lollipop 5.0 version. “

The RAT was delivered through the official Google Play Store and also via unofficial Android app stores. The experts have already discovered more than 20 unique BRATA variants in Android apps on the Play Store.

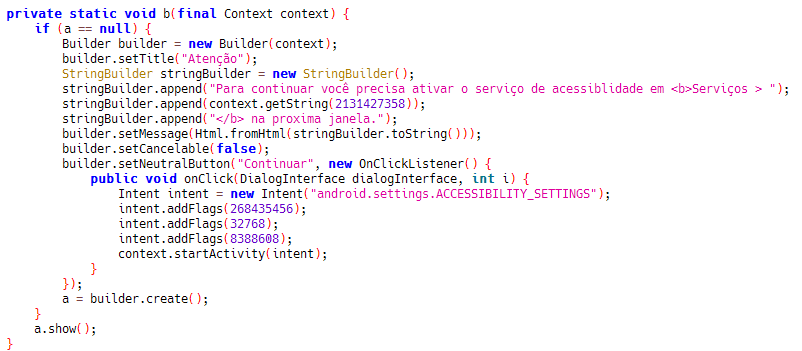
Most of the tainted apps pose as an update to the popular instant messaging application WhatsApp that would address the CVE-2019-3568 flaw in the instant messaging application. Once the malware has infected the victim’s device, it will start keylogging feature, enhancing it with real-time streaming functionality. The malware leverages the Android Accessibility Service feature to interact with other applications installed on the victim’s device.

brata rat

“The cybercriminals behind BRATA use few infection vectors. For example, they use push notifications on compromised websites; and also spread it using messages delivered via WhatsApp or SMS, and sponsored links in Google searches.” continues the report.

BRATA supports many commands, such as unlocking the victims’ devices, collecting device information, turning off the device’s screen to surreptitiously run tasks in the background, executing any particular application and uninstall itself and removes any infection traces.

“It is worth mentioning that the infamous fake WhatsApp update registered over 10,000 downloads in the official Google Play Store, reaching up to 500 victims per day.” concludes Kaspersky.

The report includes indicators of compromise (IOCs) for the BRATA RAT malware.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs  BRATA RAT, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


